Skip to content
Artwork for Cybersecurity Tech Brief By HackerNoon
TechnologyNewsTech News

Cybersecurity Tech Brief By HackerNoon

HackerNoon

Learn the latest Cybersecurity updates in the tech world.

Play
  • 86 episodes
  • Avg 11 min
  • English
Counted on this page — what you have heard stays on this device, so it is not something the list can be paged by.
  • September 9 · 14 min

    Modernizing Threat Monitoring and Detection Engineering for Ultimate MTTR Reduction

    This story was originally published on HackerNoon at: https://hackernoon.com/modernizing-threat-monitoring-and-detection-engineering-for-ultimate-mttr-reduction. Learn how threat intelligence connects monitoring and detection engineering to help SOC teams reduce alert noise, improve detection, and respond faster. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #threat-intelligence, #soc-threat-monitoring, #soc-operations, #proactive-threat-detection, #mssp-threat-monitoring, #intelligence-driven-soc, #threat-intelligence-feeds, #good-company, and more. This story was written by: @anyrun. Learn more about this writer by checking @anyrun's about page, and for more stories, please visit hackernoon.com. Modern SOCs need more than continuous log collection. This guide explains how threat monitoring, detection engineering, and threat intelligence work together as a continuous operational loop. It covers live intelligence feeds, behavioral threat hunting, YARA rule creation, emerging threat research, and unified workflows that help SOC teams reduce false positives, close detection gaps, improve analyst efficiency, and move from reactive incident response toward proactive defense.
  • September 8 · 11 min

    A Green Import Report Is Not a CRM Cutover Test

    This story was originally published on HackerNoon at: https://hackernoon.com/a-green-import-report-is-not-a-crm-cutover-test. Six evidence checks for CRM cutovers: identity, relationships, automation, access, reporting, and recovery. Includes a worked reconciliation example. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #disaster-recovery, #crm-migration, #data-migration, #hubspot, #software-testing, #data-integrity, #enterprise-software, #revops, and more. This story was written by: @mrpratikthakker. Learn more about this writer by checking @mrpratikthakker's about page, and for more stories, please visit hackernoon.com. Matching record totals do not prove a CRM migration is safe. Validate six layers using explicit expected results, record-level reconciliation, negative permission tests, and a recovery rehearsal. Treat the final go-live decision as an evidence review, not a progress update.

  • September 8 · 6 min

    Post-Quantum Cryptography and India’s Digital Public Infrastructure

    This story was originally published on HackerNoon at: https://hackernoon.com/post-quantum-cryptography-and-indias-digital-public-infrastructure. India’s Aadhaar, UPI, and DigiLocker systems may need crypto-agility and post-quantum migration as quantum computing risks grow. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #post-quantum-cryptography, #digital-public-infrastructure, #upi-encryption, #digilocker-security, #national-quantum-mission-india, #crypto-agility, #quantum-safe-encryption, #post-quantum-planning, and more. This story was written by: @sam-matrix. Learn more about this writer by checking @sam-matrix's about page, and for more stories, please visit hackernoon.com. The article argues that India’s digital public infrastructure needs early post-quantum planning, including hybrid cryptography, crypto-agile PKI/HSM upgrades, testing, certification, and prioritization of sensitive identity and payment systems.

  • September 7 · 5 min

    8 Timer Implementation Patterns for Systems and Network Software

    This story was originally published on HackerNoon at: https://hackernoon.com/8-timer-implementation-patterns-for-systems-and-network-software. A practical guide to system-side timer patterns, from hardware interrupts and OS APIs to timer wheels, heaps, polling, and event loops. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #networking, #system-timers, #timer-architecture, #linux-timers, #network-protocol-timers, #bgp-hold-timers, #event-loop, #kernel-timers, and more. This story was written by: @vijayananda. Learn more about this writer by checking @vijayananda's about page, and for more stories, please visit hackernoon.com. System-side timers can be built in eight different ways — from hardware interrupts and OS APIs to timer wheels, heaps, and event loops. This article breaks down each approach and explains why timer wheels and event-loop-integrated timers (like libevent or epoll/timerfd) are the go-to choices for production networking software handling thousands of concurrent sessions, such as BGP or tunnel keepalives.

  • September 7 · 18 min

    Enterprise Networks Know Who Connected. AI Agents Make the “Why” Harder

    This story was originally published on HackerNoon at: https://hackernoon.com/enterprise-networks-know-who-connected-ai-agents-make-the-why-harder. AI agents complicate enterprise trust because identity alone cannot explain intent, delegated authority, or why a connection happened. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #networking, #network-identity, #ai-agents, #zero-trust, #enterprise-security, #ai-observability, #identity-and-access-management, #machine-identity, and more. This story was written by: @kgsr2194. Learn more about this writer by checking @kgsr2194's about page, and for more stories, please visit hackernoon.com. The article argues that AI agents will stretch enterprise identity models. Knowing who an agent is will not be enough; infrastructure will also need context about authority, delegation, task scope, and intent.

  • September 5 · 49 min

    Where the Cybersecurity Market Is Actually Moving in 2026

    This story was originally published on HackerNoon at: https://hackernoon.com/where-the-cybersecurity-market-is-actually-moving-in-2026. A study of 77 cybersecurity vendors reveals how AI Security, Identity, Exposure Management, DSPM, DSA, and PQC are evolving. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #cybersecurity, #infosecurity, #ai-security, #market-research, #security-architecture, #forecasting, #security, #hackernoon-top-story, and more. This story was written by: @yuriybutuzov. Learn more about this writer by checking @yuriybutuzov's about page, and for more stories, please visit hackernoon.com. A study of 77 cybersecurity vendors reveals how AI Security, Identity, Exposure Management, DSPM, DSA, and PQC are evolving.

  • September 5 · 15 min

    Best Autonomous Pentesting Tools for 2026

    This story was originally published on HackerNoon at: https://hackernoon.com/best-autonomous-pentesting-tools-for-2026. Stop guessing with scanners. Discover 7 autonomous pentesting tools that chain real exploits. Compare web, API, and network security leaders for 2026. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #pentesting, #pentesting-tools, #pentesting-ai-tool, #autonomous-pentesting, #cybersecurity, #cyberattacks, #offensive-security, #good-company, and more. This story was written by: @stevebeyatte. Learn more about this writer by checking @stevebeyatte's about page, and for more stories, please visit hackernoon.com. Stop guessing with scanners. Discover 7 autonomous pentesting tools that chain real exploits. Compare web, API, and network security leaders for 2026.

  • September 4 · 9 min

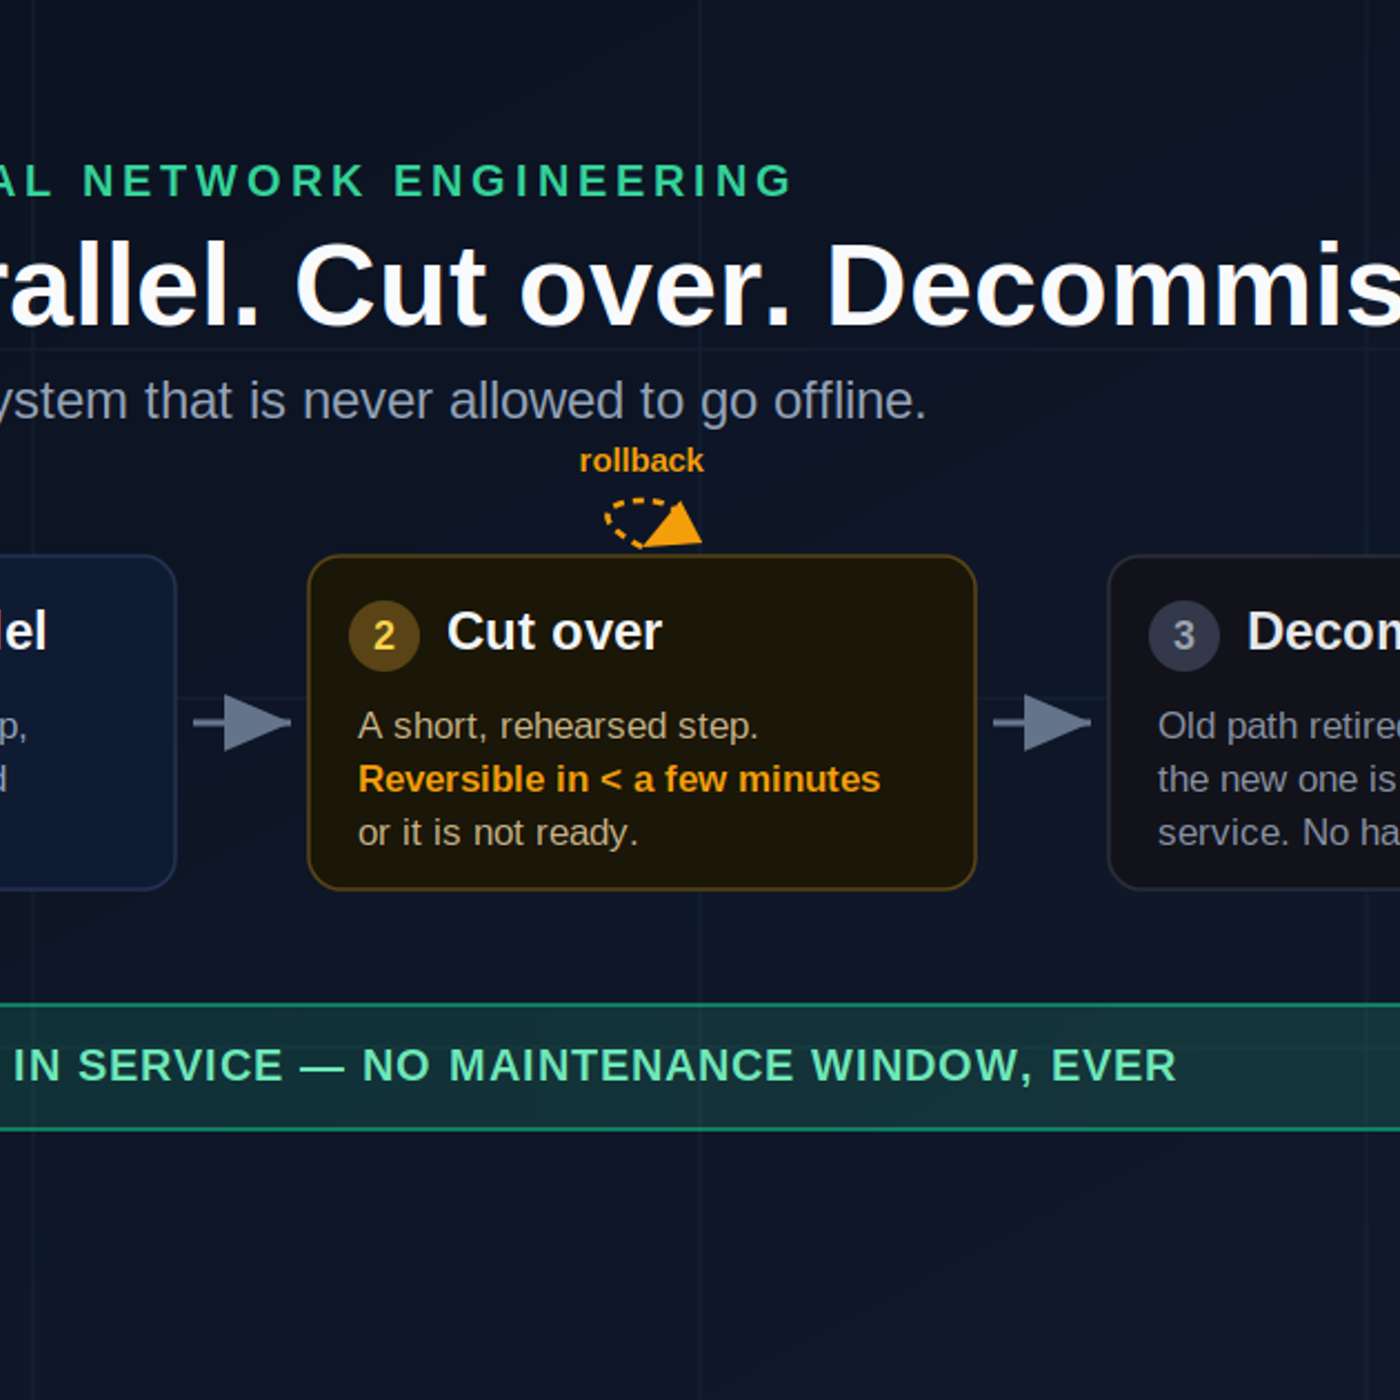
    What It Actually Takes to Network a Live System That's Never Allowed to Go Offline

    This story was originally published on HackerNoon at: https://hackernoon.com/what-it-actually-takes-to-network-a-live-system-thats-never-allowed-to-go-offline. Lessons from building transit networks that can never go offline: addressing as a 20-year decision, blast-radius switch design, and testing by breaking things. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #networking, #system-design, #site-reliability-engineering, #infrastructure, #resilience, #building-networks, #public-transit-system, #intercom, and more. This story was written by: @savni. Learn more about this writer by checking @savni's about page, and for more stories, please visit hackernoon.com. I've spent over a decade building networks for a public transit system that's almost never allowed to go offline — surveillance, public address, intercom, and emergency comms running while trains keep moving underneath. That single "no maintenance window" constraint reshapes every decision: addressing schemes become twenty-year commitments, switch configuration becomes a blast-radius problem, and the acceptance test becomes the real deliverable. Here's what mission-critical network engineering actually takes when "down" means a passenger presses a call button and nobody answers.

  • September 4 · 5 min

    A Six-Day Intrusion in March Became 3.7 Million Patients in August

    This story was originally published on HackerNoon at: https://hackernoon.com/a-six-day-intrusion-in-march-became-37-million-patients-in-august. CareCloud's breach count went from roughly 350,000 to 3,756,469 — five months after a six-day intrusion. The gap is a data-lineage problem, not a PR one. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #data-breach, #healthcare-security, #incident-response, #cloud-security, #cybersecurity, #healthcare-cybersecurity, #cyber-attack, #hipaa, and more. This story was written by: @nickmarsteller. Learn more about this writer by checking @nickmarsteller's about page, and for more stories, please visit hackernoon.com. CareCloud told federal regulators this week that 3,756,469 people were affected by a March breach of an AWS environment. The figure was first reported as roughly 350,000. The gap between those two numbers is the part worth studying.

  • September 3 · 20 min

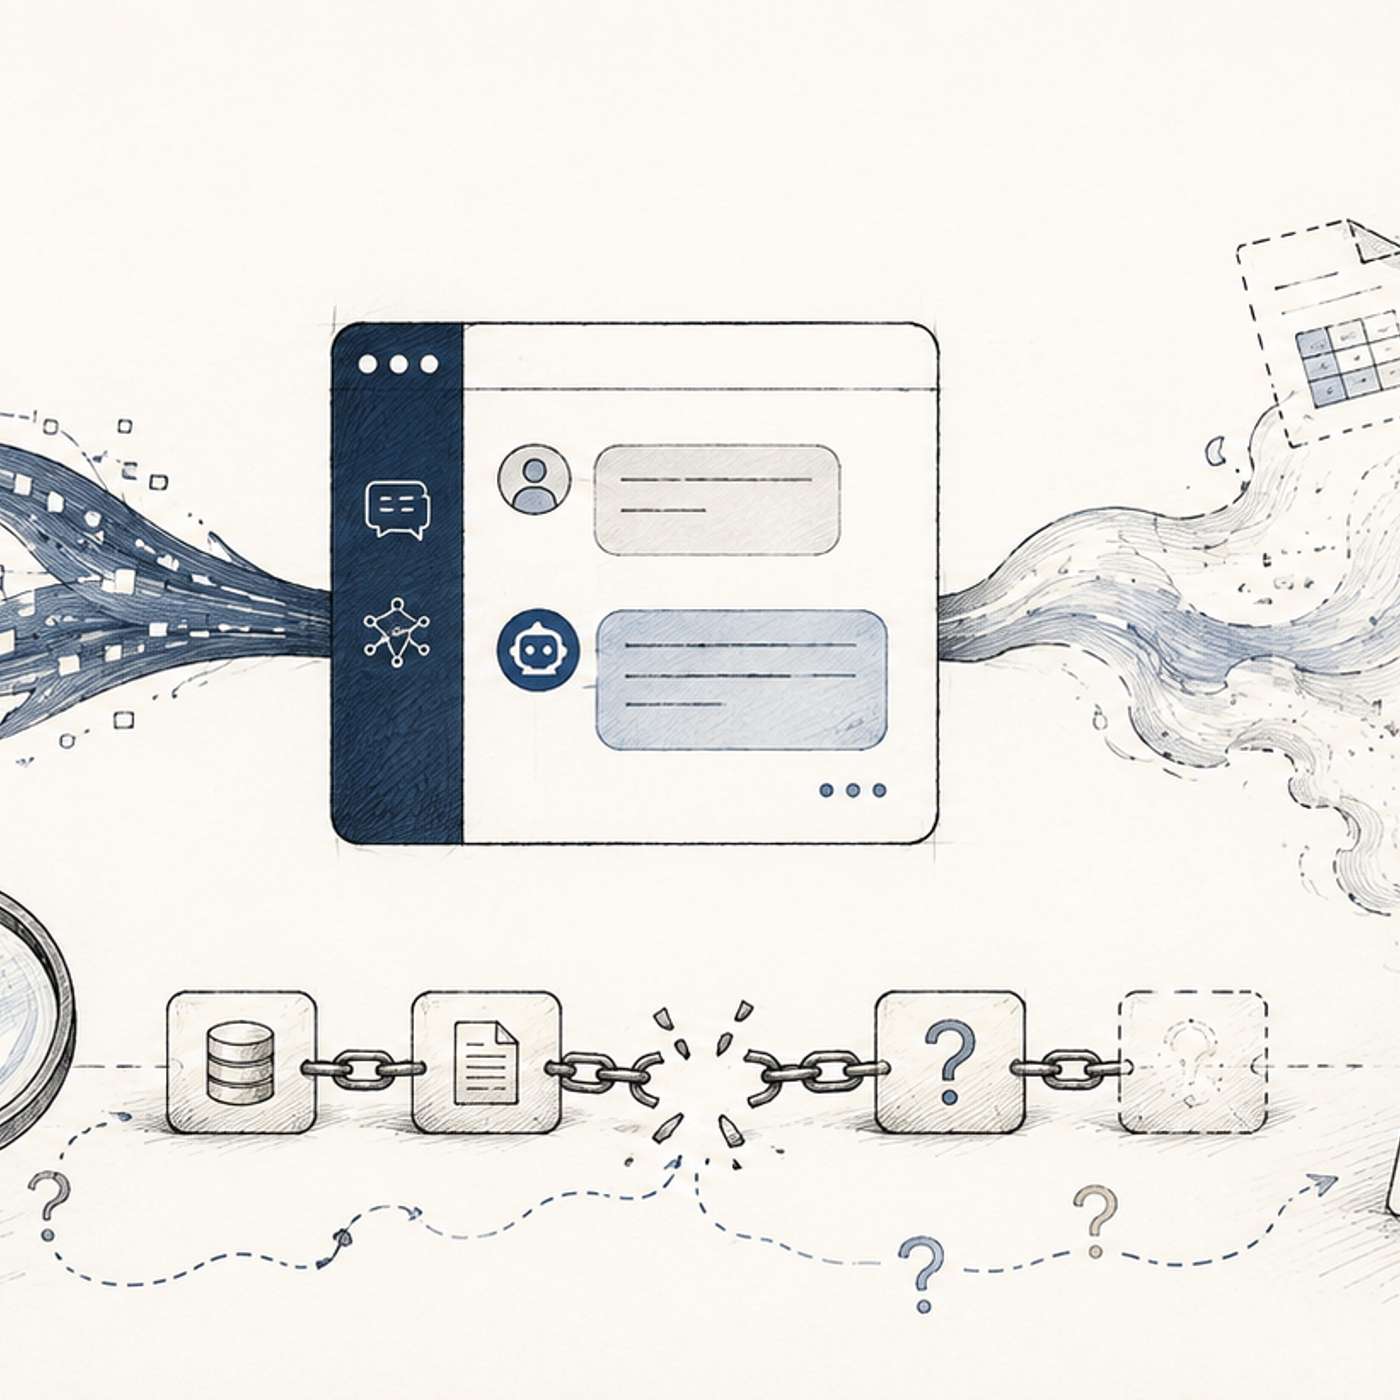
    When an AI Cannot Tell a Leak from a Hallucination: A Multi-Model Guardrail Case Study

    This story was originally published on HackerNoon at: https://hackernoon.com/when-an-ai-cannot-tell-a-leak-from-a-hallucination-a-multi-model-guardrail-case-study. A firsthand multi-model AI security case study on real account memory, simulated tools, hallucinated secrets, and broken provenance across AI workflows today. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #cybersecurity, #artificial-intelligence, #ai-security, #llm-security, #generative-ai, #prompt-injection, #ai-hallucinations, #responsible-disclosure, and more. This story was written by: @cyber-octopus. Learn more about this writer by checking @cyber-octopus's about page, and for more stories, please visit hackernoon.com. I tested AI Fiesta’s multi-model workflow to see how it separated system instructions, account memory, simulated tools and generated output. The models exposed instruction-like content, surfaced genuine account context, produced realistic security artifacts and then contradicted each other about whether those artifacts were real or simulated. The core issue wasn’t a confirmed leak but the broken provenance.

  • September 3 · 8 min

    SonarQube Hunter Agent is Now GA: Catch Broken Access Control and Business Logic Flaws

    This story was originally published on HackerNoon at: https://hackernoon.com/sonarqube-hunter-agent-is-now-ga-catch-broken-access-control-and-business-logic-flaws. SonarQube Hunter Agent uses AI reasoning to find broken access control, business logic flaws, and security bugs traditional SAST tools miss. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #cybersecurity, #authentication, #finance, #programming, #artificial-intelligence, #business, #sonarqube-hunter-agent, #good-company, and more. This story was written by: @sonarsource. Learn more about this writer by checking @sonarsource's about page, and for more stories, please visit hackernoon.com. SonarQube Hunter Agent uses AI reasoning to find broken access control, business logic flaws, and security bugs traditional SAST tools miss.

  • September 2 · 6 min

    Bright Security Expands its AI SDLC security Platform & Launches an AI PT Module

    This story was originally published on HackerNoon at: https://hackernoon.com/bright-security-expands-its-ai-sdlc-security-platform-and-launches-an-ai-pt-module. Bright Security Expands AI SDLC Security Platform, Launches AI PT: AI-Powered Penetration Testing That Cuts Weeks Down to Hours Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #cybersecurity, #ai, #cybernewswire, #press-release, #cyber-threats, #cyber-security-awareness, #cybersecurity-tips, #good-company, and more. This story was written by: @cybernewswire. Learn more about this writer by checking @cybernewswire's about page, and for more stories, please visit hackernoon.com.

  • September 2 · 19 min

    Pixel 11 Drops Hardware Memory Tagging and GrapheneOS May Skip It Entirely

    This story was originally published on HackerNoon at: https://hackernoon.com/pixel-11-drops-hardware-memory-tagging-and-grapheneos-may-skip-it-entirely. Pixel 11 drops ARM Memory Tagging Extension, a key hardware security feature. Here’s why GrapheneOS calls it a serious security regression. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #cybersecurity, #android, #google-pixel-11, #mobile-security, #memory-safety, #graphene-os, #privacy, #hardware-security, and more. This story was written by: @davidtimothy. Learn more about this writer by checking @davidtimothy's about page, and for more stories, please visit hackernoon.com. The Pixel 11 drops ARM Memory Tagging Extension (MTE), a hardware-level defense against memory corruption exploits. GrapheneOS says the missing feature is serious enough that it may skip the entire Pixel 11 generation. Google’s new security features, including post-quantum crypto, don’t replace MTE’s protection against today’s memory attacks. The Pixel 11 isn’t suddenly insecure, but losing MTE without an equivalent replacement is a clear security step backward.

  • September 1 · 6 min

    Why Pentesting Teams are Drowning in Tools

    This story was originally published on HackerNoon at: https://hackernoon.com/why-pentesting-teams-are-drowning-in-tools. Pentesting teams are juggling more tools than ever. Learn how fragmented workflows create inefficiency and why centralized pentest management matters. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #pentesting, #cybersecurity, #pentest-management, #pentesting-tools, #penetration-testing, #pentest-platform, #pentest-workflow, #pentest-tool-sprawl, and more. This story was written by: @anthonylucas. Learn more about this writer by checking @anthonylucas's about page, and for more stories, please visit hackernoon.com. Pentesting teams are juggling more tools than ever. Learn how fragmented workflows create inefficiency and why centralized pentest management matters.

  • September 1 · 9 min

    5 Big Crypto Crimes Solved by Chain Transparency —The Last One Saved Lives

    This story was originally published on HackerNoon at: https://hackernoon.com/5-big-crypto-crimes-solved-by-chain-transparency-the-last-one-saved-lives. Five real crypto crimes, one common clue: chain transparency. See how public ledgers helped investigators follow the money and crack the cases. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #crypto-crime, #crypto-hacks, #crypto-security, #on-chain-transactions, #public-blockchain, #obyte, #good-company, #hackernoon-top-story, and more. This story was written by: @obyte. Learn more about this writer by checking @obyte's about page, and for more stories, please visit hackernoon.com. Five real crypto crimes, one common clue: chain transparency. See how public ledgers helped investigators follow the money and crack the cases.

  • August 27 · 5 min

    Why I Built a Password Manager That Never Touches the Cloud

    This story was originally published on HackerNoon at: https://hackernoon.com/why-i-built-a-password-manager-that-never-touches-the-cloud. Kryptix removes accounts, telemetry, and cloud sync from password management while offering encrypted backups, biometrics, and auditable code. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #passwords, #security, #data-security, #password-security, #offline, #react-native, #password-manager, #data-privacy, and more. This story was written by: @nima01. Learn more about this writer by checking @nima01's about page, and for more stories, please visit hackernoon.com. Kryptix removes accounts, telemetry, and cloud sync from password management while offering encrypted backups, biometrics, and auditable code.

  • August 27 · 5 min

    Inside Xalgorix: An AI Pentester Built Around Exploit Verification

    This story was originally published on HackerNoon at: https://hackernoon.com/inside-xalgorix-an-ai-pentester-built-around-exploit-verification. Xalgorix is an open-source AI pentester that separates vulnerability discovery from independent exploit verification. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #cybersecurity, #devsecops, #open-source, #penetration-testing, #application-security, #security-testing, #artificial-intelligence, #ai-agents, and more. This story was written by: @xalgord. Learn more about this writer by checking @xalgord's about page, and for more stories, please visit hackernoon.com. Xalgorix is an open-source, self-hosted AI pentester whose independent verifier re-exploits candidate findings before they are reported.

  • August 26 · 5 min

    When an Expired Domain Becomes a Security Problem

    This story was originally published on HackerNoon at: https://hackernoon.com/when-an-expired-domain-becomes-a-security-problem. Old domains can retain backlinks, references, integrations and digital history long after their original owners stop using them. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #cybersecurity, #infosec, #web-security, #dns, #web-domains, #expired-domains, #domain-security, #cybersecurity-awareness, and more. This story was written by: @cyberbezpieczenstwo. Learn more about this writer by checking @cyberbezpieczenstwo's about page, and for more stories, please visit hackernoon.com. Expired domains aren't just an SEO asset — they can become a cybersecurity risk. Old domains may still be referenced in documentation, DNS, email systems, APIs and external websites. If someone else registers the domain, that forgotten digital footprint can potentially be abused. Organizations should treat domain retirement as part of their security lifecycle and audit dependencies before allowing a domain to expire.

  • August 25 · 17 min

    62 Blog Posts To Learn About Network

    This story was originally published on HackerNoon at: https://hackernoon.com/62-blog-posts-to-learn-about-network. Learn everything you need to know about Network via these 62 free HackerNoon blog posts. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #network, #learn, #learn-network, and more. This story was written by: @learn. Learn more about this writer by checking @learn's about page, and for more stories, please visit hackernoon.com.

  • August 25 · 18 min

    Claude Code Hooks: How to Stop AI Agents From Breaking Your Code

    This story was originally published on HackerNoon at: https://hackernoon.com/claude-code-hooks-how-to-stop-ai-agents-from-breaking-your-code. Learn how Claude Code hooks create deterministic guardrails that block dangerous commands and verify AI-generated code before problems ship. Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity. You can also check exclusive content about #cybersecurity, #docker, #large-language-models, #programming, #api, #artificial-intelligence, #claude-code-hooks, #good-company, and more. This story was written by: @sonarsource. Learn more about this writer by checking @sonarsource's about page, and for more stories, please visit hackernoon.com. Learn how Claude Code hooks create deterministic guardrails that block dangerous commands and verify AI-generated code before problems ship.

Showing 41–60 of 86 episodes