Skip to content
Artwork for CyberCode Academy
CyberCode Academy · Yesterday · 17 min

Course 43 - Practical Malware Development | Episode 7: Building a PHP Session Control Panel

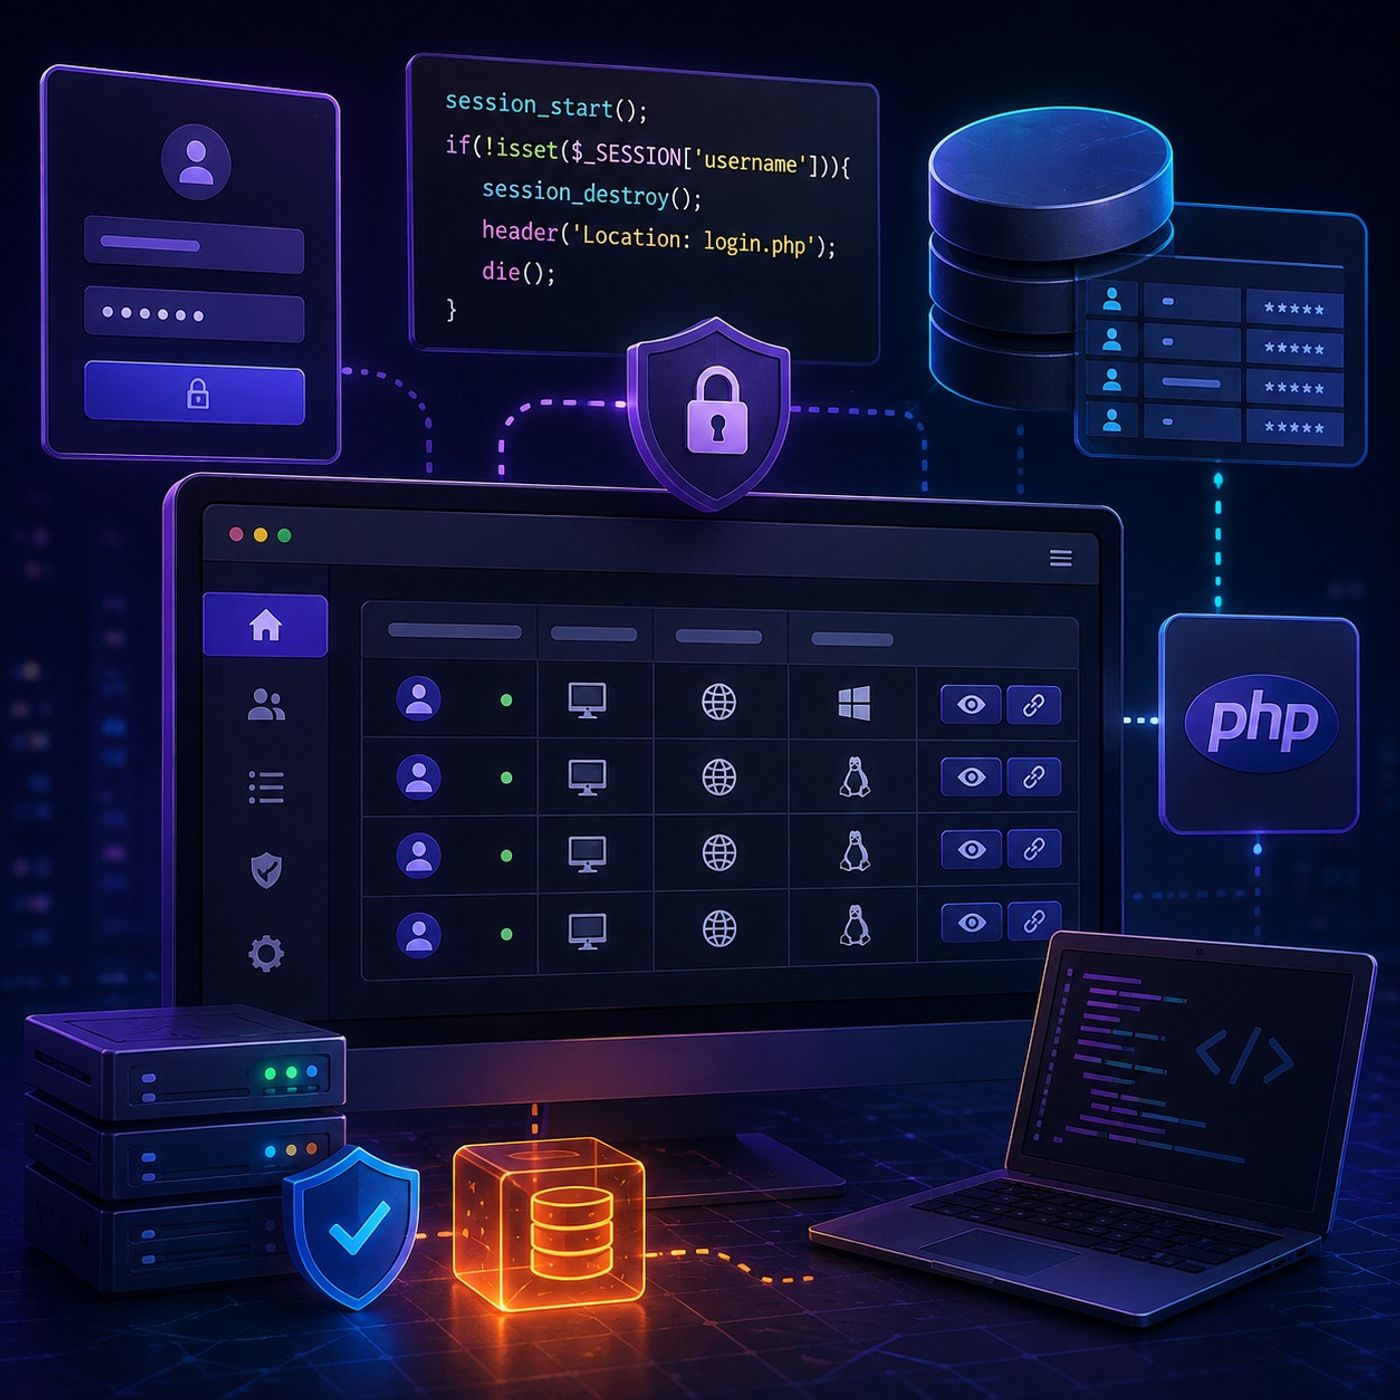
This episode, we continue developing our PHP-based control panel by moving beyond authentication and building the authenticated administration layer.We begin by establishing administrator credentials, then implement a dedicated session-protection mechanism to secure private pages. Finally, we transform the control panel into a dynamic dashboard capable of retrieving database records and presenting them through a structured web interface.The episode demonstrates how authentication, session management, database queries, and dynamic HTML generation come together to create a functional administrative backend.1. Creating Administrator CredentialsWe start by creating the primary administrator account within the users table.Using MySQL's INSERT INTO statement, we add the required authentication information and examine how password values can be transformed before being stored in the database.The episode uses the MD5() function as part of the original implementation while also emphasizing an important security consideration: MD5 is obsolete for password storage and should be replaced with a modern password-hashing algorithm in production applications.2. Building the Session Security LayerNext, we create a dedicated authentication guard named session.php.This component protects private control-panel pages by: Starting the PHP session with session_start(). Checking whether the expected session username exists. Identifying unauthenticated access attempts. Destroying invalid sessions. Redirecting unauthorized users away from protected pages. Using die() to immediately terminate script execution after the redirect. The final step is particularly important because redirecting a browser alone does not automatically stop the current PHP script from continuing to execute. Terminating execution ensures that protected content is not subsequently rendered to an unauthorized requester.3. Creating the Dynamic DashboardWith authentication and session protection in place, we build the main administrative interface in index.php.The dashboard integrates the existing PHP database connection and retrieves records from the victims table.We use PHP's database functionality to: Execute the required database query. Iterate through returned records with a while loop. Extract individual fields using fetch_assoc(). Retrieve information such as Host Name, IP Address, and Operating System. Dynamically generate HTML based on the database contents. This transforms the dashboard from a static page into a real-time interface driven by database records.4. Designing the Data TableThe retrieved records are presented through a custom-styled HTML table.The table provides a structured view of the information stored in the database, making it easier for an administrator to review individual records through the web interface.We also introduce dynamic HTML generation, allowing PHP to populate the table automatically as new database records become available.5. Adding Administrative ActionsFinally, we create a dynamically generated clickable action link for each individual record.Each link is associated with the corresponding database entry and routes the administrator toward a dedicated management page.This establishes the foundation for a more advanced administrative workflow where individual records can later be inspected and managed through dedicated controls.Overall ArchitectureThe completed workflow can be summarized as:Administrator Credentials → Login Authentication → PHP Session → Session Validation → Database Query → Dynamic Dashboard → Individual Management ActionsThis architecture demonstrates how authentication and database-driven interfaces can be combined into a functional PHP administration system.Key TakeawaysBy the end of this episode, you will understand how to: Create administrator credentials within MySQL. Understand the limitations of legacy MD5 password hashing. Build a reusable PHP session-protection mechanism. Protect private pages against unauthenticated access. Terminate unauthorized PHP execution with die(). Retrieve database records dynamically with PHP. Process MySQL results using fetch_assoc(). Generate HTML tables from database records. Create dynamic links for individual database entries. Structure an authenticated PHP administration dashboard. The techniques presented throughout the episode provide a practical foundation for understanding web authentication, session security, database-driven interfaces, and secure backend architecture. You can listen and download our episodes for free on more than 10 different platforms: https://linktr.ee/cybercode_academy

0:00-17:30

transcript

No transcript — this publisher did not publish one.

show notes

This episode, we continue developing our PHP-based control panel by moving beyond authentication and building the authenticated administration layer.We begin by establishing administrator credentials, then implement a dedicated session-protection mechanism to secure private pages. Finally, we transform the control panel into a dynamic dashboard capable of retrieving database records and presenting them through a structured web interface.The episode demonstrates how authentication, session management, database queries, and dynamic HTML generation come together to create a functional administrative backend.1. Creating Administrator CredentialsWe start by creating the primary administrator account within the users table.Using MySQL's INSERT INTO statement, we add the required authentication information and examine how password values can be transformed before being stored in the database.The episode uses the MD5() function as part of the original implementation while also emphasizing an important security consideration: MD5 is obsolete for password storage and should be replaced with a modern password-hashing algorithm in production applications.2. Building the Session Security LayerNext, we create a dedicated authentication guard named session.php.This component protects private control-panel pages by:
  • Starting the PHP session with session_start().
  • Checking whether the expected session username exists.
  • Identifying unauthenticated access attempts.
  • Destroying invalid sessions.
  • Redirecting unauthorized users away from protected pages.
  • Using die() to immediately terminate script execution after the redirect.
The final step is particularly important because redirecting a browser alone does not automatically stop the current PHP script from continuing to execute. Terminating execution ensures that protected content is not subsequently rendered to an unauthorized requester.3. Creating the Dynamic DashboardWith authentication and session protection in place, we build the main administrative interface in index.php.The dashboard integrates the existing PHP database connection and retrieves records from the victims table.We use PHP's database functionality to:
  • Execute the required database query.
  • Iterate through returned records with a while loop.
  • Extract individual fields using fetch_assoc().
  • Retrieve information such as Host Name, IP Address, and Operating System.
  • Dynamically generate HTML based on the database contents.
This transforms the dashboard from a static page into a real-time interface driven by database records.4. Designing the Data TableThe retrieved records are presented through a custom-styled HTML table.The table provides a structured view of the information stored in the database, making it easier for an administrator to review individual records through the web interface.We also introduce dynamic HTML generation, allowing PHP to populate the table automatically as new database records become available.5. Adding Administrative ActionsFinally, we create a dynamically generated clickable action link for each individual record.Each link is associated with the corresponding database entry and routes the administrator toward a dedicated management page.This establishes the foundation for a more advanced administrative workflow where individual records can later be inspected and managed through dedicated controls.Overall ArchitectureThe completed workflow can be summarized as:Administrator Credentials → Login Authentication → PHP Session → Session Validation → Database Query → Dynamic Dashboard → Individual Management ActionsThis architecture demonstrates how authentication and database-driven interfaces can be combined into a functional PHP administration system.Key TakeawaysBy the end of this episode, you will understand how to:
  • Create administrator credentials within MySQL.
  • Understand the limitations of legacy MD5 password hashing.
  • Build a reusable PHP session-protection mechanism.
  • Protect private pages against unauthenticated access.
  • Terminate unauthorized PHP execution with die().
  • Retrieve database records dynamically with PHP.
  • Process MySQL results using fetch_assoc().
  • Generate HTML tables from database records.
  • Create dynamic links for individual database entries.
  • Structure an authenticated PHP administration dashboard.
The techniques presented throughout the episode provide a practical foundation for understanding web authentication, session security, database-driven interfaces, and secure backend architecture.

You can listen and download our episodes for free on more than 10 different platforms:
https://linktr.ee/cybercode_academy
links1