Skip to content
Artwork for CyberCode Academy
CyberCode Academy · Yesterday · 21 min

Course 43 - Practical Malware Development | Episode 6: Database Foundations and PHP Integration

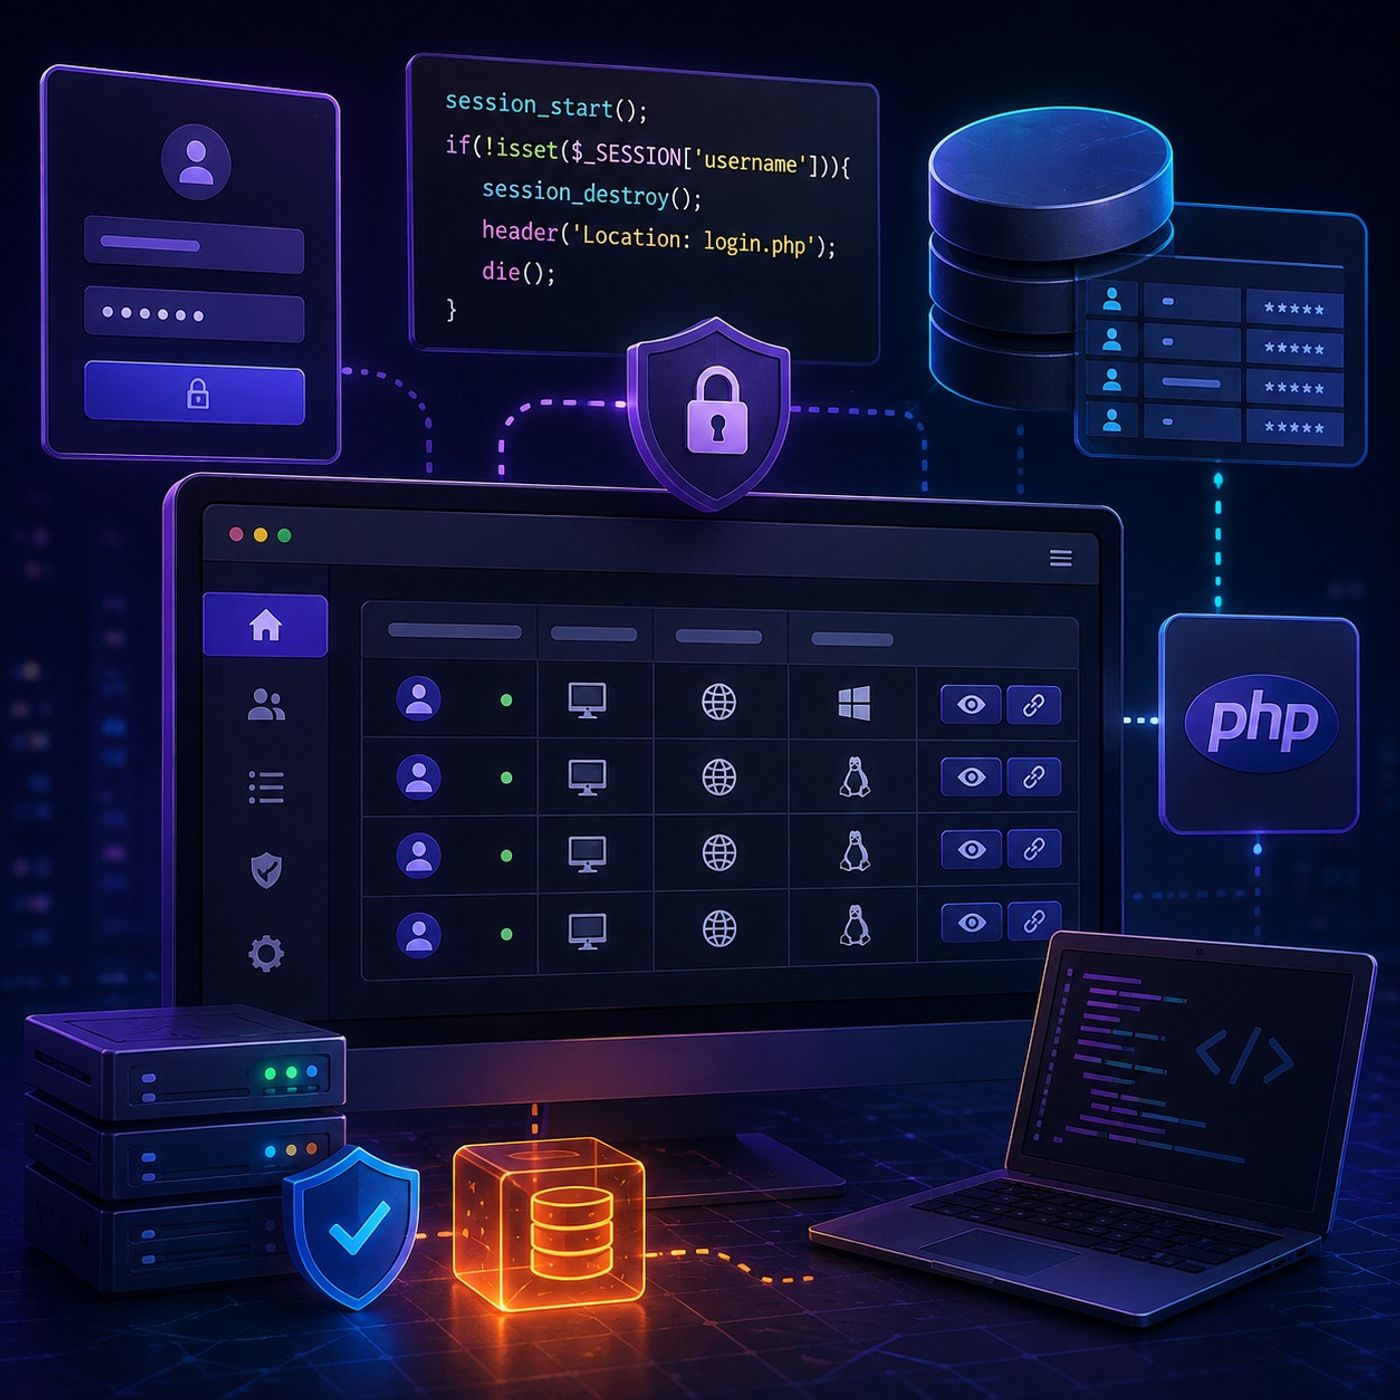
This episode, we build a PHP and MySQL control panel backend from the ground up, progressing from database initialization and server configuration to user authentication and session management.The episode focuses on connecting a web application to a MySQL database while introducing important security concepts such as prepared statements, parameter binding, password hashing, and session-based authentication.1. Creating the Database FoundationWe begin by preparing the MySQL environment and creating a dedicated database named control_panel.The database is structured around two key tables: A users table for storing web panel authentication data. A victims table containing eight columns designed to record system information such as operating systems, IP addresses, and command-and-control activity outcomes. This database provides the foundation for both authentication and the application's monitoring functionality.2. Connecting Apache, PHP, and MySQLNext, we configure the web server and database environment so that PHP can communicate reliably with MySQL.The episode covers: Adjusting Apache directory ownership and permissions. Updating MySQL authentication configuration where necessary. Creating a reusable PHP database connection script named con.php. Implementing connection error handling to identify and report database failures. This establishes a clean separation between the application's authentication logic and its database connection layer.3. Building the Login InterfaceWith the backend database ready, we create the application's login interface using an HTML form contained in login.php.The form collects user credentials and passes them to the server-side authentication logic, where the submitted values are validated against the database.4. Implementing Secure Database QueriesA major focus of the episode is preventing SQL injection during authentication.Instead of constructing SQL queries by directly concatenating user input, we use: Prepared statements Parameter binding Server-side credential validation This demonstrates why parameterized database queries are an essential security practice for applications that process user-controlled input.5. Authentication and PHP SessionsAfter retrieving the appropriate user record, the application validates the supplied credentials against the stored password representation.Once authentication succeeds, we introduce PHP session management to maintain the authenticated state and securely redirect the user to the application's main page.This creates the basic authentication flow:Login Form → Server-Side Validation → Database Lookup → Credential Verification → Session Creation → Main Panel6. Password Storage and HashingThe episode also explores password hashing and the importance of protecting stored credentials rather than keeping passwords in plaintext.The original implementation demonstrates MD5 hashing, while highlighting the broader concept of transforming credentials before storing them in the database.For modern production applications, stronger password-hashing mechanisms such as Argon2id or bcrypt should be used instead of MD5.Key TakeawaysBy the end of the episode, you will understand how to: Create and structure a MySQL database for a web application. Connect PHP to MySQL through a reusable connection layer. Configure Apache and MySQL for application integration. Build an HTML/PHP login workflow. Use prepared statements and parameter binding to reduce SQL injection risk. Implement PHP session-based authentication. Handle database and authentication errors. Understand the role of password hashing in credential protection. Recognize why legacy algorithms such as MD5 are unsuitable for modern password storage. You can listen and download our episodes for free on more than 10 different platforms: https://linktr.ee/cybercode_academy

0:00-21:04

transcript

No transcript — this publisher did not publish one.

show notes

This episode, we build a PHP and MySQL control panel backend from the ground up, progressing from database initialization and server configuration to user authentication and session management.The episode focuses on connecting a web application to a MySQL database while introducing important security concepts such as prepared statements, parameter binding, password hashing, and session-based authentication.1. Creating the Database FoundationWe begin by preparing the MySQL environment and creating a dedicated database named control_panel.The database is structured around two key tables:
  • A users table for storing web panel authentication data.
  • A victims table containing eight columns designed to record system information such as operating systems, IP addresses, and command-and-control activity outcomes.
This database provides the foundation for both authentication and the application's monitoring functionality.2. Connecting Apache, PHP, and MySQLNext, we configure the web server and database environment so that PHP can communicate reliably with MySQL.The episode covers:
  • Adjusting Apache directory ownership and permissions.
  • Updating MySQL authentication configuration where necessary.
  • Creating a reusable PHP database connection script named con.php.
  • Implementing connection error handling to identify and report database failures.
This establishes a clean separation between the application's authentication logic and its database connection layer.3. Building the Login InterfaceWith the backend database ready, we create the application's login interface using an HTML form contained in login.php.The form collects user credentials and passes them to the server-side authentication logic, where the submitted values are validated against the database.4. Implementing Secure Database QueriesA major focus of the episode is preventing SQL injection during authentication.Instead of constructing SQL queries by directly concatenating user input, we use:
  • Prepared statements
  • Parameter binding
  • Server-side credential validation
This demonstrates why parameterized database queries are an essential security practice for applications that process user-controlled input.5. Authentication and PHP SessionsAfter retrieving the appropriate user record, the application validates the supplied credentials against the stored password representation.Once authentication succeeds, we introduce PHP session management to maintain the authenticated state and securely redirect the user to the application's main page.This creates the basic authentication flow:Login Form → Server-Side Validation → Database Lookup → Credential Verification → Session Creation → Main Panel6. Password Storage and HashingThe episode also explores password hashing and the importance of protecting stored credentials rather than keeping passwords in plaintext.The original implementation demonstrates MD5 hashing, while highlighting the broader concept of transforming credentials before storing them in the database.For modern production applications, stronger password-hashing mechanisms such as Argon2id or bcrypt should be used instead of MD5.Key TakeawaysBy the end of the episode, you will understand how to:
  • Create and structure a MySQL database for a web application.
  • Connect PHP to MySQL through a reusable connection layer.
  • Configure Apache and MySQL for application integration.
  • Build an HTML/PHP login workflow.
  • Use prepared statements and parameter binding to reduce SQL injection risk.
  • Implement PHP session-based authentication.
  • Handle database and authentication errors.
  • Understand the role of password hashing in credential protection.
  • Recognize why legacy algorithms such as MD5 are unsuitable for modern password storage.


You can listen and download our episodes for free on more than 10 different platforms:
https://linktr.ee/cybercode_academy
links1