Skip to content
Artwork for Data Science Tech Brief By HackerNoon
Data Science Tech Brief By HackerNoon · Yesterday · 4 min

One Rogue pip install Away from a Breach

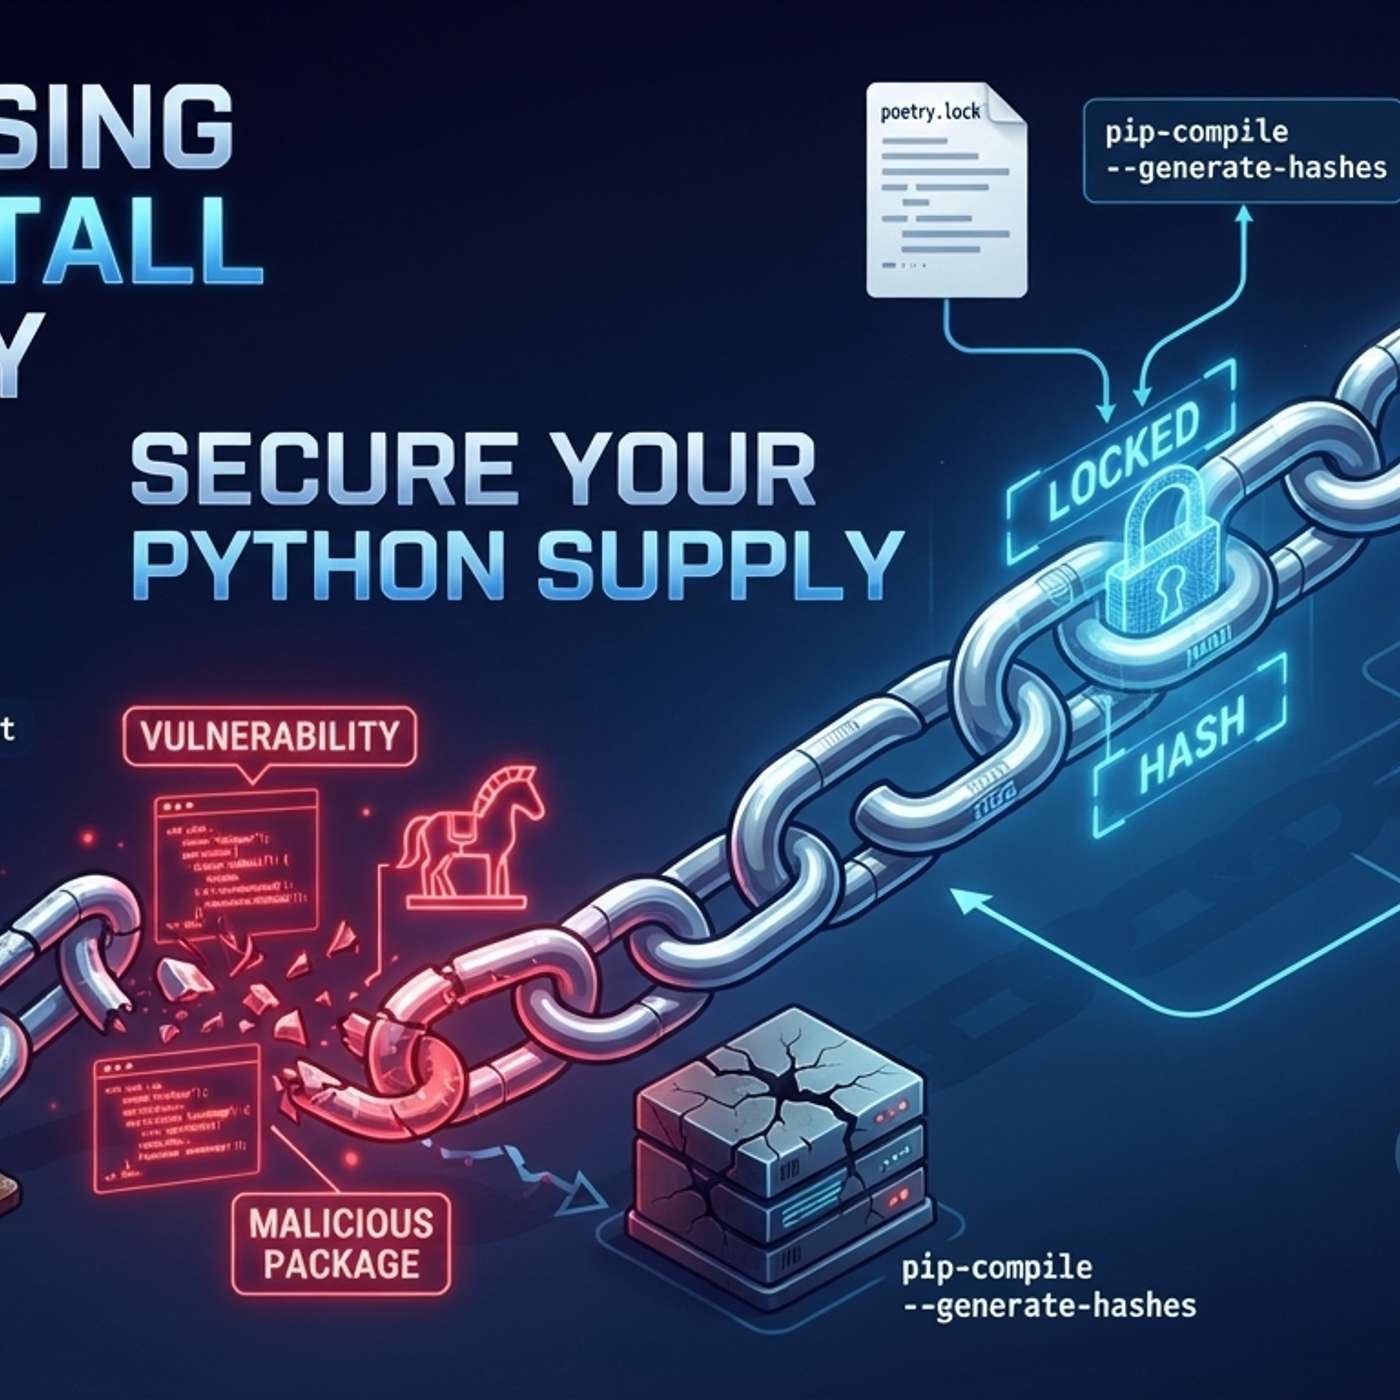
This story was originally published on HackerNoon at: https://hackernoon.com/one-rogue-pip-install-away-from-a-breach. Stop Using pip Install Blindly: Securing Your Python Supply Chain in 2026 Check more stories related to data-science at: https://hackernoon.com/c/data-science. You can also check exclusive content about #python-programming, #secure-software-development, #secure-infrastructure, #supply-chain, #software-engineering, #software-development, #backend-development, #pip-install, and more. This story was written by: @himashitech6978. Learn more about this writer by checking @himashitech6978's about page, and for more stories, please visit hackernoon.com. To secure your Python application, use deterministic builds with tools like Poetry or pip-tools to lock exact versions and cryptographic hashes. Automate vulnerability scans in your CI/CD pipeline with tools like pip-audit or Safety to catch CVEs before deployment.

0:00-4:43

transcript

No transcript — this publisher did not publish one.

show notes

This story was originally published on HackerNoon at: https://hackernoon.com/one-rogue-pip-install-away-from-a-breach.
Stop Using pip Install Blindly: Securing Your Python Supply Chain in 2026
Check more stories related to data-science at: https://hackernoon.com/c/data-science. You can also check exclusive content about #python-programming, #secure-software-development, #secure-infrastructure, #supply-chain, #software-engineering, #software-development, #backend-development, #pip-install, and more.

This story was written by: @himashitech6978. Learn more about this writer by checking @himashitech6978's about page, and for more stories, please visit hackernoon.com.

To secure your Python application, use deterministic builds with tools like Poetry or pip-tools to lock exact versions and cryptographic hashes. Automate vulnerability scans in your CI/CD pipeline with tools like pip-audit or Safety to catch CVEs before deployment.
links13