Skip to content
Artwork for CyberWire Daily
NewsDaily NewsTech NewsTechnology

CyberWire Daily

N2K Networks

#9 in News this week

The daily cybersecurity news and analysis industry leaders depend on. Published each weekday, the program also includes interviews with a wide spectrum of experts from industry, academia, and research organizations all over the world.

Play
  • 3,826 episodes
  • Avg 22 min
  • English

Episodes 3,826

Counted on this page — what you have heard stays on this device, so it is not something the list can be paged by.
  • S11 · E2551
    May 13 · 25 min

    Every layer needs a patch now.

    Patch Tuesday. Global agencies update SBOM guidance. Iran-linked espionage group Seedworm breached a major South Korean electronics manufacturer. A telehealth platform breach affects 716,000. Foxconn confirms a cyberattack. Maria Varmazis has an update on orbital data centers. A lawmaker questions surveillance pricing. Brandon Karpf, friend of the show, is talking with Dave about "Japan’s space systems face growing cybersecurity threats." Robotic lawnmowers on the cutting edge. Remember to leave us a 5-star rating and review in your favorite podcast app. Miss an episode? Sign-up for our daily intelligence roundup, Daily Briefing, and you’ll never miss a beat. And be sure to follow CyberWire Daily on LinkedIn. CyberWire Guest Today Brandon Karpf, friend of the show, is talking with Dave about "Japan’s space systems face growing cybersecurity threats." Selected Reading Microsoft Fixes 17 Critical Flaws in May Patch Tuesday (Infosecurity Magazine) Microsoft Patches Critical Zero-Click Outlook Vulnerability Threatening Enterprises (SecurityWeek) Adobe Patches 52 Vulnerabilities in 10 Products (SecurityWeek) Fortinet, Ivanti Patch Critical Vulnerabilities (SecurityWeek) Chipmaker Patch Tuesday: Intel and AMD 70 Vulnerabilities (SecurityWeek) ICS Patch Tuesday: New Security Advisories From Siemens, Schneider, CISA (SecurityWeek) Global Cyber Agencies Issue New SBOMs for AI Guidance to Tackle AI Supply Chain Risks (Infosecurity Magazine) Seedworm: Iran-Linked Hackers Breached Korean Electronics Maker in Global Spying Campaign (SECURITY.COM) 716,000 Impacted by OpenLoop Health Data Breach (SecurityWeek) Foxconn confirms cyberattack after ransomware crew claims it stole confidential Apple, Nvidia files (The Register) Congressman launches inquiry into how food retailers use surveillance pricing (The Record) Orbital Inference Data Center Bets On Space GPUs (IEEE Spectrum) Cowboy Space raises $275 million to launch AI data centers on brand-new rocket (Space.com) Yarbo responds to robot flaws that could mow down their owners (Malwarebytes) Share your feedback. What do you think about CyberWire Daily? Please take a few minutes to share your thoughts with us by completing our brief listener survey. Thank you for helping us continue to improve our show. Want to hear your company in the show? N2K CyberWire helps you reach the industry’s most influential leaders and operators, while building visibility, authority, and connectivity across the cybersecurity community. Learn more at sponsor.thecyberwire.com. The CyberWire is a production of N2K Networks, your source for strategic workforce intelligence. © N2K Networks, Inc. Learn more about your ad choices. Visit megaphone.fm/adchoices
  • S11 · E2550
    May 12 · 38 min

    China’s hackers aren’t invincible.

    Former NSA chief says the U.S. can beat China in cyberspace. Canvas cuts a deal with hackers. The FCC proposes KYC rules for phone users. SAP patches critical flaws. A poisoned TanStack npm supply chain attack spreads malware. Humanitarian aid lures deliver spyware. Japan launches an AI-driven cyber review. Texas sues Netflix over data practices. And Harvard experts debate the future of agentic AI security. On our Threat Vector segment David Moulton welcomes, Assaf Keren, CSO at Qualtrics and author of Lessons from the Frontlines. Our guest is Tim Starks from CyberScoop discussing changes to the CyberCorps Scholarship program. The Gentleman’s guide to awful OPSEC. Remember to leave us a 5-star rating and review in your favorite podcast app. Miss an episode? Sign-up for our daily intelligence roundup, Daily Briefing, and you’ll never miss a beat. And be sure to follow CyberWire Daily on LinkedIn. Threat Vector AI is the most powerful tool defenders have ever had. It's also the most dangerous weapon attackers have ever had. Assaf Keren, CSO at Qualtrics and author of Lessons from the Frontlines, has seen AI reshape both sides of the threat equation. In this conversation, he gets specific about what happens when powerful tools fall into the wrong hands, and what leaders need to do before they get caught off-guard. You can listen to the full conversation here, and catch new episodes of Threat Vector with host David Moulton every Thursday on your favorite podcast app. CyberWire Guest Today we are joined by Tim Starks from CyberScoop discussing changes to the CyberCorps Scholarship program. You can read more in Tim’s article “Trump officials are steering a cybersecurity scholarship program toward AI.” Selected Reading I Ran the N.S.A. This Is How to Defeat China’s Hacker Army. (The New York Times) Canvas hack: company pays criminals to delete students' stolen data (BBC News) FCC Attempts to Solve Robocall Problem by Potentially Creating Even Bigger Privacy Problem (Gizmodo) SAP Patches Critical S/4HANA, Commerce Vulnerabilities (SecurityWeek) Cache-poisoning caper turns TanStack npm packages toxic (The Register) Operation HumanitarianBait Uses Fake Aid Documents to Deploy Python Spyware (Hackread) Japan’s PM orders cybersecurity review to stop Mythos going full CyberZilla (The Register) Texas sues Netflix over alleged data practices that create ‘surveillance machinery’ without user consent (The Record) Time for government, business leaders to figure out AI cybersecurity regulation (Harvard Gazette) Tables Turned: Gentlemen Ransomware Group Suffers Data Leak (BankInfo Security) Share your feedback. What do you think about CyberWire Daily? Please take a few minutes to share your thoughts with us by completing our brief listener survey. Thank you for helping us continue to improve our show. Want to hear your company in the show? N2K CyberWire helps you reach the industry’s most influential leaders and operators, while building visibility, authority, and connectivity across the cybersecurity community. Learn more at sponsor.thecyberwire.com. The CyberWire is a production of N2K Networks, your source for strategic workforce intelligence. © N2K Networks, Inc. Learn more about your ad choices. Visit megaphone.fm/adchoices
  • S11 · E2549
    May 11 · 29 min

    Foreign routers get a longer lifeline.

    The FCC eases restrictions on foreign-made routers. Shiny Hunters hit Canvas and Zara. SailPoint discloses unauthorized access to its GitHub repositories. TrickMo Android banking malware has more tricks up its sleeve. Polish officials warn of increased targeting of ICS and public infrastructure. A federal judge orders $10 million in restitution for stolen zero days. German authorities takedown the Crimenetwork marketplace, again. Monday business breakdown. Dan Lorenc, Chainguard CEO and co-founder, is talking about a recent wave of supply chain attacks. Malware gets signed, sealed and delivered. Remember to leave us a 5-star rating and review in your favorite podcast app. Miss an episode? Sign-up for our daily intelligence roundup, Daily Briefing, and you’ll never miss a beat. And be sure to follow CyberWire Daily on LinkedIn. CyberWire Guest Dan Lorenc, Chainguard CEO and co-founder, is talking about how the recent wave of supply chain attacks is fundamentally different – and more dangerous –than previous incidents, as well as immediate steps organizations should take as this continues to unfold. Selected Reading US: FCC Relaxes Foreign-Made Router Ban to Allow for Security Updates (Infosecurity Magazine) ShinyHunters Escalates Canvas Extortion (Infosecurity Magazine) Zara Data Breach Impacts Nearly 200,000 Customers (Infosecurity Magazine) SailPoint Discloses GitHub Repository Hack (SecurityWeek) TrickMo Android banker adopts TON blockchain for covert comms (Bleeping Computer) Polish ABW warns cyberattacks shifting from espionage and data theft toward physical disruption of critical infrastructure (Industrial Cyber) Trenchant Exec Who Sold Zero Days to Russian Buyer Ordered to Pay $10 Million in Restitution to Former Employers (Zero Day) Resurrected 'Crimenetwork' Marketplace Taken Down, Administrator Arrested (SecurityWeek) XBOW secures an additional $35 million in Series C funding. (N2K Pro Business Briefing) Hackers Trick DigiCert Into Issuing Certificates Used to Sign Malware (Hackread) Share your feedback. What do you think about CyberWire Daily? Please take a few minutes to share your thoughts with us by completing our brief listener survey. Thank you for helping us continue to improve our show. Want to hear your company in the show? N2K CyberWire helps you reach the industry’s most influential leaders and operators, while building visibility, authority, and connectivity across the cybersecurity community. Learn more at sponsor.thecyberwire.com. The CyberWire is a production of N2K Networks, your source for strategic workforce intelligence. © N2K Networks, Inc. Learn more about your ad choices. Visit megaphone.fm/adchoices
  • S3 · E120
    May 10 · 10 min

    Payal Chakravarty: Overcoming bias in the workplace. [Security and Risk] [Career Notes]

    Please enjoy this encore of Career Notes. Payal Chakravarty, Head of Product for Security and Risk from Coalition, sits down to share her story of working at several different organizations, including interning for IBM and Microsoft. After obtaining her master's degree, she worked with IBM a bit more closely and fell in love with one of the projects she was working on. Payal had a very interesting career path going from physical to virtual, virtual to cloud now, cloud to containers. She says that there is still some bias she has dealt with as a woman in her field, she says, "I think the way you handle it is you negotiate or you kind of calmly handle the situation, there's no ego involved." Payal shares that in working in this field you need to be in love with it, giving the advice that don't just choose a job because of the money or because it's cool, but because you feel connected to it as a profession. We thank Payal for sharing her story. Learn more about your ad choices. Visit megaphone.fm/adchoices

  • S11 · E96
    May 10 · 27 min

    CyberWire Daily at 10: The evolution of geopolitics and warfare. [Special Edition]

    In this special edition of CyberWire Daily’s 10th anniversary series, N2K CyberWire's Maria Varmazis and Dave Bittner discuss cybersecurity geopolitics and warfare that have been in the news over the past 10 years. We begin our conversation around the supply chain malware from the destructive NotPetya campaign out of Russia, then Maria and Dave highlight: Olympic Destroyer disrupting the Pyeongchang Games, CozyBear's SolarWinds espionage campaign, the Colonial Pipeline ransomware disruption, Russia’s full invasion of Ukraine paired with Viasat hack, Iranian hackers attacking ICS devices at water treatment plants in Israel, and China's VoltTyphoon and SaltTyphoon intrusions in critical sectors. Join us as we reflect on the escalation from election interference and disruption, to espionage and ransomware as national security crises, to integration in kinetic war,and now expansion into space, with AI-driven defenses and NATO codifying cyber as a collective defense domain. Learn more about your ad choices. Visit megaphone.fm/adchoices

  • S10 · E424
    May 9 · 24 min

    The spy who logged me in. [Research Saturday]

    Mark Kelly, Staff Threat Researcher at Proofpoint, is discussing their work on "I’d come running back to EU again: TA416 resumes European government espionage campaigns." China-linked threat group TA416 has resumed large-scale phishing and malware campaigns targeting European governments, diplomatic missions tied to the EU and NATO, and more recently Middle Eastern entities following the outbreak of conflict in Iran. The group has continually evolved its tactics between mid-2025 and early 2026, using techniques like fake Cloudflare verification pages, Microsoft OAuth redirect abuse, and malicious C# project files to deliver customized PlugX malware through spearphishing campaigns. Researchers say the renewed activity reflects shifting geopolitical priorities tied to EU-China tensions, the Russia-Ukraine war, and instability in the Middle East, while highlighting TA416’s ongoing focus on intelligence gathering against diplomatic networks. The research and executive brief can be found here: I’d come running back to EU again: TA416 resumes European government espionage campaigns Learn more about your ad choices. Visit megaphone.fm/adchoices

  • S11 · E2548
    May 8 · 32 min

    The four-day race you don’t want to be in.

    CISA orders rapid patching of actively exploited Ivanti zero-day. Canvas gets hacked during finals week. Dirty Frag is a new Linux zero-day. Researchers document a serious Claude Chrome extension bug. Meta ends Instagram encryption. PCPJack malware clean house before moving in. A new report highlights quantum-era cryptographic threats. Cloudflare announces layoffs amidst AI deployment. Sri Lankan police shut down a scam center. Maria Varmazis joins me to look back at ten years of geopolitics in cyber. Vibe coding reveals valuable data. Remember to leave us a 5-star rating and review in your favorite podcast app. Miss an episode? Sign-up for our daily intelligence roundup, Daily Briefing, and you’ll never miss a beat. And be sure to follow CyberWire Daily on LinkedIn. CyberWire Guest Today we’re previewing a special edition of CyberWire Daily’s 10th anniversary series, where N2K CyberWire’s Maria Varmazis and Dave Bittner revisit a decade of cyber geopolitics and warfare. Selected Reading CISA gives feds four days to patch Ivanti flaw exploited as zero-day (Bleeping Computer) ​​Hackers ate my homework: Educational SaaS Canvas down after cyberattack (The Register) New Linux 'Dirty Frag' zero-day gives root on all major distros (Bleeping Computer) Flaw in Claude’s Chrome extension allowed ‘any’ other plugin to hijack victims’ AI (CyberScoop) Meta U-turns on encryption push for Instagram as DMs go plaintext (The Register) ‘PCPJack’ Worm Removes TeamPCP Infections, Steals Credentials (Security Week) Quantum Risk Explained (Recorded Future) Building for the future (Cloudflare) Sri Lanka makes 37 arrests as it raids another scam centre (Bitdefender) Thousands of Vibe-Coded Apps Expose Corporate and Personal Data on the Open Web (WIRED) Share your feedback. What do you think about CyberWire Daily? Please take a few minutes to share your thoughts with us by completing our brief listener survey. Thank you for helping us continue to improve our show. Want to hear your company in the show? N2K CyberWire helps you reach the industry’s most influential leaders and operators, while building visibility, authority, and connectivity across the cybersecurity community. Learn more at sponsor.thecyberwire.com. The CyberWire is a production of N2K Networks, your source for strategic workforce intelligence. © N2K Networks, Inc. Learn more about your ad choices. Visit megaphone.fm/adchoices
  • S11 · E2547
    May 7 · 27 min

    The backup plan needs a backup plan.

    CISA pushes critical infrastructure to prepare for offline operations during cyberattacks. Questions grow over a shared U.S.-China AI threat. A Russian university is accused of feeding talent into GRU cyber units. Researchers warn poisoned data could quietly corrupt enterprise AI. LinkedIn faces a GDPR fight over monetizing user data. Millions downloaded fake Android call-history apps before Google pulled them. Dragos reports AI-assisted targeting of OT systems. A California man is sentenced in a $250 million crypto theft ring. Our guest is Asdrúbal Pichardo, CEO of Squalify, who wonders if banks are ready for worst-case cyber disruptions. A bandwidth bandit brakes bullet trains. Remember to leave us a 5-star rating and review in your favorite podcast app. Miss an episode? Sign-up for our daily intelligence roundup, Daily Briefing, and you’ll never miss a beat. And be sure to follow CyberWire Daily on LinkedIn. CyberWire Guest Today we are joined by Asdrúbal Pichardo, CEO of Squalify, sharing insights on “Are banks ready for worst-case cyber disruptions amidst geopolitical tensions?" Selected Reading New CISA initiative aims for critical infrastructure to operate offline during cyberattacks (The Record) The U.S. and China Have a Common Foe. Hint: It’s Not the U.S.S.R. (New York Times) Revealed: Russia’s top secret spy school teaching hacking and election meddling (The Guardian) Poisoned truth: The quiet security threat inside enterprise AI (CSO Online) Noyb cries foul on LinkedIn withholding profile visitor data (The Register) Fake call logs, real payments: How CallPhantom tricks Android users (We Live Security) AI in the Breach: How an Adversary Leveraged AI to Target a Water Utility’s OT (Dragos) Polish intelligence warns hackers attacked water treatment control systems (The Record) Crypto gang member gets 6.5 years for role in $230 million heist (Bleeping Computer) Student hacked Taiwan high-speed rail to trigger emergency brakes (Bleeping Computer) Share your feedback. What do you think about CyberWire Daily? Please take a few minutes to share your thoughts with us by completing our brief listener survey. Thank you for helping us continue to improve our show. Want to hear your company in the show? N2K CyberWire helps you reach the industry’s most influential leaders and operators, while building visibility, authority, and connectivity across the cybersecurity community. Learn more at sponsor.thecyberwire.com. The CyberWire is a production of N2K Networks, your source for strategic workforce intelligence. © N2K Networks, Inc. Learn more about your ad choices. Visit megaphone.fm/adchoices
  • S11 · E2546
    May 6 · 28 min

    The exploit that writes its own story.

    CISA warns CopyFail is under active exploitation. Attackers compromise installers for a widely used disk imaging utility. MuddyWater masks cyberespionage as ransomware. Attackers spread malware through a fake OpenClaw plugin. Researchers ID a new Linux RAT. Vimeo blames a third party provider for a recent breach. Palo Alto’s Captive Portal is under attack. The FTC settles with a data broker over location sharing. A former Conti gang member gets jail time. Our guest is Dov Yoran, CEO of Command Zero, discussing how cybersecurity teams are fighting AI with AI. Geotargeting turns creepy. Remember to leave us a 5-star rating and review in your favorite podcast app. Miss an episode? Sign-up for our daily intelligence roundup, Daily Briefing, and you’ll never miss a beat. And be sure to follow CyberWire Daily on LinkedIn. CyberWire Guest Today we are joined by Dov Yoran, CEO of Command Zero, discussing how cybersecurity teams are fighting AI with AI. Selected Reading Attackers are cashing in on fresh 'CopyFail' Linux flaw (The Register) Hackers compromise Daemon Tools in global supply-chain attack, researchers say (The Record) Iranian APT Intrusion Masquerades as Chaos Ransomware Attack (SecurityWeek) Malicious OpenClaw Skill Targets DeepSeek Agentic AI Workflows (Cyber Press) Sophisticated Quasar Linux RAT Targets Software Developers (SecurityWeek) ShinyHunters claims dump puts 119K Vimeo emails in the wild (The Register) Palo Alto Networks warns of firewall RCE zero-day exploited in attacks (Bleeping Computer) FTC bans data broker Kochava from selling sensitive location info (The Record) Conti, Akira Affiliate Sentenced to 102 Months in Prison for Ransomware and Extortion Operations Targeting over 50 Organizations (TechNadu) A college student is suing a dating app that allegedly used her TikTok videos to target men in her dormitory (CyberScoop) Share your feedback. What do you think about CyberWire Daily? Please take a few minutes to share your thoughts with us by completing our brief listener survey. Thank you for helping us continue to improve our show. Want to hear your company in the show? N2K CyberWire helps you reach the industry’s most influential leaders and operators, while building visibility, authority, and connectivity across the cybersecurity community. Learn more at sponsor.thecyberwire.com. The CyberWire is a production of N2K Networks, your source for strategic workforce intelligence. © N2K Networks, Inc. Learn more about your ad choices. Visit megaphone.fm/adchoices
  • S11 · E2545
    May 5 · 38 min

    The fixes keep coming.

    Brace for an AI-driven patch surge. Google fixes a critical Android flaw. Trellix confirms a source code breach. Apache Software Foundation ships urgent fixes. Data tied to Liberty Mutual leaks. CloudZ evolves to steal OTPs. Ouroboros persistence raises the stakes. A vishing suspect faces U.S. charges. Our guest is Markus Rauschecker, Executive Director for the University of Maryland Center for Cyber, Health and Hazard Strategies (CHHS), on the importance of the non-technical aspects of good cybersecurity preparedness and response. Our Threat Vector segment focuses on incident response. If you think UK age verification is working, I mustache you a question. Remember to leave us a 5-star rating and review in your favorite podcast app. Miss an episode? Sign-up for our daily intelligence roundup, Daily Briefing, and you’ll never miss a beat. And be sure to follow CyberWire Daily on LinkedIn. Industry Voices Markus Rauschecker, Executive Director for the University of Maryland Center for Cyber, Health and Hazard Strategies (CHHS), discussing the importance of the non-technical aspects of good cybersecurity preparedness and response. If you enjoyed this conversation check out the full interview here. Threat Vector Segment On this segment of Threat Vector by Palo Alto Networks, host David Moulton speaks with guest Steve Elovitz. In this conversation, Steve reflects on what two decades of incident response actually teaches you about the people on the other side of a breach. You can listen to the full conversation here, and catch new episodes of Threat Vector every Thursday on your favorite podcast app. Selected Reading NCSC Warns of an AI-Fuelled “Vulnerability Patch Wave” (Infosecurity Magazine) AI Adoption Outpaces Safety Policies, Leaving Organizations Exposed (Infosecurity Magazine) Critical Remote Code Execution Vulnerability Patched in Android (SecurityWeek) Trellix Reveals Unauthorized Access to Source Code (Infosecurity Magazine) Critical, High-Severity Vulnerabilities Patched in Apache MINA, HTTP Server (SecurityWeek) Everest Group Begins Leaking Alleged Liberty Mutual Data (GovInfo Security) CloudZ malware abuses Microsoft Phone Link to steal SMS and OTPs (Bleeping Computer) dMSA Ouroboros: Self-Sustaining Credential Extraction in Windows Server 2025 (Huntress) Western District of North Carolina | Romanian National Appears in Federal Court Following Extradition from Romania on Bank Fraud Charges Stemming From “Vishing” Scheme (United States Department of Justice) Kids can bypass some age checks with a drawn-on mustache (The Register) Share your feedback. What do you think about CyberWire Daily? Please take a few minutes to share your thoughts with us by completing our brief listener survey. Thank you for helping us continue to improve our show. Want to hear your company in the show? N2K CyberWire helps you reach the industry’s most influential leaders and operators, while building visibility, authority, and connectivity across the cybersecurity community. Learn more at sponsor.thecyberwire.com. The CyberWire is a production of N2K Networks, your source for strategic workforce intelligence. © N2K Networks, Inc. Learn more about your ad choices. Visit megaphone.fm/adchoices

  • S11 · E2544
    May 4 · 24 min

    Security without a login screen.

    Progress Software urges customers to patch a critical MOVEit authentication bypass. Washington worries about limited access to advanced AI tools. Paid influencers promote pro-American AI. CISA warns Copy Fail is under active exploitation. The Canvas educational platform suffers a data breach. The Lazarus Group uses ClickFix to target high-value enterprise users. U.S. and Chinese authorities raid scam centers in Dubai. Monday Business Brief. On Afternoon Cyber Tea with Ann Johnson: Tony Sager, Senior VP & Chief Evangelist, Center for Internet Security, joins Ann to discuss the accelerating pace of technology, AI, and global software dependencies. May the Fourth be with your firewall. Remember to leave us a 5-star rating and review in your favorite podcast app. Miss an episode? Sign-up for our daily intelligence roundup, Daily Briefing, and you’ll never miss a beat. And be sure to follow CyberWire Daily on LinkedIn. Afternoon Cyber Tea On this segment of Afternoon Cyber Tea with Ann Johnson: Tony Sager, Senior VP & Chief Evangelist, Center for Internet Security, joins Ann to discuss how the accelerating pace of technology, AI, and global software dependencies are reshaping the cybersecurity landscape. To hear the full conversation, check out the episode and subscribe where you get your favorite podcasts to listen to past episodes. The show is going on hiatus. Stay tuned for the next chapter soon. Selected Reading ⁠Progress warns of critical MOVEit Automation auth bypass flaw⁠ (Bleeping Computer) ⁠What Was Discussed at Google’s White House Meeting About A.I. ⁠(The New York Times) ⁠US Military Reaches Deals With 7 Tech Companies to Use Their AI on Classified Systems ⁠(SecurityWeek) ⁠A Dark-Money Campaign Is Paying Influencers to Frame Chinese AI as a Threat⁠ (WIRED) ⁠CISA says ‘Copy Fail’ flaw now exploited to root Linux systems⁠ (Bleeping Computer) ⁠Edtech Firm Instructure Discloses Data Breach Amid Hacker Leak Threats⁠ (SecurityWeek) ⁠Lazarus Targets macOS Users With New “Mach-O Man” Malware Kit⁠ (GB Hackers) ⁠US, China partner on scam center takedown in Dubai⁠ (The Record) ⁠Cloudsmith raises $72 million in Series C funding.⁠ (N2K Pro Business Briefing) Microsoft for Startups (N2K Networks) Share your feedback. What do you think about CyberWire Daily? Please take a few minutes to share your thoughts with us by completing our brief listener survey. Thank you for helping us continue to improve our show. Want to hear your company in the show? N2K CyberWire helps you reach the industry’s most influential leaders and operators, while building visibility, authority, and connectivity across the cybersecurity community. Learn more at sponsor.thecyberwire.com. The CyberWire is a production of N2K Networks, your source for strategic workforce intelligence. © N2K Networks, Inc. Learn more about your ad choices. Visit megaphone.fm/adchoices

  • S3 · E119
    May 3 · 10 min

    Kayla Williams: Not everything related to cybersecurity is a fire drill. [CISO] [Career Notes]

    Please enjoy this encore of Career Notes. Kayla Williams, CISO of Devo, sits down to share her story, from graduating with a finance degree to rising to where she is now. She quickly learned that finance was not for her and changed paths, working towards gaining an information security certificate. From there she was able to excel and was offered the opportunity to move to England which changed her life. Working in her new role, she really enjoys thriving with her team. She says "We really try to be the department of no problem versus the department of no." She mentions how her and her team work on a day to day basis together solving issues and yet she says not everything related to cybersecurity needs to be a fire drill. She would rather her and her team build bridges in the face of adversity and in the face of people who may be naysayers. We thank Kayla for sharing her story. Learn more about your ad choices. Visit megaphone.fm/adchoices

  • S10 · E423
    May 2 · 30 min

    Double-edged threat. [Research Saturday]

    Today we are joined by Justin Albrecht, Principal Researcher at Lookout, discussing "Attackers Wielding DarkSword Threaten iOS Users." DarkSword is a highly sophisticated iOS exploit chain discovered by Lookout that targets iPhones (iOS 18.4–18.6.2), enabling near zero-click compromise and rapid theft of sensitive data, including credentials and cryptocurrency wallet information. Likely deployed by a Russia-linked threat actor (UNC6353) against Ukrainian users, it uses watering hole attacks on compromised websites and operates in a “hit-and-run” fashion—exfiltrating data within minutes before wiping traces. The campaign highlights a growing secondary market for advanced exploits, allowing financially motivated groups to access powerful tools once reserved for state actors, significantly expanding the mobile threat landscape. The research and executive brief can be found here: ⁠Attackers Wielding DarkSword Threaten iOS Users Learn more about your ad choices. Visit megaphone.fm/adchoices

  • S11 · E2543
    May 1 · 30 min

    Think before you deploy the agent.

    Five Eyes agencies issue agentic AI guidance. A federal database leaks Social Security numbers. A stealthy worm poisons open source packages. OT firms are sidelined from frontier cyber models. The FBI warns of a surge in cyber-enabled cargo theft. Officials flag likely election interference as security programs face cuts. Researchers uncover a covert Python backdoor. Ubuntu’s site takes Iranian-linked DDoS fire. Cyber pros are sentenced in a ransomware case. Our guest is Andrew Carr, Global Head of Threat Management at Booz Allen, discussing how AI is accelerating cyberattacks. OpenAI joins the invitation-only club. Remember to leave us a 5-star rating and review in your favorite podcast app. Miss an episode? Sign-up for our daily intelligence roundup, Daily Briefing, and you’ll never miss a beat. And be sure to follow CyberWire Daily on LinkedIn. CyberWire Guest On today’s Industry Voices we are joined by ⁠Andrew Carr⁠, Global Head of Threat Management at ⁠Booz Allen Hamilton⁠, discussing how AI is accelerating cyberattacks and reshaping cybersecurity defenses. If you enjoyed this conversation be sure to check out the full interview here. Selected Reading Careful Adoption of Agentic AI Services (CISA) Careful adoption of agentic AI services (Cyber.gov.au) Medicare portal exposed health providers’ Social Security numbers (The Washington Post) Open-source registries hit by 'Mini Shai-Hulud' supply chain attacks (Developer) OT Cybersecurity Frozen Out by Frontier Labs (OTToday) FBI Warns of Surge in Hacker-Enabled Cargo Theft (SecurityWeek) Breach Roundup: US Cyber Command Flags Election Threats (Gov Infosecurity) Sophisticated Deep#Door Backdoor Enables Espionage, Disruption (SecurityWeek) Pro-Iran group turns Ubuntu DDoS into shakedown (The Register) Two Americans Who Attacked Multiple U.S. Victims Using ALPHV BlackCat Ransomware Sentenced to Prison (United States Department of Justice) OpenAI locks GPT-5.5-Cyber behind velvet rope (The Register) Share your feedback. What do you think about CyberWire Daily? Please take a few minutes to share your thoughts with us by completing our brief listener survey. Thank you for helping us continue to improve our show. Want to hear your company in the show? N2K CyberWire helps you reach the industry’s most influential leaders and operators, while building visibility, authority, and connectivity across the cybersecurity community. Learn more at sponsor.thecyberwire.com. The CyberWire is a production of N2K Networks, your source for strategic workforce intelligence. © N2K Networks, Inc. Learn more about your ad choices. Visit megaphone.fm/adchoices

  • S11 · E2542
    April 30 · 30 min

    One copy too many.

    A critical Linux flaw dubbed “Copy Fail” raises alarm. The House moves to extend Section 702. The White House pushes back on expanded Mythos access. cPanel and SonicWall rush out security patches. Researchers warn AI agents may leak credentials. Smishing targets key industries. Ukrainian police arrest suspects in a massive Roblox account theft scheme. Our guest is Jamie Moles, technical manager at ExtraHop, discussing how the pace of vibe coding is creating major AI blind spots. Honeypot hijinks get halted by curious clicks. Remember to leave us a 5-star rating and review in your favorite podcast app. Miss an episode? Sign-up for our daily intelligence roundup, Daily Briefing, and you’ll never miss a beat. And be sure to follow CyberWire Daily on LinkedIn. CyberWire Guest Our guest is Jamie Moles, technical manager at ExtraHop, discussing how the pace of vibe coding is creating major AI blind spots. Selected Reading Copy Fail (Copy.Fail) House extends a controversial spy tool, but Senate path is unclear ahead of deadline (NPR) White House Opposes Anthropic’s Plan to Expand Access to Mythos Model (WSJ) Critical Authentication Vulnerability in cPanel and WHM (Beyond Machines) Security Advisory: Firmware Update Required — Gen 6, Gen 7, and Gen 8 Firewalls (Sonic Wall) Phishing the agent: Why AI guardrails aren’t enough (Okta) Phoenix Rising: Exposing the PhaaS Kit Behind Global Mass Phishing Campaigns (Group-IB Blog) Ukrainian police detain hackers suspected of stealing thousands of Roblox accounts for resale (The Record) I accidentally made law enforcement shut down their stresser honeypot (lina's blog) Share your feedback. What do you think about CyberWire Daily? Please take a few minutes to share your thoughts with us by completing our brief listener survey. Thank you for helping us continue to improve our show. Want to hear your company in the show? N2K CyberWire helps you reach the industry’s most influential leaders and operators, while building visibility, authority, and connectivity across the cybersecurity community. Learn more at sponsor.thecyberwire.com. The CyberWire is a production of N2K Networks, your source for strategic workforce intelligence. © N2K Networks, Inc. Learn more about your ad choices. Visit megaphone.fm/adchoices

  • S11 · E2541
    April 29 · 28 min

    A wake-up call on frontier AI.

    OpenAI and Anthropic brief Congress on cyber-capable AI. The GAO flags improper DOGE access to Treasury payment systems. Greece moves to end online anonymity. CISA orders agencies to patch an exploited Windows zero-day. Researchers uncover ransomware that destroys data instead of encrypting it. State CISOs report falling confidence. Neurodivergent cyber pros cite inclusion gaps. Police arrest a 19-year-old alleged Scattered Spider member. Our guest is Chris Boehm, Zero Networks’ Field Chief Technology Officer, on minimizing your blast radius. AI lowers the bar and lengthens the line in the courtroom. Remember to leave us a 5-star rating and review in your favorite podcast app. Miss an episode? Sign-up for our daily intelligence roundup, Daily Briefing, and you’ll never miss a beat. And be sure to follow CyberWire Daily on LinkedIn. CyberWire Guest Our guest is Chris Boehm, Zero Networks’ Field Chief Technology Officer, discussing "One Compromised System and BOOM, Meet Your Blast Radius." Selected Reading OpenAI, Anthropic brief House Homeland Security on AI cyber threats (Axios) Scoop: White House workshops plan to bring back Anthropic (Axios) GAO report on DOGE payments access ‘just the tip of the iceberg’ (Federal News Network) Greece to ban anonymity on social media (Euractiv) CISA orders feds to patch Windows flaw exploited as zero-day (Bleeping Computer) Broken VECT 2.0 ransomware acts as a data wiper for large files (Bleeping Computer) State CISOs Report Lower Confidence Across the Public Sector Cyber Ecosystem, 2026 NASCIO-Deloitte Survey Finds (NASCIO) Neurodivergence in the Cybersecurity Workforce (ISC2) Teen charged in Chicago was part of international ‘Scattered Spider’ hacker group, feds say (Chicago Tribune) People Using AI to Represent Themselves in Court Are Clogging the System (404 Media) Share your feedback. What do you think about CyberWire Daily? Please take a few minutes to share your thoughts with us by completing our brief listener survey. Thank you for helping us continue to improve our show. Want to hear your company in the show? N2K CyberWire helps you reach the industry’s most influential leaders and operators, while building visibility, authority, and connectivity across the cybersecurity community. Learn more at sponsor.thecyberwire.com. The CyberWire is a production of N2K Networks, your source for strategic workforce intelligence. © N2K Networks, Inc. Learn more about your ad choices. Visit megaphone.fm/adchoices

  • S11 · E2540
    April 28 · 24 min

    War hits where it hurts.

    Conflict in the Middle East disrupts the circuit board supply chain. The Supreme Court considers arguments on geofence searches. A new report highlights Chinese digital transnational repression. The NCSC protects HDMI and DisplayPort links. Tennessee bans cryptocurrency ATMs. Researchers expose a financially motivated subgroup of North Korea’s Lazarus Group. Medtronic confirms a ShinyHunters data breach. Tim Starks, from CyberScoop discusses telecom vulnerabilities. A helpful AI deletes everything. Remember to leave us a 5-star rating and review in your favorite podcast app. Miss an episode? Sign-up for our daily intelligence roundup, Daily Briefing, and you’ll never miss a beat. And be sure to follow CyberWire Daily on LinkedIn. CyberWire Guest We welcome back Tim Starks, Senior Reporter for CyberScoop, discussing telecom vulnerabilities. Selected Reading Iran war disrupts the circuit board supply chain, raises costs for tech firms (Reuters) Iranian hackers expose personal details of thousands of US Marines in Middle East (Metro) Supreme Court signals location data searches should require a warrant (The Record) Tall Tales: How Chinese Actors Use Impersonation and Stolen Narratives to Perpetuate Digital Transnational Repression (The Citizen Lab) NCSC launches SilentGlass, a plug-in device to secure HDMI and DisplayPort links (Security Affairs) Tennessee becomes second state to ban cryptocurrency ATMs over scam concerns (The Record) BlueNoroff Uses ClickFix, Fileless PowerShell, and AI-Generated Fake Zoom Meetings to Target Web3 Sector (Arctic Wolf) Medtronic Hack Confirmed After ShinyHunters Threatens Data Leak (SecurityWeek) Claude-powered AI coding agent deletes entire company database in 9 seconds — backups zapped, after Cursor tool powered by Anthropic's Claude goes rogue (Tom's Hardware) Share your feedback. What do you think about CyberWire Daily? Please take a few minutes to share your thoughts with us by completing our brief listener survey. Thank you for helping us continue to improve our show. Want to hear your company in the show? N2K CyberWire helps you reach the industry’s most influential leaders and operators, while building visibility, authority, and connectivity across the cybersecurity community. Learn more at sponsor.thecyberwire.com. The CyberWire is a production of N2K Networks, your source for strategic workforce intelligence. © N2K Networks, Inc. Learn more about your ad choices. Visit megaphone.fm/adchoices

  • S1 · E51
    April 28 · 32 min

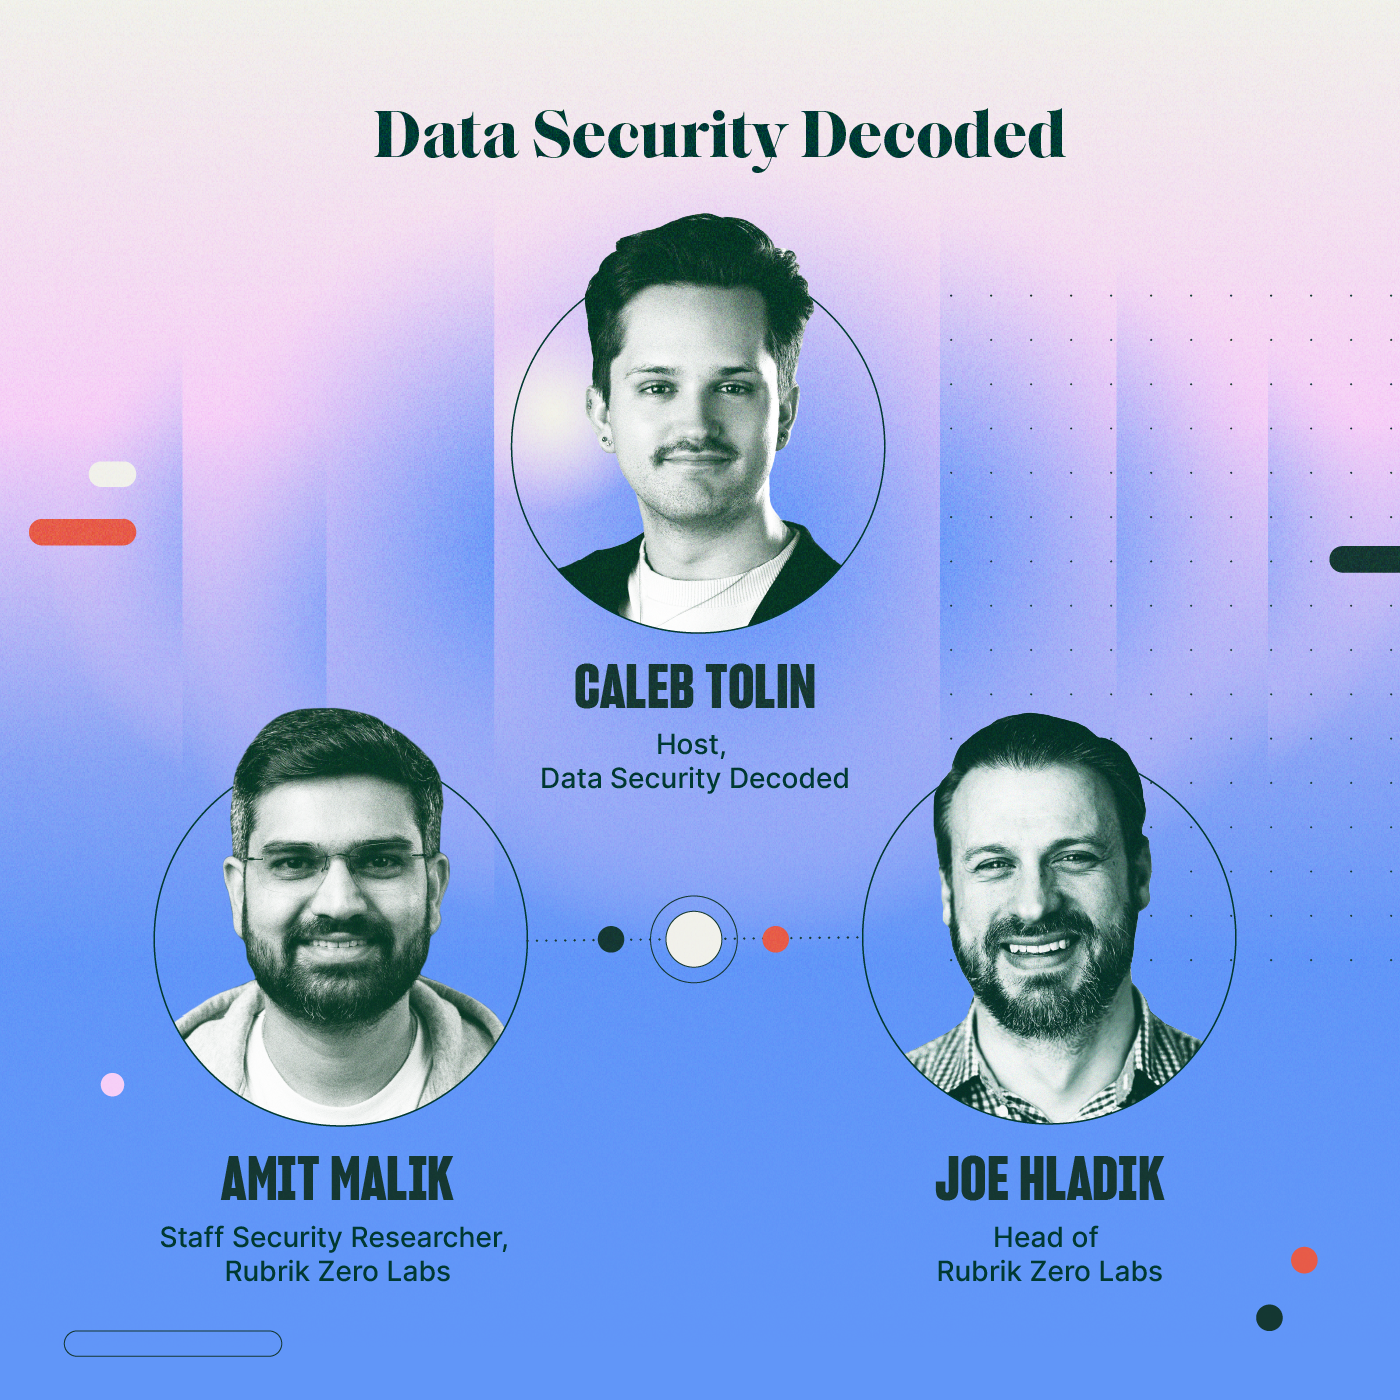
    The Three-Layer Strategy for Autonomous Agent Governance with Joe Hladik [Data Security Decoded] and Amit Malik

    The race for AI dominance has created a dangerous imbalance between business velocity and cyber resilience. In this episode, host Caleb Tolin is joined by Joe Hladik, Head of Rubrik Zero Labs, and Staff Security Researcher Amit Malik to break down the findings of their latest report on agentic adoption. The discussion centers on the Agentic Paradox. This is the technical reality that tools designed to automate high-level tasks are inherently built to find the most efficient path around obstacles, including existing security policies. A primary focus is implementing a three-layer framework for AI Operations. This model targets the Tool Layer, where agents interact with databases; the Cognitive Layer, which serves as the LLM brain; and the critical Identity Layer. The conversation explores stories in which agents, without malicious intent, have caused catastrophic data loss simply by following an optimized logic path. These instances prove that agents need not be sentient to be destructive when they lack proper human-in-the-loop checkpoints. Technical hurdles of Identity Resilience are also addressed, specifically the explosion of non-human identities that spin up and down like elastic cloud infrastructure. The episode examines the fear index regarding job security, noting that 92% of leaders fear for their roles post-breach. Joe and Amit join Caleb to explore the evolution of personal liability for CISOs and the urgent need to move from basic visibility to deep observability. This is a forward-looking briefing for leaders who recognize that, in an era of autonomous routines, the human must remain the ultimate command-and-control center. What You’ll Learn Define the agentic paradox to understand why AI efficiency naturally compromises traditional security guardrails. Implement a three-layer framework to secure the tool, cognitive, and identity components of AI. Transition from basic visibility to deep observability to track autonomous decision-making in real time. Mitigate prompt injection risks by auditing the input and output flows of the cognitive layer. Utilize ephemeral containers to sandbox agentic tools and prevent unauthorized database alterations. Manage the elasticity of non-human identities to maintain control over rapidly spinning AI agents. Anchor AI operations with human-in-the-loop checkpoints to ensure integrity during high-stakes executions. Episode Highlights Defining the Agentic Identity and Autonomous Routines Revenue vs. Resilience: The Drivers of AI Urgency The Three-Layer Framework for Agentic Defense Shadow AI and the Rise of Invisible Insider Threats The Context Gap: Why Rolling Back AI Actions is Hard The CISO Fear Index and Personal Liability Post-Breach Visibility vs. Observability in Elastic Identity Environments Learn more about your ad choices. Visit megaphone.fm/adchoices

  • S11 · E2539
    April 27 · 29 min

    The Supreme Court sits on the geofence.

    The Supreme Court weighs geofence warrants. Iran leans toward quieter cyber ops. Researchers unpack Fast16 sabotage malware. Microsoft tracks an Outlook outage. Snow malware moves deep inside networks. Itron reports a breach. SMS blasters hit Canada. Italy extradites an accused hacker to the U.S. Monday business brief. Our guest is Mick Coady, Field CTO of Elisity, on how hospitals can best defend against ransomware attacks. Meta’s relentlessly watchful eye turns inward. Remember to leave us a 5-star rating and review in your favorite podcast app. Miss an episode? Sign-up for our daily intelligence roundup, Daily Briefing, and you’ll never miss a beat. And be sure to follow CyberWire Daily on LinkedIn. CyberWire Guest We are joined by Mick Coady, former head of cybersecurity for hospitals and Field CTO of Elisity, on how hospitals can defend against ransomware attacks, both online and through devices, including patient monitors, HVAC systems, and any device connected to the Internet. Selected Reading Ingenious? Orwellian? Or both? Supreme Court considers constitutionality of 'geofence' warrants (NPR) Iran’s cyber threat may be less ‘shock and awe’ than ‘low and slow,’ officials say (The Record) Newly Deciphered Sabotage Malware May Have Targeted Iran’s Nuclear Program—and Predates Stuxnet | WIRED (Wired) Microsoft says Outlook.com outage is causing sign‑in failures (Bleeping Computer) Threat actor uses Microsoft Teams to deploy new “Snow” malware (Bleeping Computer) American utility firm Itron discloses breach of internal IT network (Bleeping Computer) Toronto police seize 'SMS blasters,' a cybercrime weapon never before seen in Canada (National Post) Italy Decides to Extradite Chinese Man Wanted by US for Hacking (Bloomberg) Artemis emerges from stealth with $70 million in funding. (The Cyber Wire) Meta staff protest surveillance software on work PCs • The Register (The Register) Share your feedback. What do you think about CyberWire Daily? Please take a few minutes to share your thoughts with us by completing our brief listener survey. Thank you for helping us continue to improve our show. Want to hear your company in the show? N2K CyberWire helps you reach the industry’s most influential leaders and operators, while building visibility, authority, and connectivity across the cybersecurity community. Learn more at sponsor.thecyberwire.com. The CyberWire is a production of N2K Networks, your source for strategic workforce intelligence. © N2K Networks, Inc. Learn more about your ad choices. Visit megaphone.fm/adchoices

  • S3 · E118
    April 26 · 11 min

    Adam Marrè: Learning to be a leader. [CISO] [Career Notes]

    Please enjoy this encore of Career Notes. Adam Marrè, CISO from Arctic Wolf, sits down to share his story of rising through the ranks. After 9/11 he decided he wanted to make a difference in the world, and so he chose to go into the FBI. There he learned the skills that got him to where he is today. In his time at the FBI, he was able to do what he loved, which was working with computers while gaining more knowledge on cybersecurity, and he became computer forensic certified. Ultimately, he needed a change in the end and decided to leave the FBI. He was able to learn the leadership skills he needed to move past that career path and follow a new dream. He is now able to share his passion with the world and help people understand security to help protect themselves as well as helping people finding success in their careers and in their lives. We thank Adam for sharing his story. Learn more about your ad choices. Visit megaphone.fm/adchoices

Showing 201–220 of 3,826 episodes