Stop Trusting the OAuth Email: How One Missing Check Enables Account Takeover in 2026
transcript
show notes
This story was originally published on HackerNoon at: https://hackernoon.com/stop-trusting-the-oauth-email-how-one-missing-check-enables-account-takeover-in-2026.
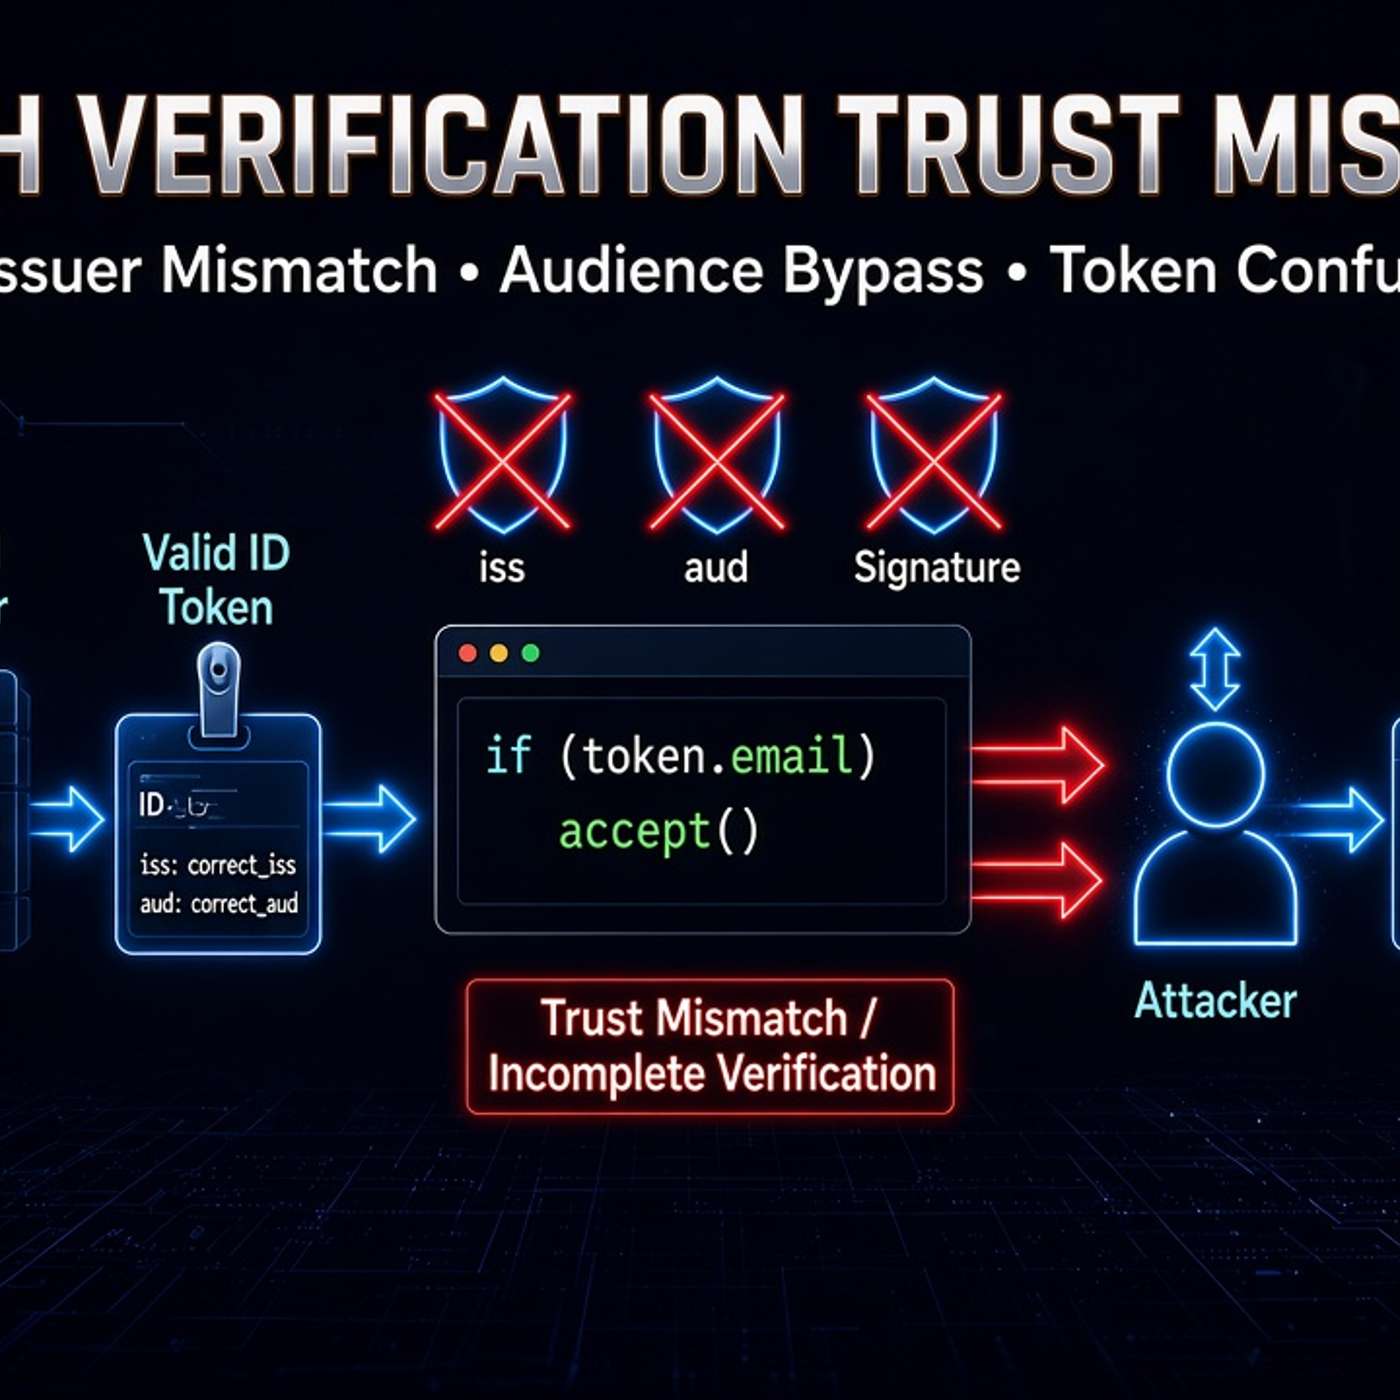
Explore OAuth Verification Trust Mismatch, a security issue caused by mismatch between OAuth providers and client applications
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #cybersecurity, #oauth-authentication, #web-security, #oauth-vulnerabilities, #hackernoon-top-story, #account-takeover, #vulnerabilities, and more.
This story was written by: @viodex. Learn more about this writer by checking @viodex's about page,
and for more stories, please visit hackernoon.com.
OAuth Verification Trust Mismatch vulnerabilities can arise when a client application incorrectly assumes an email address is verified based on an OAuth provider's authentication response, potentially leading to account takeover, blind linking, and other security issues.