From Raw Trace to Share-Checked Evidence: The Safety Model Behind AgentInspect
transcript
show notes
This story was originally published on HackerNoon at: https://hackernoon.com/from-raw-trace-to-share-checked-evidence-the-safety-model-behind-agentinspect.
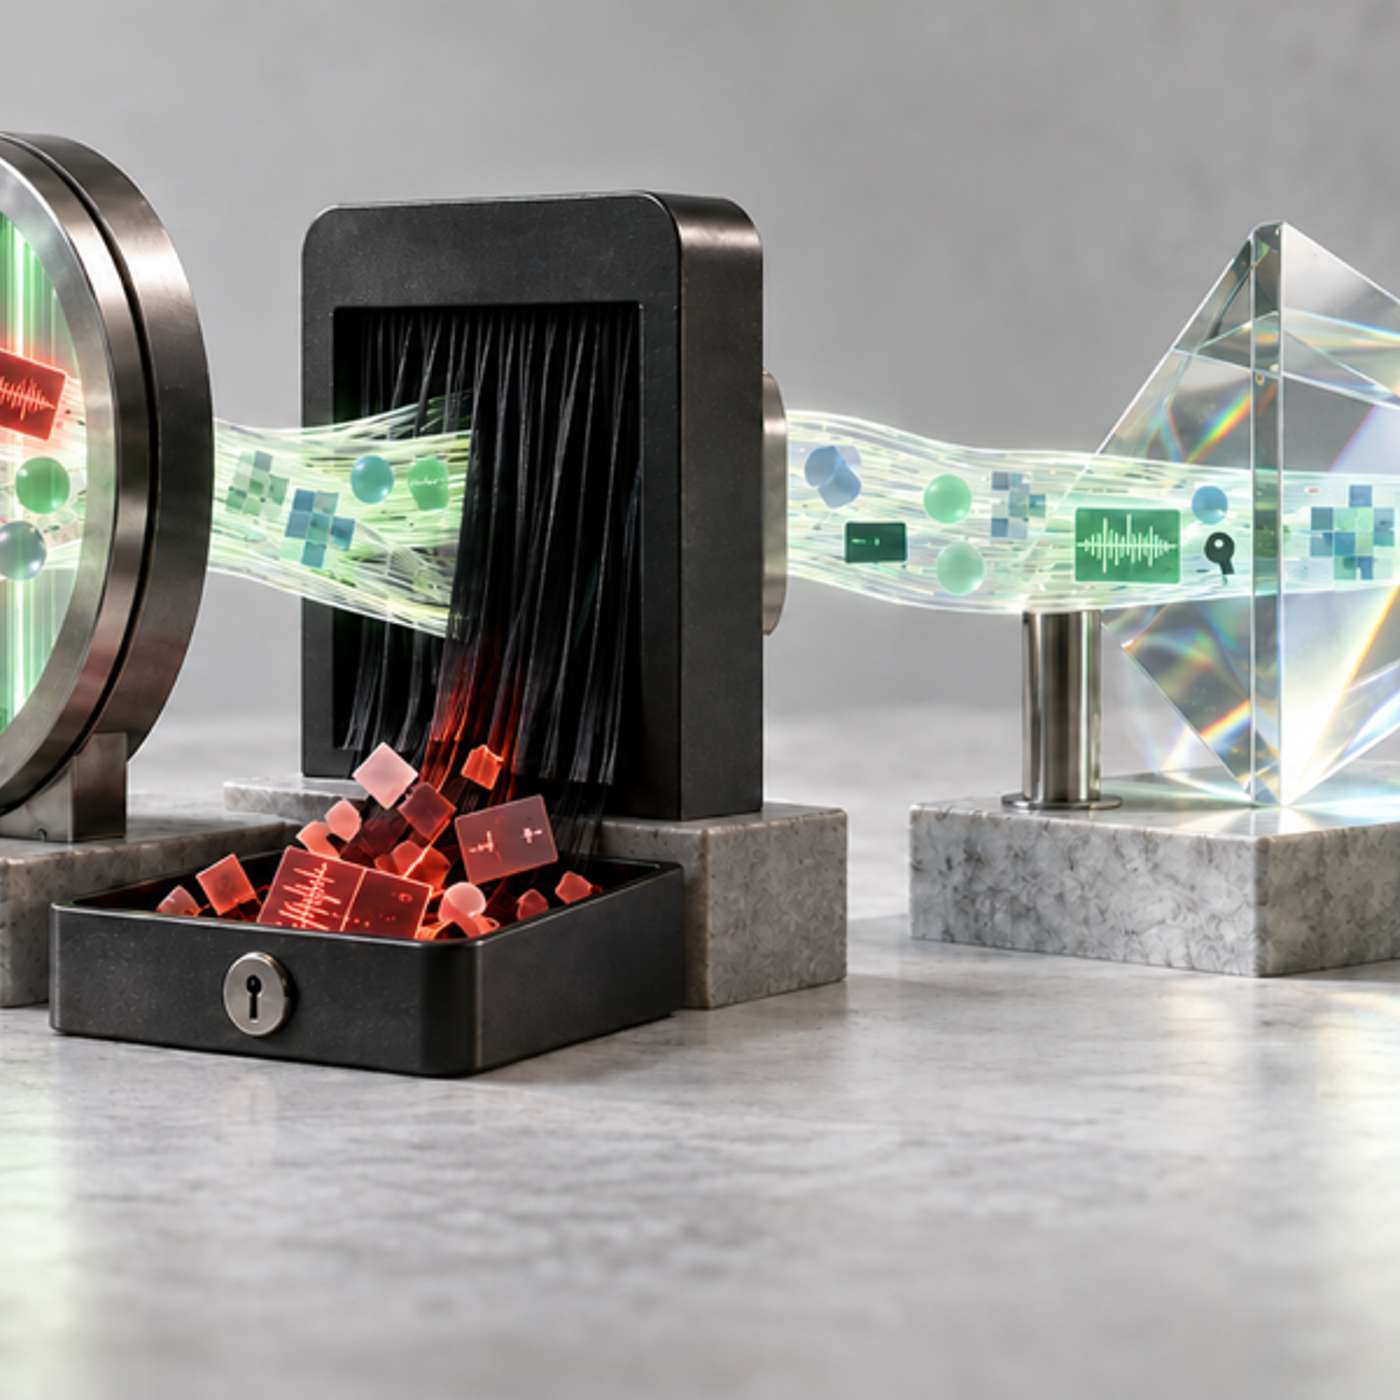
Why local traces are not automatically safe and how assessment, redaction, artifact review, and integrity verification form a safer evidence workflow.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #data-privacy, #cybersecurity, #developer-tools, #software-security, #typescript, #open-source, #ai-agent-observability, #data-redaction, and more.
This story was written by: @rajudandigam. Learn more about this writer by checking @rajudandigam's about page,
and for more stories, please visit hackernoon.com.
Local-first tracing reduces automatic transmission, but it does not make a trace safe to share. This article separates source assessment, redaction, post-redaction artifact review, evidence packaging, and hash verification and explains what each stage cannot prove.