Defending AI Agent Memory Against Persistent Prompt Injection
transcript
show notes
This story was originally published on HackerNoon at: https://hackernoon.com/defending-ai-agent-memory-against-persistent-prompt-injection.
Explore how indirect prompt injection can persist in AI agent memory and why secure ingestion, access controls, and tool-call authorization matter.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #ai-security, #multi-agent-systems, #agent-memory-poisoning, #persistent-prompt-injection, #multi-agent-security, #tool-call-authorization, #zero-trust-ai, #agentic-ai-architecture, and more.
This story was written by: @gunjeetbawa. Learn more about this writer by checking @gunjeetbawa's about page,
and for more stories, please visit hackernoon.com.
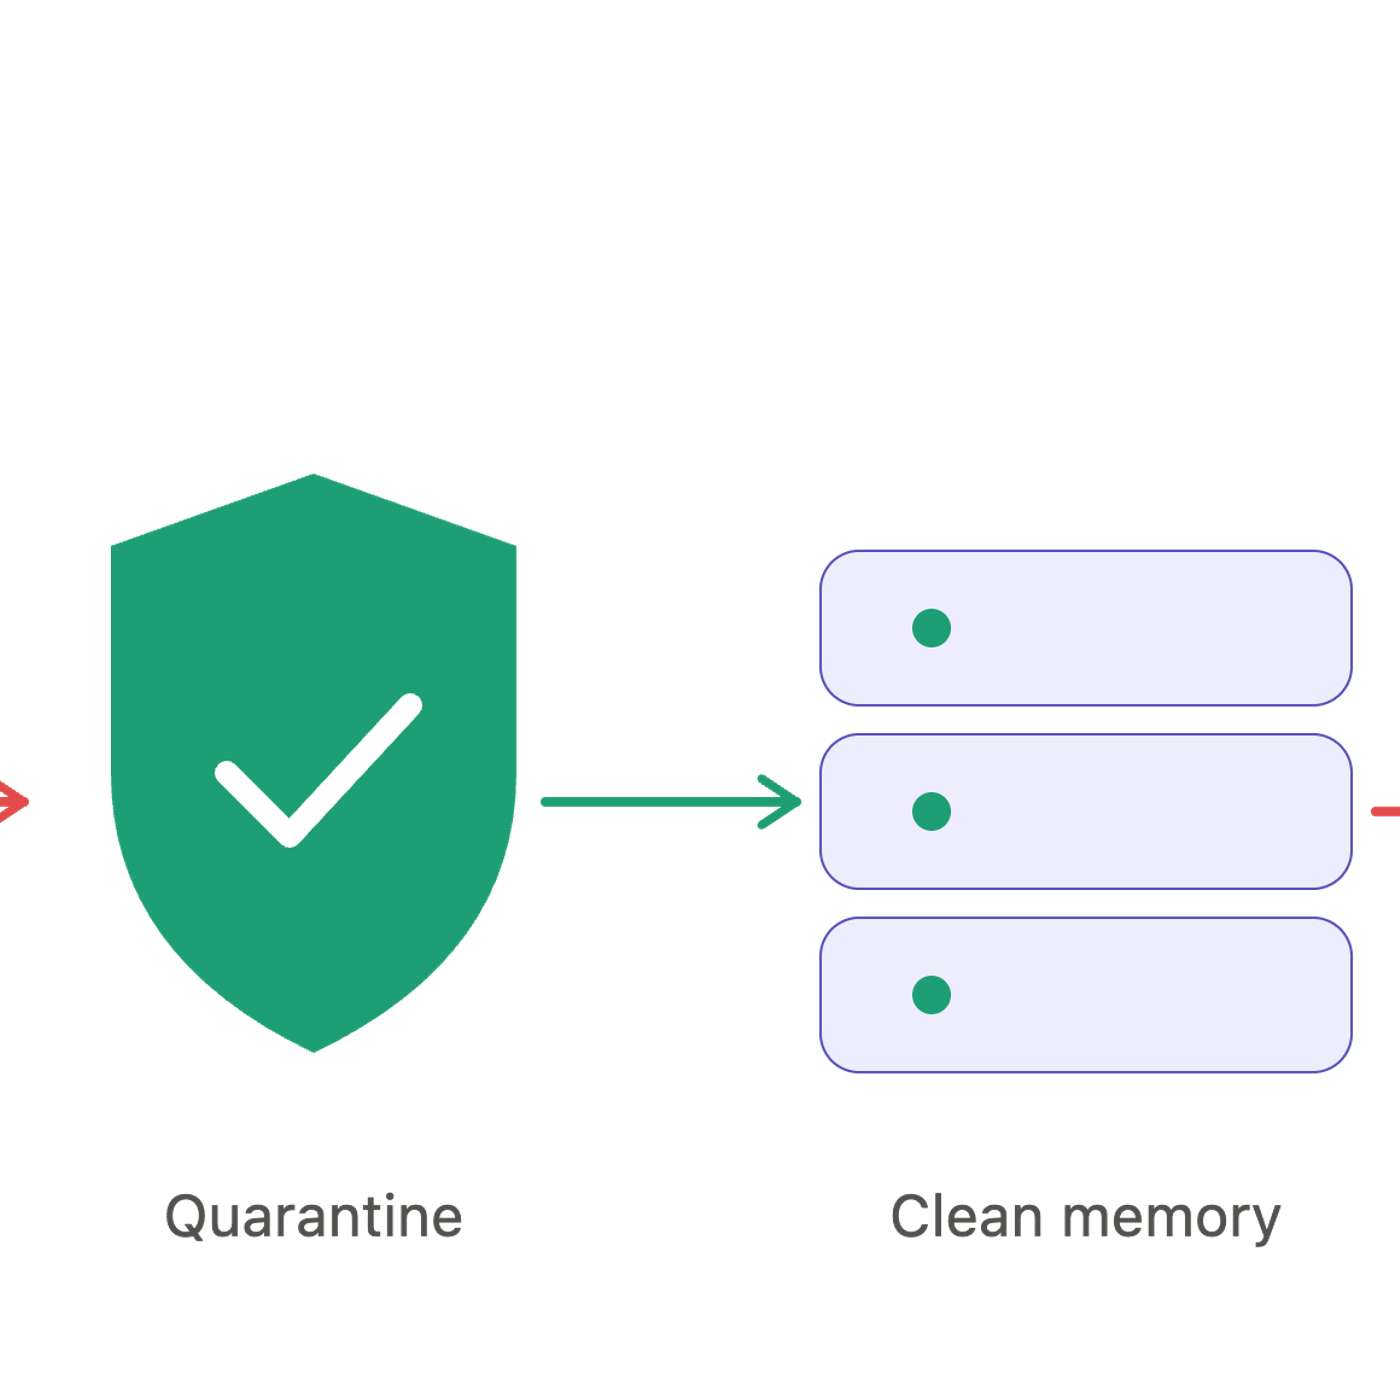
Indirect prompt injection can enter an AI agent through untrusted external content, persist in long-term memory, and influence actions in later sessions. The article proposes a layered defense involving structured input validation, isolated memory processing, and runtime tool-call authorization. However, its effectiveness claims require independent evidence, and the sample implementation does not yet enforce the full security boundaries described.