Skip to content
Artwork for CyberCode Academy
CyberCode Academy · Friday · 14 min

Course 46 - CompTIA Cybersecurity Analyst | Episode 31: Detecting Attacks and Managing Federated Systems

Identity Threat Detection and Federated Identity ArchitectureEpisode OverviewThis episode explores two critical areas of modern identity security: detecting attacks against identity and access management (IAM) systems and designing secure federated identity architectures.It examines how organizations use centralized security telemetry and human analysis to identify suspicious identity activity, then moves into the architecture of federated authentication, where trusted identity providers enable users to access multiple applications without maintaining separate credentials for every service.The episode also compares major federation and identity technologies, including SAML, OAuth 2.0, and Active Directory Federation Services (AD FS), while examining the security and operational risks introduced by reliance on external identity providers.Key Topics Covered1. Detecting Attacks Against Identity SystemsIdentity infrastructure generates valuable security telemetry that can reveal compromised accounts, privilege abuse, and unauthorized changes. IAM Log Integration: Forward authentication, authorization, account-management, and privileged-access events to a SIEM for centralized analysis. Privileged Account Monitoring: Track administrative authentication, privilege elevation, unusual administrative activity, and access to sensitive systems. Permission Changes: Monitor modifications to group memberships, roles, ACLs, and other authorization settings. Identity Lifecycle Events: Monitor account creation, modification, disabling, deletion, and other lifecycle changes. Authentication Anomalies: Investigate unusual login times, locations, devices, authentication methods, or repeated failures. Behavioral Analysis: Compare observed activity against established baselines to identify potentially suspicious deviations. Human Analysis: Automated detection can prioritize and correlate events, but experienced analysts remain important for understanding business context, distinguishing legitimate administrative activity from abuse, and investigating ambiguous patterns. Incident Correlation: Combine IAM telemetry with endpoint, network, application, and cloud-service logs to build a broader picture of potential compromise. 2. Federated Identity ArchitectureFederated identity allows organizations to establish trust relationships between an Identity Provider (IdP) and applications or services operated by another organization.A typical federation involves: Identity Provider (IdP): Authenticates the user and provides identity or authorization information to a relying application. Relying Party (RP): A service or application that relies on assertions or tokens from the trusted identity provider. User: The individual attempting to access the federated service. Trust Relationship: The IdP and relying party establish technical and administrative trust, including configuration of identifiers, keys, endpoints, claims, and validation requirements. Single Sign-On: Once authenticated through the IdP, a user may be able to access multiple participating applications without independently authenticating to each one. Federation can simplify identity management, but it also makes the security and availability of the identity provider particularly important.3. Federation Protocols and FrameworksSAMLSecurity Assertion Markup Language (SAML) is an XML-based standard commonly used to exchange authentication and related identity information between an identity provider and a service provider or relying party.Key concepts include: Authentication assertions Attribute and identity claims XML-based messages Digital signatures Web-based Single Sign-On Trust relationships between participating organizations OAuth 2.0OAuth 2.0 is an authorization framework designed to allow applications to obtain delegated access to protected resources without requiring the resource owner's credentials to be directly shared with the application.Important components include: Resource owner Client Authorization server Resource server Access tokens Scopes and delegated permissions OAuth 2.0 should not be treated as an authentication protocol by itself. OpenID Connect (OIDC) builds an authentication and identity layer on top of OAuth 2.0.Active Directory Federation ServicesAD FS is Microsoft's claims-based federation technology for establishing trust between organizations and applications.It can provide federated authentication and claims-based access in environments that integrate with Microsoft identity infrastructure.4. Managing Third-Party Identity Provider RiskFederation introduces a dependency on the security and availability of external identity providers.Organizations should evaluate: Provider Security: Assess authentication controls, privileged access management, encryption, monitoring, incident response, and security assurance. Availability: Determine how an IdP outage could affect access to critical applications. Account Recovery: Establish secure recovery procedures for users who lose access to their identity provider or authentication factors. Breach Response: Define responsibilities and communication procedures if the external IdP is compromised. Trust Configuration: Protect signing keys, certificates, federation metadata, redirect endpoints, and other federation configuration. Access Revocation: Ensure terminated or compromised identities can be disabled across dependent services in an appropriate timeframe. Contractual Responsibilities: Establish security, notification, audit, availability, and incident-response requirements with the provider. Business Continuity: Maintain appropriate contingency procedures for critical identity dependencies. Identity Detection and Federation WorkflowCollect IAM Events → Centralize Telemetry → Establish Baselines → Detect Anomalies → Investigate → Validate Identity Activity → RespondAuthenticate at IdP → Issue Assertion or Token → Validate Trust → Grant Application Access → Monitor Activity → Revoke or Modify Access When RequiredKey Takeaways Identity systems should be treated as high-value security infrastructure and continuously monitored. IAM logs become significantly more useful when correlated through a SIEM with endpoint, network, application, and cloud telemetry. Privileged-account activity, permission changes, and identity lifecycle events are particularly important sources of security evidence. Human analysts remain important because security events require context and interpretation, not merely automated classification. Federated identity establishes trust between an identity provider and relying parties, allowing users to authenticate through a trusted identity system. SAML is widely used for browser-based federation and SSO, while OAuth 2.0 primarily provides delegated authorization and OpenID Connect adds an authentication/identity layer. AD FS provides Microsoft's claims-based federation capabilities for applicable Microsoft environments. Federation can simplify identity management but creates dependencies on the IdP's security, availability, configuration, and incident-response capabilities. A mature identity strategy therefore combines continuous monitoring, strong federation controls, lifecycle management, third-party risk assessment, and well-defined breach and recovery procedures. You can listen and download our episodes for free on more than 10 different platforms: https://linktr.ee/cybercode_academy

0:00-14:09

transcript

No transcript — this publisher did not publish one.

show notes

Identity Threat Detection and Federated Identity ArchitectureEpisode OverviewThis episode explores two critical areas of modern identity security: detecting attacks against identity and access management (IAM) systems and designing secure federated identity architectures.It examines how organizations use centralized security telemetry and human analysis to identify suspicious identity activity, then moves into the architecture of federated authentication, where trusted identity providers enable users to access multiple applications without maintaining separate credentials for every service.The episode also compares major federation and identity technologies, including SAML, OAuth 2.0, and Active Directory Federation Services (AD FS), while examining the security and operational risks introduced by reliance on external identity providers.Key Topics Covered1. Detecting Attacks Against Identity SystemsIdentity infrastructure generates valuable security telemetry that can reveal compromised accounts, privilege abuse, and unauthorized changes.
  • IAM Log Integration: Forward authentication, authorization, account-management, and privileged-access events to a SIEM for centralized analysis.
  • Privileged Account Monitoring: Track administrative authentication, privilege elevation, unusual administrative activity, and access to sensitive systems.
  • Permission Changes: Monitor modifications to group memberships, roles, ACLs, and other authorization settings.
  • Identity Lifecycle Events: Monitor account creation, modification, disabling, deletion, and other lifecycle changes.
  • Authentication Anomalies: Investigate unusual login times, locations, devices, authentication methods, or repeated failures.
  • Behavioral Analysis: Compare observed activity against established baselines to identify potentially suspicious deviations.
  • Human Analysis: Automated detection can prioritize and correlate events, but experienced analysts remain important for understanding business context, distinguishing legitimate administrative activity from abuse, and investigating ambiguous patterns.
  • Incident Correlation: Combine IAM telemetry with endpoint, network, application, and cloud-service logs to build a broader picture of potential compromise.
2. Federated Identity ArchitectureFederated identity allows organizations to establish trust relationships between an Identity Provider (IdP) and applications or services operated by another organization.A typical federation involves:
  • Identity Provider (IdP): Authenticates the user and provides identity or authorization information to a relying application.
  • Relying Party (RP): A service or application that relies on assertions or tokens from the trusted identity provider.
  • User: The individual attempting to access the federated service.
  • Trust Relationship: The IdP and relying party establish technical and administrative trust, including configuration of identifiers, keys, endpoints, claims, and validation requirements.
  • Single Sign-On: Once authenticated through the IdP, a user may be able to access multiple participating applications without independently authenticating to each one.
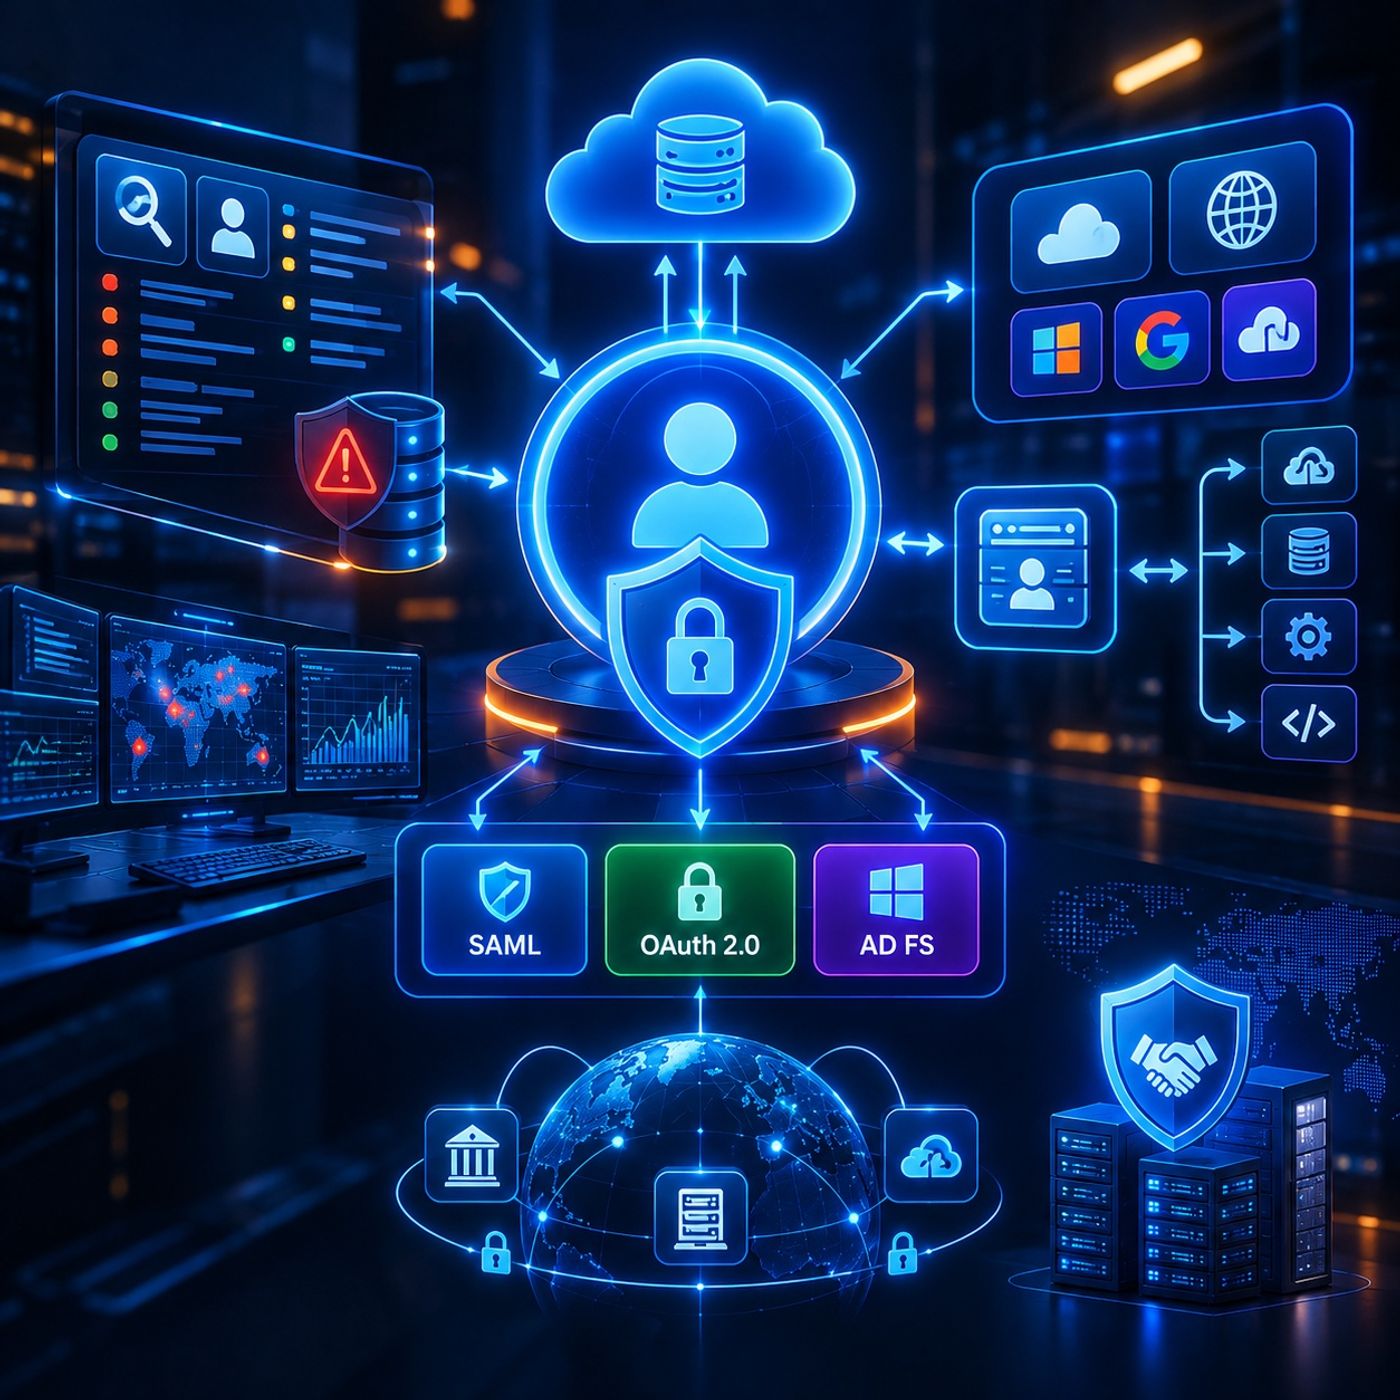
Federation can simplify identity management, but it also makes the security and availability of the identity provider particularly important.3. Federation Protocols and FrameworksSAMLSecurity Assertion Markup Language (SAML) is an XML-based standard commonly used to exchange authentication and related identity information between an identity provider and a service provider or relying party.Key concepts include:
  • Authentication assertions
  • Attribute and identity claims
  • XML-based messages
  • Digital signatures
  • Web-based Single Sign-On
  • Trust relationships between participating organizations
OAuth 2.0OAuth 2.0 is an authorization framework designed to allow applications to obtain delegated access to protected resources without requiring the resource owner's credentials to be directly shared with the application.Important components include:
  • Resource owner
  • Client
  • Authorization server
  • Resource server
  • Access tokens
  • Scopes and delegated permissions
OAuth 2.0 should not be treated as an authentication protocol by itself. OpenID Connect (OIDC) builds an authentication and identity layer on top of OAuth 2.0.Active Directory Federation ServicesAD FS is Microsoft's claims-based federation technology for establishing trust between organizations and applications.It can provide federated authentication and claims-based access in environments that integrate with Microsoft identity infrastructure.4. Managing Third-Party Identity Provider RiskFederation introduces a dependency on the security and availability of external identity providers.Organizations should evaluate:
  • Provider Security: Assess authentication controls, privileged access management, encryption, monitoring, incident response, and security assurance.
  • Availability: Determine how an IdP outage could affect access to critical applications.
  • Account Recovery: Establish secure recovery procedures for users who lose access to their identity provider or authentication factors.
  • Breach Response: Define responsibilities and communication procedures if the external IdP is compromised.
  • Trust Configuration: Protect signing keys, certificates, federation metadata, redirect endpoints, and other federation configuration.
  • Access Revocation: Ensure terminated or compromised identities can be disabled across dependent services in an appropriate timeframe.
  • Contractual Responsibilities: Establish security, notification, audit, availability, and incident-response requirements with the provider.
  • Business Continuity: Maintain appropriate contingency procedures for critical identity dependencies.
Identity Detection and Federation WorkflowCollect IAM Events → Centralize Telemetry → Establish Baselines → Detect Anomalies → Investigate → Validate Identity Activity → RespondAuthenticate at IdP → Issue Assertion or Token → Validate Trust → Grant Application Access → Monitor Activity → Revoke or Modify Access When RequiredKey Takeaways
  • Identity systems should be treated as high-value security infrastructure and continuously monitored.
  • IAM logs become significantly more useful when correlated through a SIEM with endpoint, network, application, and cloud telemetry.
  • Privileged-account activity, permission changes, and identity lifecycle events are particularly important sources of security evidence.
  • Human analysts remain important because security events require context and interpretation, not merely automated classification.
  • Federated identity establishes trust between an identity provider and relying parties, allowing users to authenticate through a trusted identity system.
  • SAML is widely used for browser-based federation and SSO, while OAuth 2.0 primarily provides delegated authorization and OpenID Connect adds an authentication/identity layer.
  • AD FS provides Microsoft's claims-based federation capabilities for applicable Microsoft environments.
  • Federation can simplify identity management but creates dependencies on the IdP's security, availability, configuration, and incident-response capabilities.
  • A mature identity strategy therefore combines continuous monitoring, strong federation controls, lifecycle management, third-party risk assessment, and well-defined breach and recovery procedures.


You can listen and download our episodes for free on more than 10 different platforms:
https://linktr.ee/cybercode_academy
links1