CyberCode Academy · Yesterday · 17 min
Course 46 - CompTIA Cybersecurity Analyst | Episode 25: Mastering Layered Defense & Security Controls
0:00-17:58
transcript
show notes
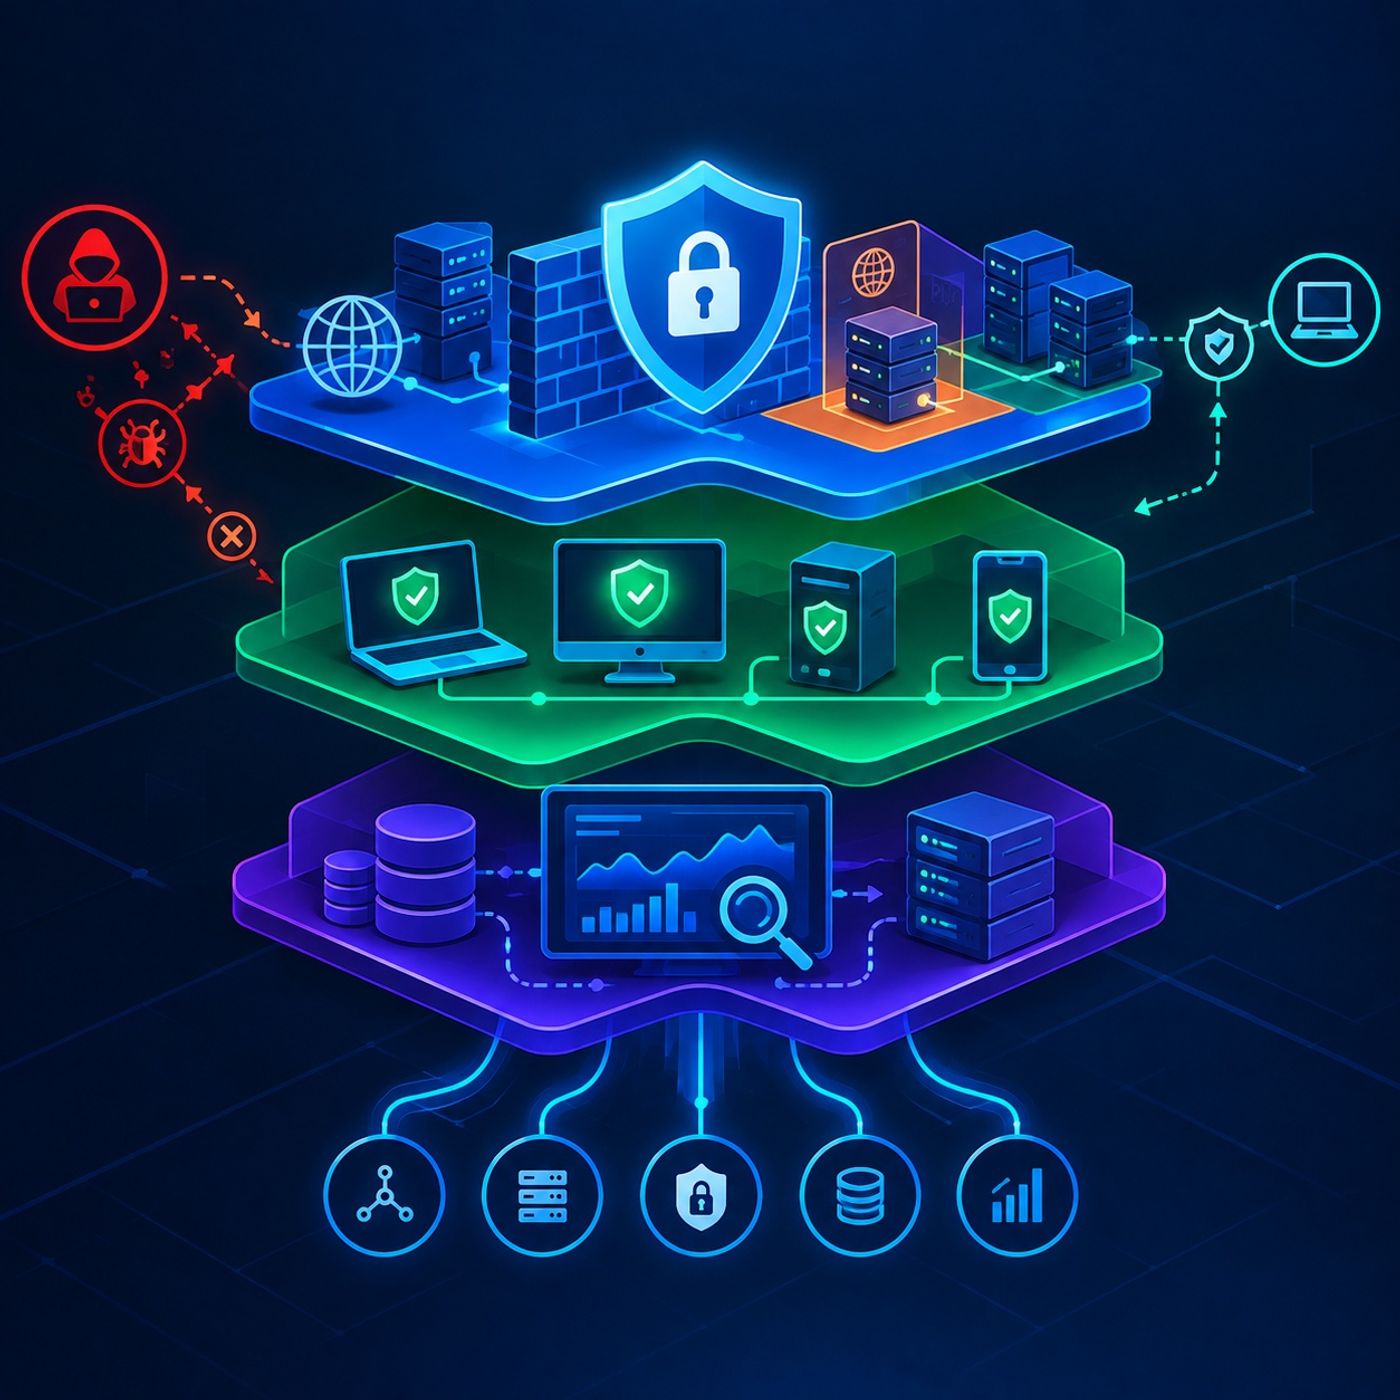
Frameworks for Network Security: Defensive Architectures and Security ControlsEpisode OverviewThis episode examines the fundamental frameworks used to build a resilient network security posture through defense in depth, layered security architectures, and security controls.It explores how organizations combine technical safeguards, administrative processes, and operational practices to reduce risk across networks, systems, applications, and sensitive information. The episode also emphasizes an important principle of security architecture: controls must provide meaningful protection without unnecessarily disrupting legitimate business operations.Key Topics Covered1. Defense in Depth
You can listen and download our episodes for free on more than 10 different platforms:
https://linktr.ee/cybercode_academy
- Layered Security: Understand how multiple security layers work together so that the failure or bypass of one control does not automatically result in compromise.
- Perimeter Protection: Examine border routers, firewalls, and other network-edge controls used to regulate traffic entering and leaving an environment.
- Network Detection and Prevention: Explore IDS/IPS technologies for identifying and, where appropriate, blocking suspicious network activity.
- Endpoint Security: Incorporate endpoint protection, host-based controls, secure configurations, and patch management into the broader defensive architecture.
- Application Security: Maintain secure applications through vulnerability management, secure configuration, and timely security updates.
- Security vs. Business Operations: Balance protective controls with availability, usability, performance, and operational requirements to avoid creating security measures that unnecessarily interfere with legitimate business processes.
- Uniform Protection: Apply a consistent baseline of security controls across assets where similar protection requirements exist.
- Protected Enclaves: Isolate particularly sensitive systems or environments—such as payment-card or critical-data systems—with additional controls and segmentation.
- Risk- or Threat-Based Architecture: Prioritize controls according to specific threats, attack paths, exposure levels, and organizational risk.
- Information Classification-Based Architecture: Match security protections to the sensitivity and classification of the information being processed or stored.
- Firewalls
- Authentication and access-control systems
- Endpoint security and anti-malware technologies
- Network segmentation
- Encryption
- IDS/IPS
- Security monitoring systems
- Security policies
- Standards and procedures
- Risk-management processes
- Security awareness and training
- Vendor and third-party requirements
- Compliance and legal obligations
- Preventive Controls: Designed to reduce the likelihood of an unwanted event, such as firewalls, access controls, and secure configurations.
- Detective Controls: Identify events or conditions that may indicate a security problem, including IDS, monitoring systems, and audit logs.
- Directive Controls: Guide users and administrators toward required security behavior through policies, procedures, standards, and security instructions.
- Compensating Controls: Provide an alternative safeguard when a preferred control cannot be implemented or cannot adequately address a particular requirement.
- Defense in depth reduces dependence on any single security mechanism.
- Network, endpoint, application, and administrative safeguards should operate as complementary layers.
- Sensitive environments may require additional segmentation and protected enclaves beyond the organization's general security baseline.
- Security architecture can be organized around uniform protection, protected enclaves, threat/risk priorities, or information classification.
- Security controls can be categorized by both implementation type and security function.
- Technical controls provide technological enforcement, while administrative controls establish the policies, processes, and governance that support secure operations.
- Preventive, detective, directive, and compensating controls address different security objectives and are often used together.
- Effective security architecture must account for both security requirements and legitimate business needs.
You can listen and download our episodes for free on more than 10 different platforms:
https://linktr.ee/cybercode_academy
links1