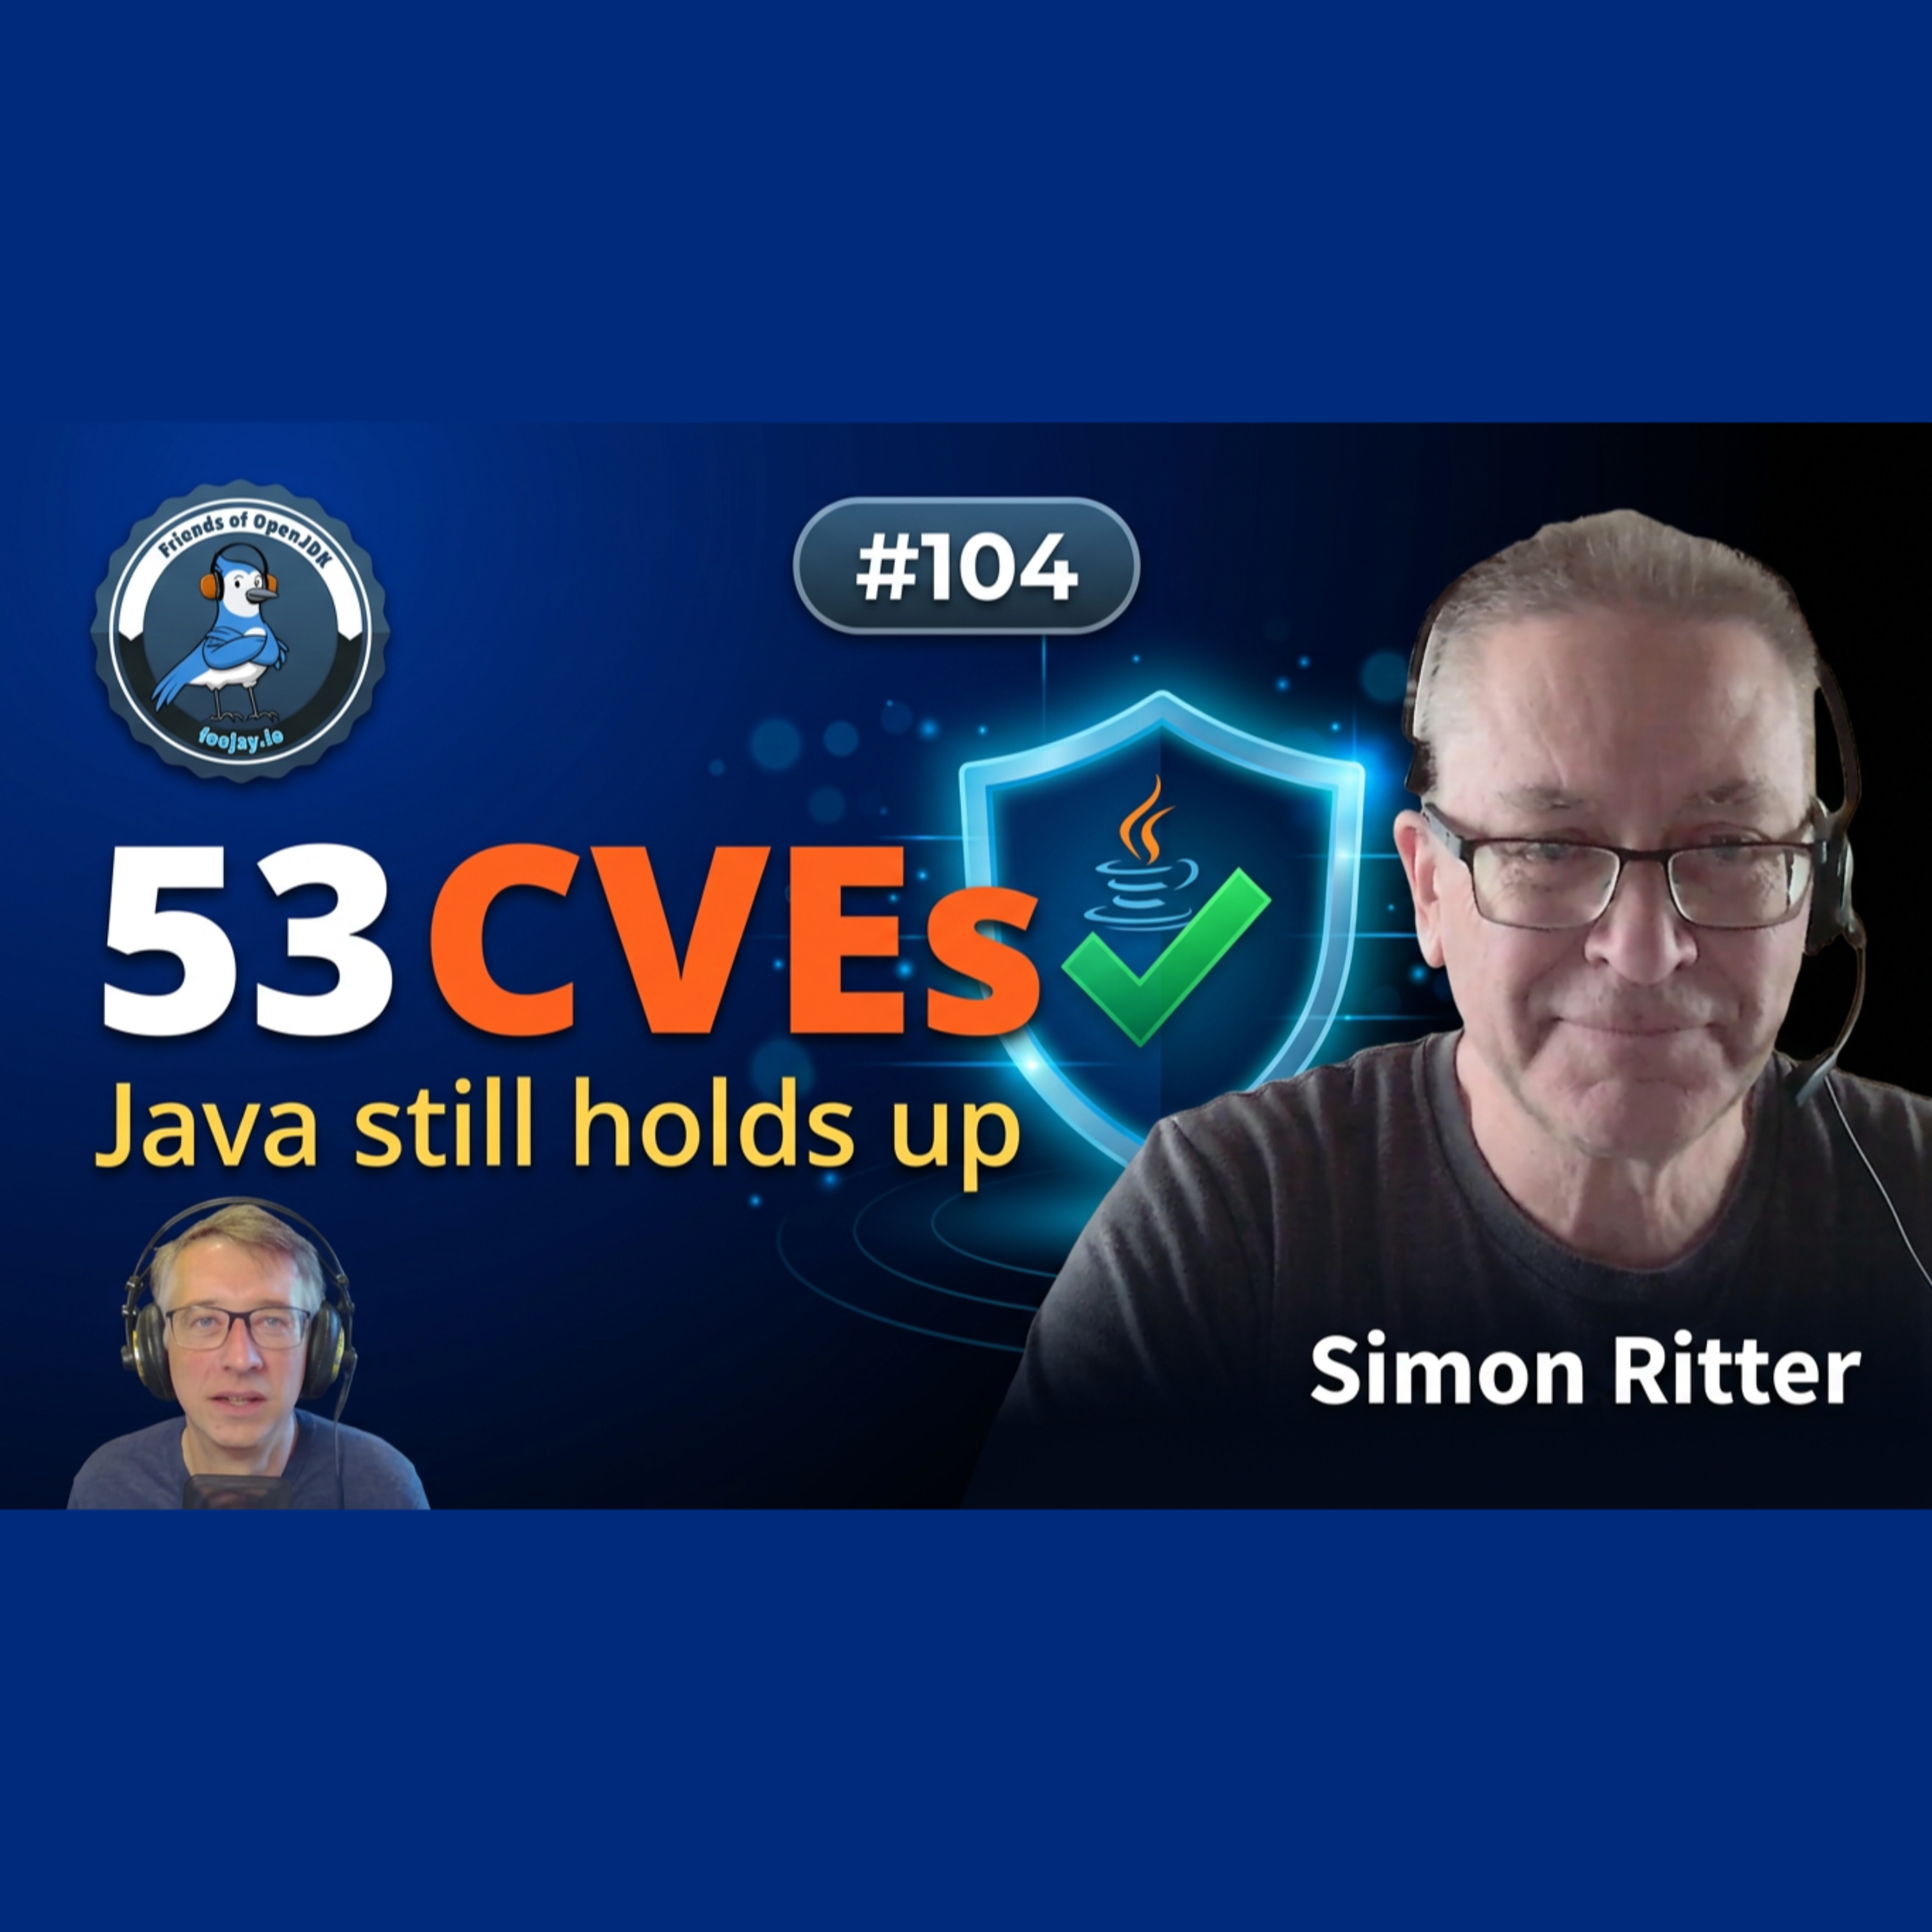
53 CVEs and Two Emergency Releases: Why Java Security Holds Up (#104)
transcript
show notes
A record 53 CVEs in one Java update, followed by two emergency releases within days. Yes, a lot of issues are being found, but Java is still strong: a whole community and the commercial distributors are behind every fix.
In this episode, Simon Ritter, Deputy CTO at Azul, Java Champion and member of the OpenJDK Vulnerability Group, explains what happened over the past weeks and what it means for your applications. We cover how a vulnerability travels from a report to a patch, why AI is changing the number of fixes, and why you should be ready to update at any moment. If you want to understand how CVEs are handled behind the scenes and what the different types of security updates mean, this episode explains it.
Topics include:
- What a CVE and a CVSS score really tell you, and why low scores can be chained into serious attacks
- How vulnerabilities are kept secret and encrypted in the OpenJDK Vulnerability Group until a patch exists
- Why the average of 7.6 CVEs per quarter jumped to 53, and the move toward monthly security updates
- The eMudhra certificate problem and the two out-of-cycle releases that followed
- The backporting workload behind every supported Java version, from 27 down to 6
- CPU, PSU and CSPU explained, and what free versus paid OpenJDK builds mean for your patching
Guest: Simon Ritter
Deputy CTO at Azul and Java Champion
Simon on LinkedIn
Links:
Full show notes with all links
Free Java, Real Risk: Why Unsupported OpenJDK Is Now a Security Gamble
Azul Zulu October 2026 Quarterly Update and Out-of-Cycle Release
Timestamps:
00:00 Introduction of topic and guest
01:59 What is a CVE and how are they reported and handled?
08:45 How the Java security release cycle is changing and each have more CVEs
11:48 How AI impacts the discovery of CVEs
14:09 What was the eMudhra problem causing two out-of-cycle security updates?
21:49 The impact of creating an out-of-cycle update (and backports)
26:05 How safe will OpenJDK builds be in the future? And dependencies?
29:06 Free versus paid versions of OpenJDK builds
32:40 CPU vs PSU vs CSPU: the names used for different types of security updates (security only versus including patches)
35:52 What will happen with old Java versions like 6, 7, 8
37:05 Why would you pay for a supported OpenJDK build?
41:50 Conclusion: check your Java version and be ready to update at any moment!