Evolution Exchange Denmark Podcast · October 9 · 49 min
Evo DK #470 - What Does A CISO Really Do In 2026
0:00-49:01
transcript
show notes
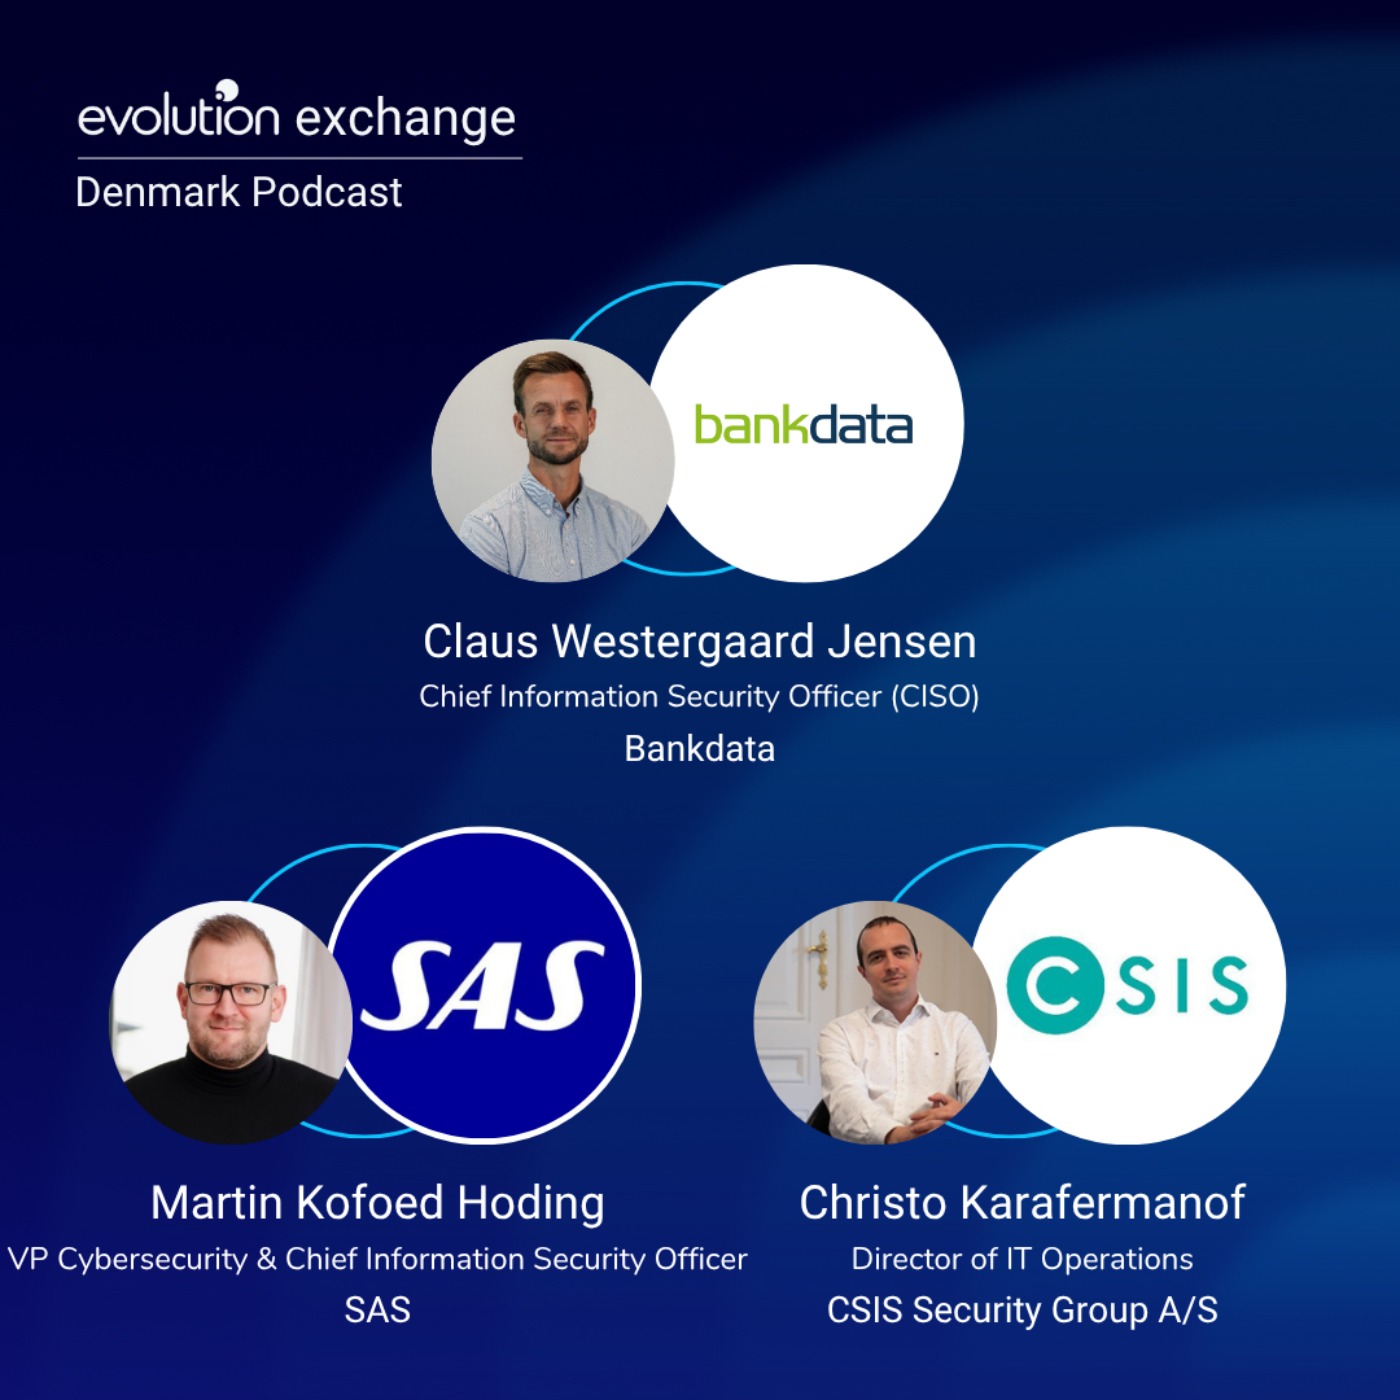
Today's episode is hosted by Kyle Chapman and they are joined on the podcast by Claus Westergaard Jensen, Chief Information Security Officer (CISO) at Bankdata, Martin Kofoed Hoding, VP Cybersecurity & Chief Information Security Officer at SAS and Christo Karafermanof, Director of IT Operations at CSIS Security Group A/S. The conversation explores the evolving responsibilities of cybersecurity leadership in 2026, examining how organisations approach information security, cyber risk management and digital resilience. The discussion considers the growing importance of strategic decision-making, security governance and balancing business priorities with increasingly complex cyber threats. The exchange also highlights the wider challenges facing a modern CISO, including regulatory compliance, enterprise security, stakeholder collaboration and the relationship between IT operations and cybersecurity strategy. With organisations navigating a rapidly changing threat landscape, the discussion offers perspectives on how security leadership continues to evolve and why effective risk management, organisational resilience and strong security practices remain essential to protecting modern businesses.
Hosted on Acast. See acast.com/privacy for more information.
links1