Skip to content
Artwork for CyberCode Academy
CyberCode Academy · Yesterday · 12 min

Course 46 - CompTIA Cybersecurity Analyst | Episode 32: Secure Software Development

Foundations of Secure Software DevelopmentEpisode OverviewThis episode explores how security can be integrated throughout the software development process, connecting the Software Development Life Cycle (SDLC), common development methodologies, and practical secure coding principles. It emphasizes the importance of addressing security early rather than treating it as an afterthought during deployment or maintenance.Key Topics Covered1. The Software Development Life Cycle (SDLC)The episode examines the major stages of the software lifecycle: Planning and Feasibility — defining business objectives, scope, resources, and constraints. Requirements Analysis — identifying functional, technical, and cybersecurity requirements. System and Application Design — incorporating secure architecture, access controls, data protection, and threat considerations. Development — implementing functionality according to secure coding standards. Testing and Validation — performing functional, security, integration, and user acceptance testing. Deployment, Training, and Transition — moving the application into operational use while preparing users and administrators. Operations and Maintenance — monitoring, patching, fixing defects, addressing vulnerabilities, and adapting to changing requirements. Retirement — securely decommissioning applications, systems, credentials, data, and supporting infrastructure. A central theme is shifting security left: security requirements, threat analysis, and architectural controls should be considered early in the lifecycle rather than postponed until after the application has already been built. Maintenance can represent a substantial portion of total lifecycle effort, but exact percentages vary by project and development environment.2. Software Development ModelsThe episode compares several approaches to organizing software development: Waterfall — sequential progression through defined phases. V-Model — emphasizes corresponding verification and validation activities alongside development stages. Spiral — iterative development centered on risk identification and mitigation. Rapid Application Development (RAD) — emphasizes rapid prototyping and iterative user feedback. Agile — iterative and incremental delivery through short development cycles. Big Bang — minimal formal planning or structure, carrying significant project and quality risks. Agile concepts covered include product backlogs, user stories, sprint planning, planning poker, timeboxing, and velocity. Sprint duration can vary by organization; a 30-day sprint is one possible implementation rather than a universal requirement. Velocity is primarily a historical planning metric rather than a direct measure of individual developer productivity.3. Secure Coding and Application DefenseThe episode then moves from lifecycle theory into practical application security. Key practices include: Establishing organizational security policies and coding standards. Performing threat and risk assessments during development. Validating and safely handling untrusted input. Preventing SQL injection through parameterized queries and appropriate database access controls. Defending against cross-site scripting (XSS) through context-appropriate output encoding and additional browser-side protections such as Content Security Policy where appropriate. Designing informative but non-sensitive error messages. Implementing multi-factor authentication for appropriate accounts and applications. Protecting sessions through secure session management and appropriate cookie controls. Using HTTPS/TLS to protect data in transit. Hardening the underlying operating systems, servers, databases, and deployment infrastructure. Applying established security guidance such as the OWASP application security resources. Using version-control systems such as Git or Subversion to track changes, support code review, improve accountability, and provide a reliable development history. Incorporating modern practices such as dependency management, secret protection, automated security testing, and security-focused code review. Secure Development WorkflowPlan → Define Security Requirements → Assess Risk → Design Securely → Develop → Test → Review → Deploy → Monitor → Maintain → RetireKey Takeaways Security should be considered throughout the entire SDLC, not added only after development is complete. Different development models provide different approaches to planning, iteration, testing, and risk management. Secure coding requires more than input validation; applications need layered defenses across authentication, authorization, sessions, data handling, error management, and infrastructure. Parameterized queries are a fundamental defense against SQL injection. XSS protection requires context-appropriate output encoding and other application/browser security controls. Version control improves traceability, collaboration, review, and accountability. Secure software development is a continuous process that extends from initial planning through deployment, maintenance, and retirement. You can listen and download our episodes for free on more than 10 different platforms: https://linktr.ee/cybercode_academy

0:00-12:24

transcript

No transcript — this publisher did not publish one.

show notes

Foundations of Secure Software DevelopmentEpisode OverviewThis episode explores how security can be integrated throughout the software development process, connecting the Software Development Life Cycle (SDLC), common development methodologies, and practical secure coding principles. It emphasizes the importance of addressing security early rather than treating it as an afterthought during deployment or maintenance.Key Topics Covered1. The Software Development Life Cycle (SDLC)The episode examines the major stages of the software lifecycle:
  • Planning and Feasibility — defining business objectives, scope, resources, and constraints.
  • Requirements Analysis — identifying functional, technical, and cybersecurity requirements.
  • System and Application Design — incorporating secure architecture, access controls, data protection, and threat considerations.
  • Development — implementing functionality according to secure coding standards.
  • Testing and Validation — performing functional, security, integration, and user acceptance testing.
  • Deployment, Training, and Transition — moving the application into operational use while preparing users and administrators.
  • Operations and Maintenance — monitoring, patching, fixing defects, addressing vulnerabilities, and adapting to changing requirements.
  • Retirement — securely decommissioning applications, systems, credentials, data, and supporting infrastructure.
A central theme is shifting security left: security requirements, threat analysis, and architectural controls should be considered early in the lifecycle rather than postponed until after the application has already been built. Maintenance can represent a substantial portion of total lifecycle effort, but exact percentages vary by project and development environment.2. Software Development ModelsThe episode compares several approaches to organizing software development:
  • Waterfall — sequential progression through defined phases.
  • V-Model — emphasizes corresponding verification and validation activities alongside development stages.
  • Spiral — iterative development centered on risk identification and mitigation.
  • Rapid Application Development (RAD) — emphasizes rapid prototyping and iterative user feedback.
  • Agile — iterative and incremental delivery through short development cycles.
  • Big Bang — minimal formal planning or structure, carrying significant project and quality risks.
Agile concepts covered include product backlogs, user stories, sprint planning, planning poker, timeboxing, and velocity. Sprint duration can vary by organization; a 30-day sprint is one possible implementation rather than a universal requirement. Velocity is primarily a historical planning metric rather than a direct measure of individual developer productivity.3. Secure Coding and Application DefenseThe episode then moves from lifecycle theory into practical application security. Key practices include:
  • Establishing organizational security policies and coding standards.
  • Performing threat and risk assessments during development.
  • Validating and safely handling untrusted input.
  • Preventing SQL injection through parameterized queries and appropriate database access controls.
  • Defending against cross-site scripting (XSS) through context-appropriate output encoding and additional browser-side protections such as Content Security Policy where appropriate.
  • Designing informative but non-sensitive error messages.
  • Implementing multi-factor authentication for appropriate accounts and applications.
  • Protecting sessions through secure session management and appropriate cookie controls.
  • Using HTTPS/TLS to protect data in transit.
  • Hardening the underlying operating systems, servers, databases, and deployment infrastructure.
  • Applying established security guidance such as the OWASP application security resources.
  • Using version-control systems such as Git or Subversion to track changes, support code review, improve accountability, and provide a reliable development history.
  • Incorporating modern practices such as dependency management, secret protection, automated security testing, and security-focused code review.
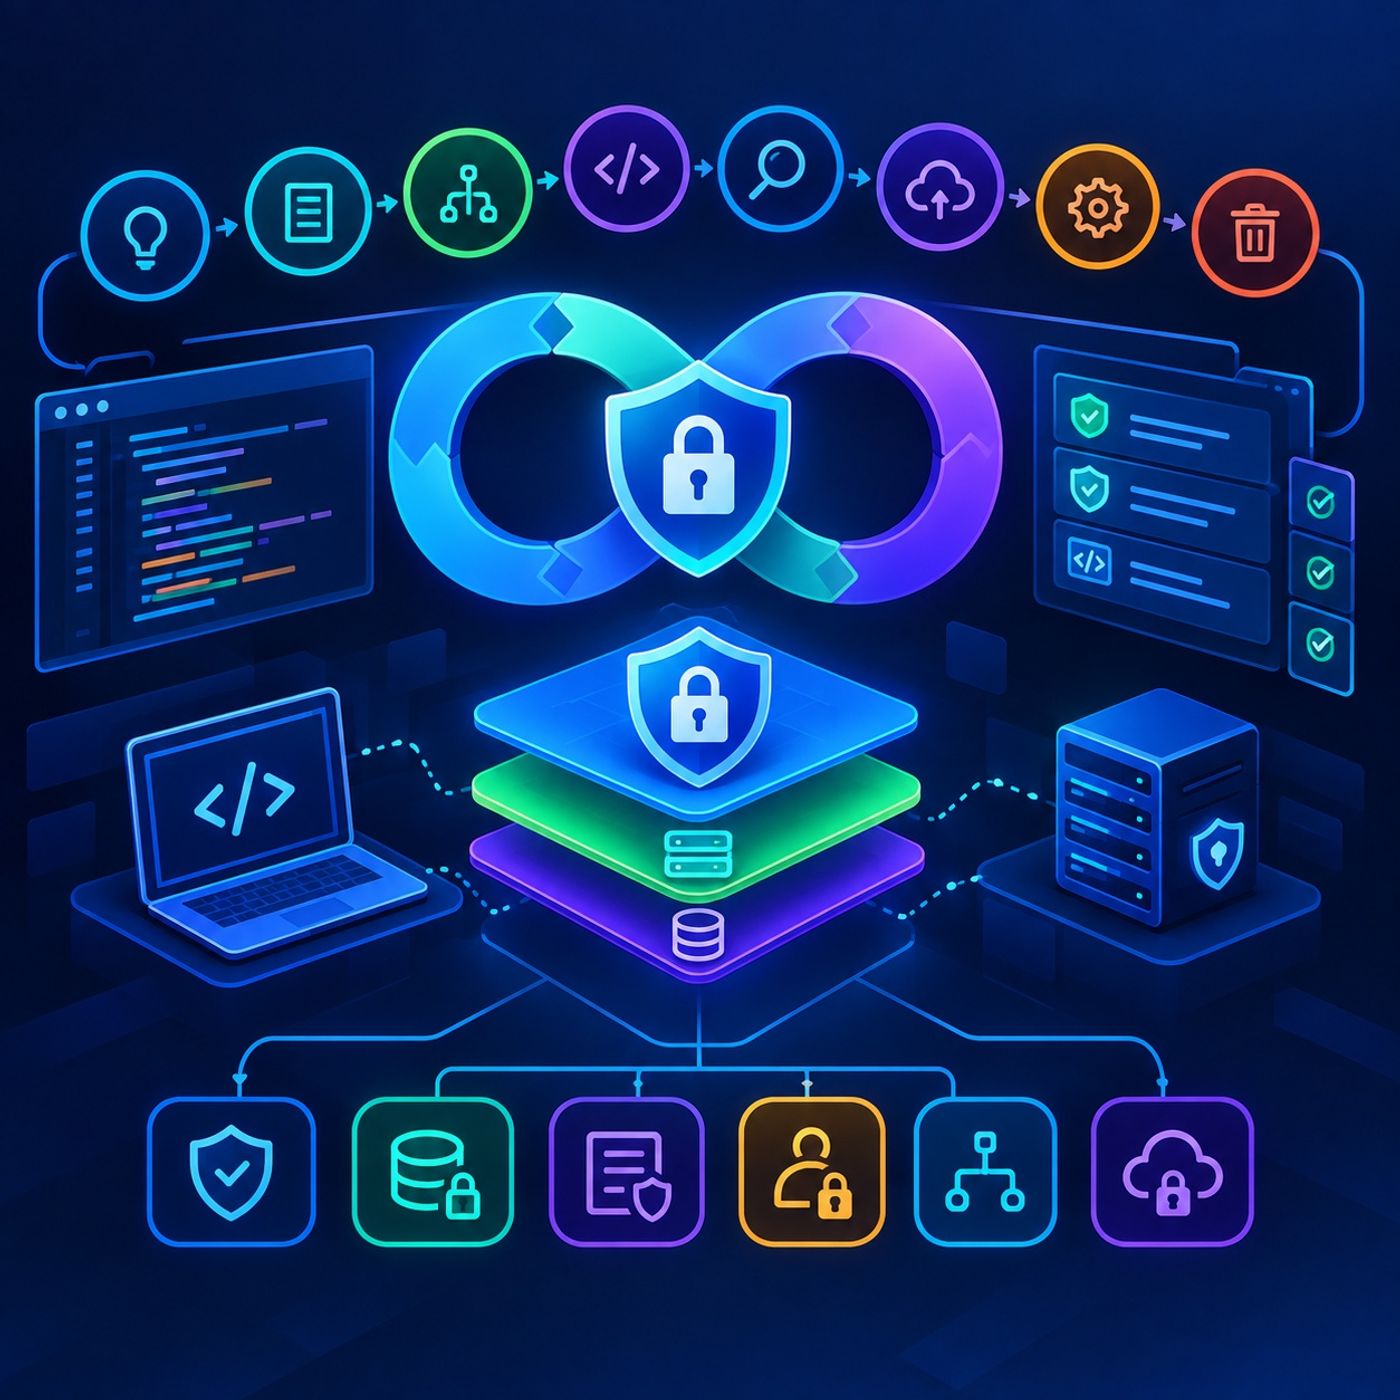
Secure Development WorkflowPlan → Define Security Requirements → Assess Risk → Design Securely → Develop → Test → Review → Deploy → Monitor → Maintain → RetireKey Takeaways
  • Security should be considered throughout the entire SDLC, not added only after development is complete.
  • Different development models provide different approaches to planning, iteration, testing, and risk management.
  • Secure coding requires more than input validation; applications need layered defenses across authentication, authorization, sessions, data handling, error management, and infrastructure.
  • Parameterized queries are a fundamental defense against SQL injection.
  • XSS protection requires context-appropriate output encoding and other application/browser security controls.
  • Version control improves traceability, collaboration, review, and accountability.
  • Secure software development is a continuous process that extends from initial planning through deployment, maintenance, and retirement.


You can listen and download our episodes for free on more than 10 different platforms:
https://linktr.ee/cybercode_academy
links1