CyberCode Academy · Yesterday · 20 min
Course 46 - CompTIA Cybersecurity Analyst | Episode 3: Measuring and Managing Risk
0:00-20:42
transcript
show notes
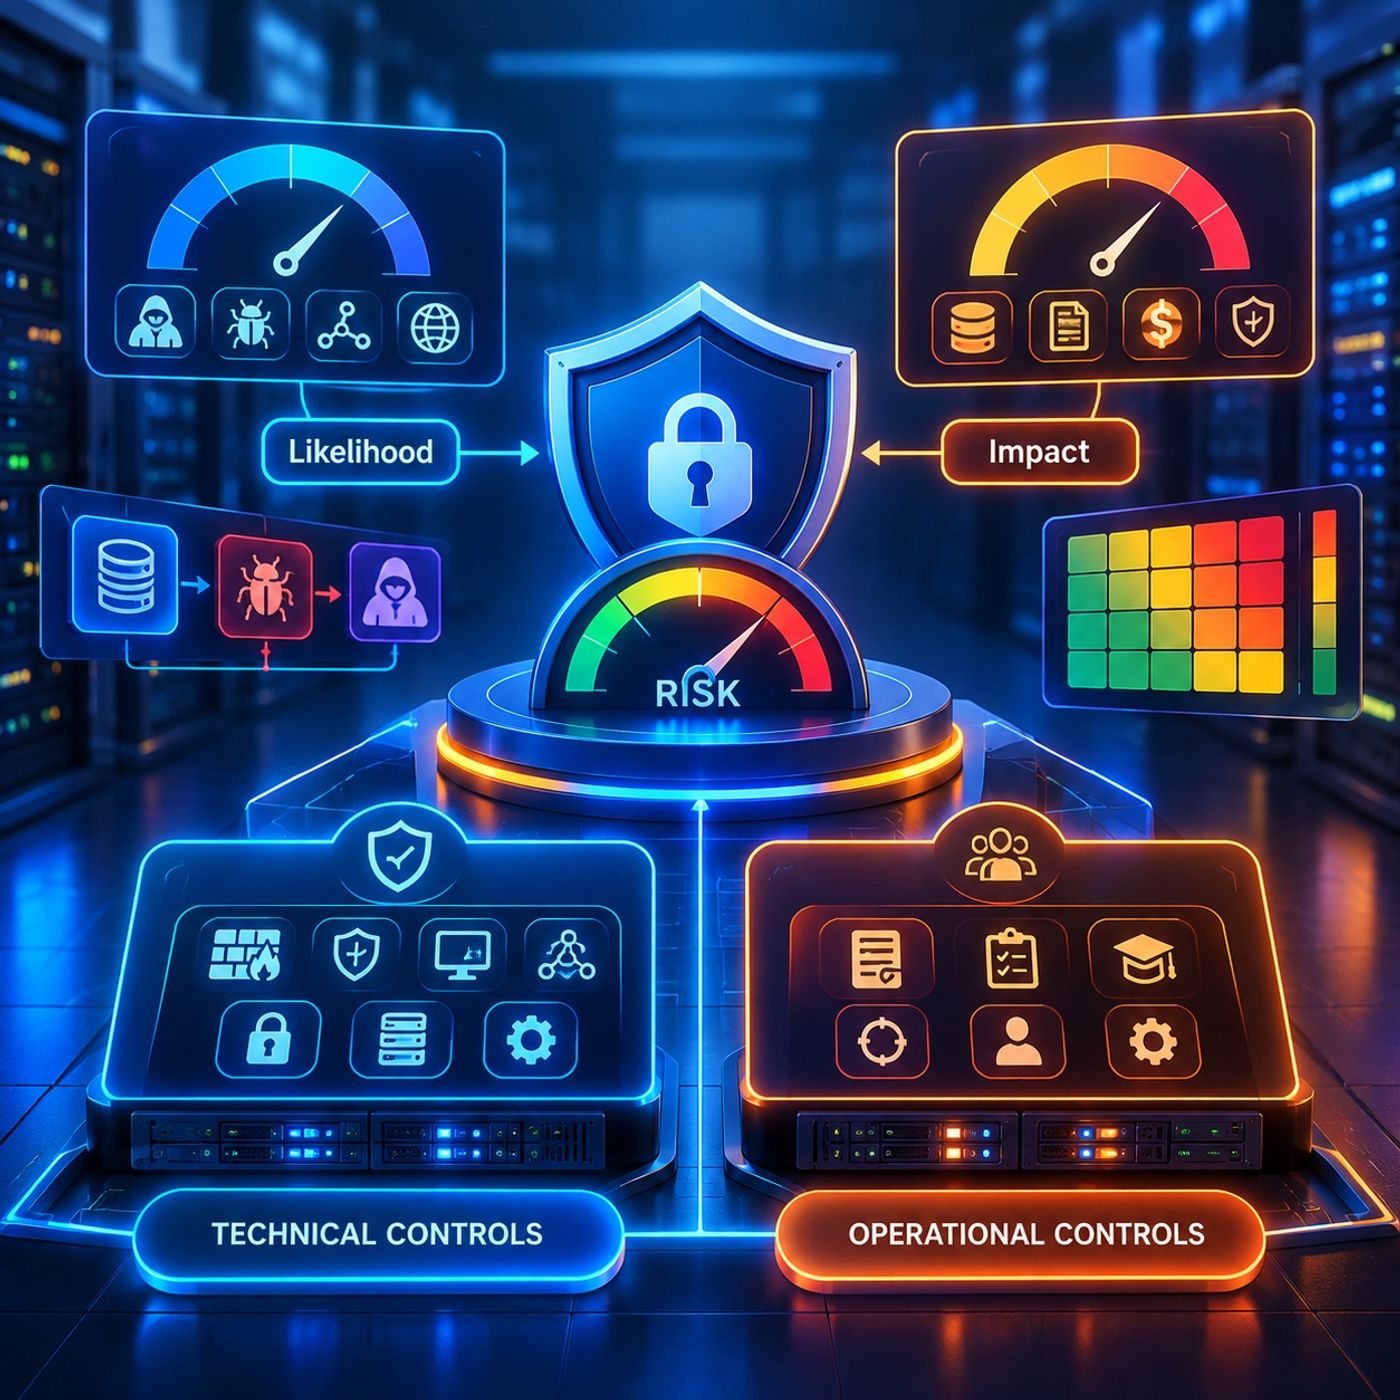
Measuring and Managing Cybersecurity Risk: Likelihood, Assessment, and ControlsEpisode OverviewThis episode moves from identifying cybersecurity risks to understanding how organizations measure, prioritize, and manage those risks.Building on the previous discussion of threats, vulnerabilities, assets, likelihood, and impact, this lesson provides a practical framework for determining how significant a particular risk may be and what actions an organization can take in response.The episode examines the relationship between likelihood and impact, compares qualitative and quantitative risk assessments, introduces four fundamental risk response strategies, and explores how technical and operational security controls can reduce exposure to an acceptable level.The central objective is to transform security findings into actionable risk-management decisions.1. Understanding Likelihood and ImpactRisk assessment begins with two fundamental questions:How likely is the event to occur?andHow significant would the consequences be if it occurred?These concepts are commonly represented as:Risk ≈ Likelihood × ImpactLikelihoodLikelihood represents the probability or estimated possibility that a threat event will occur and affect the organization.Factors influencing likelihood can include:
- Threat capability.
- Threat motivation.
- System exposure.
- Existing vulnerabilities.
- Security controls.
- Historical activity.
- Accessibility of the target.
ImpactImpact represents the consequences of a successful threat event.These consequences can affect:
- Confidentiality
- Integrity
- Availability
- Financial performance.
- Business operations.
- Reputation.
- Regulatory obligations.
Considering both dimensions allows organizations to distinguish between minor security issues and risks that could have significant business consequences.2. The Relationship Between Threats, Vulnerabilities, and RiskA risk does not exist simply because a vulnerability has been discovered.Risk emerges from the interaction between multiple factors:Asset→ Vulnerability→ Threat→ Likelihood→ Impact→ RiskFor example, a vulnerable internet-facing application may represent a much greater organizational risk when it protects sensitive business data than when the same vulnerability exists on an isolated laboratory system.This is why risk assessment must consider business context, rather than relying exclusively on technical severity.3. Qualitative Risk AssessmentA qualitative risk assessment evaluates risk using descriptive categories rather than precise financial measurements.Common classifications include:
- Low.
- Medium.
- High.
- Very High or Critical, depending on the organization's methodology.
A simple risk matrix might combine likelihood and impact:LikelihoodImpactRisk InterpretationLowLowLower-priority riskLowHighRequires consideration because of potential consequencesHighLowRequires consideration because of frequencyHighHighSignificant risk requiring appropriate treatmentThe exact classification criteria should be defined by the organization's risk-management methodology.AdvantagesQualitative assessment is useful because it is:
- Relatively fast.
- Easy to communicate.
- Practical when reliable financial data is unavailable.
- Suitable for large numbers of risks.
Its limitation is that ratings can involve analyst judgment and may be less precise when comparing risks with very different financial consequences.4. Quantitative Risk AssessmentA quantitative risk assessment attempts to express risk using numerical values.Instead of simply stating that a risk is "high," analysts can estimate potential financial exposure.One commonly discussed model is Annual Loss Expectancy (ALE).A simplified calculation is:ALE = Single Loss Expectancy (SLE) × Annual Rate of Occurrence (ARO)Where:
- SLE estimates the loss from one occurrence.
- ARO estimates how frequently the event is expected to occur each year.
- ALE estimates the expected annualized loss.
For example, if a particular incident is estimated to cause a loss of $50,000 and is expected to occur 0.2 times per year:ALE = $50,000 × 0.2 = $10,000This type of calculation can help organizations compare the expected cost of risk against the cost of implementing additional controls.5. Qualitative vs. Quantitative AssessmentBoth approaches can be useful, depending on the available information and the organization's objectives.QualitativeLow / Medium / HighUseful when:
- Data is limited.
- Rapid prioritization is required.
- Precise financial information is unavailable.
- Large numbers of risks must be assessed.
QuantitativeNumerical / Financial EstimatesUseful when:
- Financial data is available.
- Security investments require economic justification.
- Management needs to compare expected losses with control costs.
- More detailed financial analysis is appropriate.
Organizations may also combine both approaches rather than treating them as mutually exclusive.6. Choosing a Risk ResponseOnce risk has been assessed, the organization must determine how to respond.Four fundamental strategies are:
- Risk Acceptance
- Risk Avoidance
- Risk Mitigation
- Risk Transference
The appropriate strategy depends on the organization's risk tolerance, business requirements, available resources, and the characteristics of the specific risk.7. Risk AcceptanceRisk acceptance means knowingly retaining a risk.An organization may accept a risk when:
- The likelihood is low.
- The potential impact is limited.
- Existing controls provide sufficient protection.
- The cost of additional controls exceeds the expected benefit.
- The risk falls within the organization's defined tolerance.
Acceptance should be an informed management decision rather than simply ignoring a security issue.8. Risk AvoidanceRisk avoidance eliminates the activity or condition responsible for the risk.For example, an organization may decide not to deploy a particular service if the associated risk cannot be reduced to an acceptable level.Avoidance can therefore involve:Stop the activity → Eliminate the exposure → Eliminate the associated riskThis approach may be appropriate when the activity is not essential to business operations or when the risk cannot be adequately controlled.9. Risk MitigationRisk mitigation reduces the likelihood or impact of a risk by implementing appropriate security controls.Examples include:
- Firewalls.
- Endpoint protection.
- IDS/IPS.
- Network segmentation.
- Encryption.
- Multi-factor authentication.
- Vulnerability remediation.
- Security monitoring.
- Backup and recovery mechanisms.
Mitigation does not necessarily eliminate the risk completely.Instead, it aims to reduce the remaining exposure to a level that the organization considers acceptable.10. Risk TransferenceRisk transference shifts some of the financial or operational consequences of a risk to another party.Examples can include:
- Cybersecurity insurance.
- Outsourcing selected services.
- Contractual agreements.
- Service-level agreements.
- Third-party providers.
Risk transference does not necessarily eliminate the underlying threat or vulnerability.For example, an organization may transfer some financial consequences through insurance while still needing to maintain appropriate security controls.11. Understanding Security ControlsSecurity controls are safeguards designed to reduce risk.Controls can address different parts of the security lifecycle, including:
- Prevention.
- Detection.
- Response.
- Recovery.
The objective is not necessarily to eliminate every possible threat, but to reduce risk to a level consistent with organizational requirements.12. Technical Security ControlsTechnical controls are implemented through technology.Examples include:FirewallsControl network traffic according to defined security policies.Antivirus and Endpoint ProtectionDetect and respond to malicious software and suspicious activity.IDS/IPSMonitor network traffic and can identify or block suspicious activity.EncryptionProtects information from unauthorized disclosure and can help preserve confidentiality.Access-Control TechnologiesRestrict access to systems and resources based on defined permissions and authentication requirements.Technical controls provide automated or technology-driven protection across the environment.13. Operational Security ControlsSecurity is not purely a technical problem.Operational controls address how people and processes manage security.Examples include:
- Security policies.
- Standard operating procedures.
- Vulnerability management programs.
- Penetration testing.
- Security awareness training.
- Change-management procedures.
- Incident-response processes.
- Access reviews.
These controls establish consistent processes for operating and maintaining the organization's security program.14. Combining Technical and Operational Cont
You can listen and download our episodes for free on more than 10 different platforms:
https://linktr.ee/cybercode_academy
links1