CyberCode Academy · Yesterday · 21 min
Course 46 - CompTIA Cybersecurity Analyst | Episode 16: Mastering CVSS
0:00-21:04
transcript
show notes
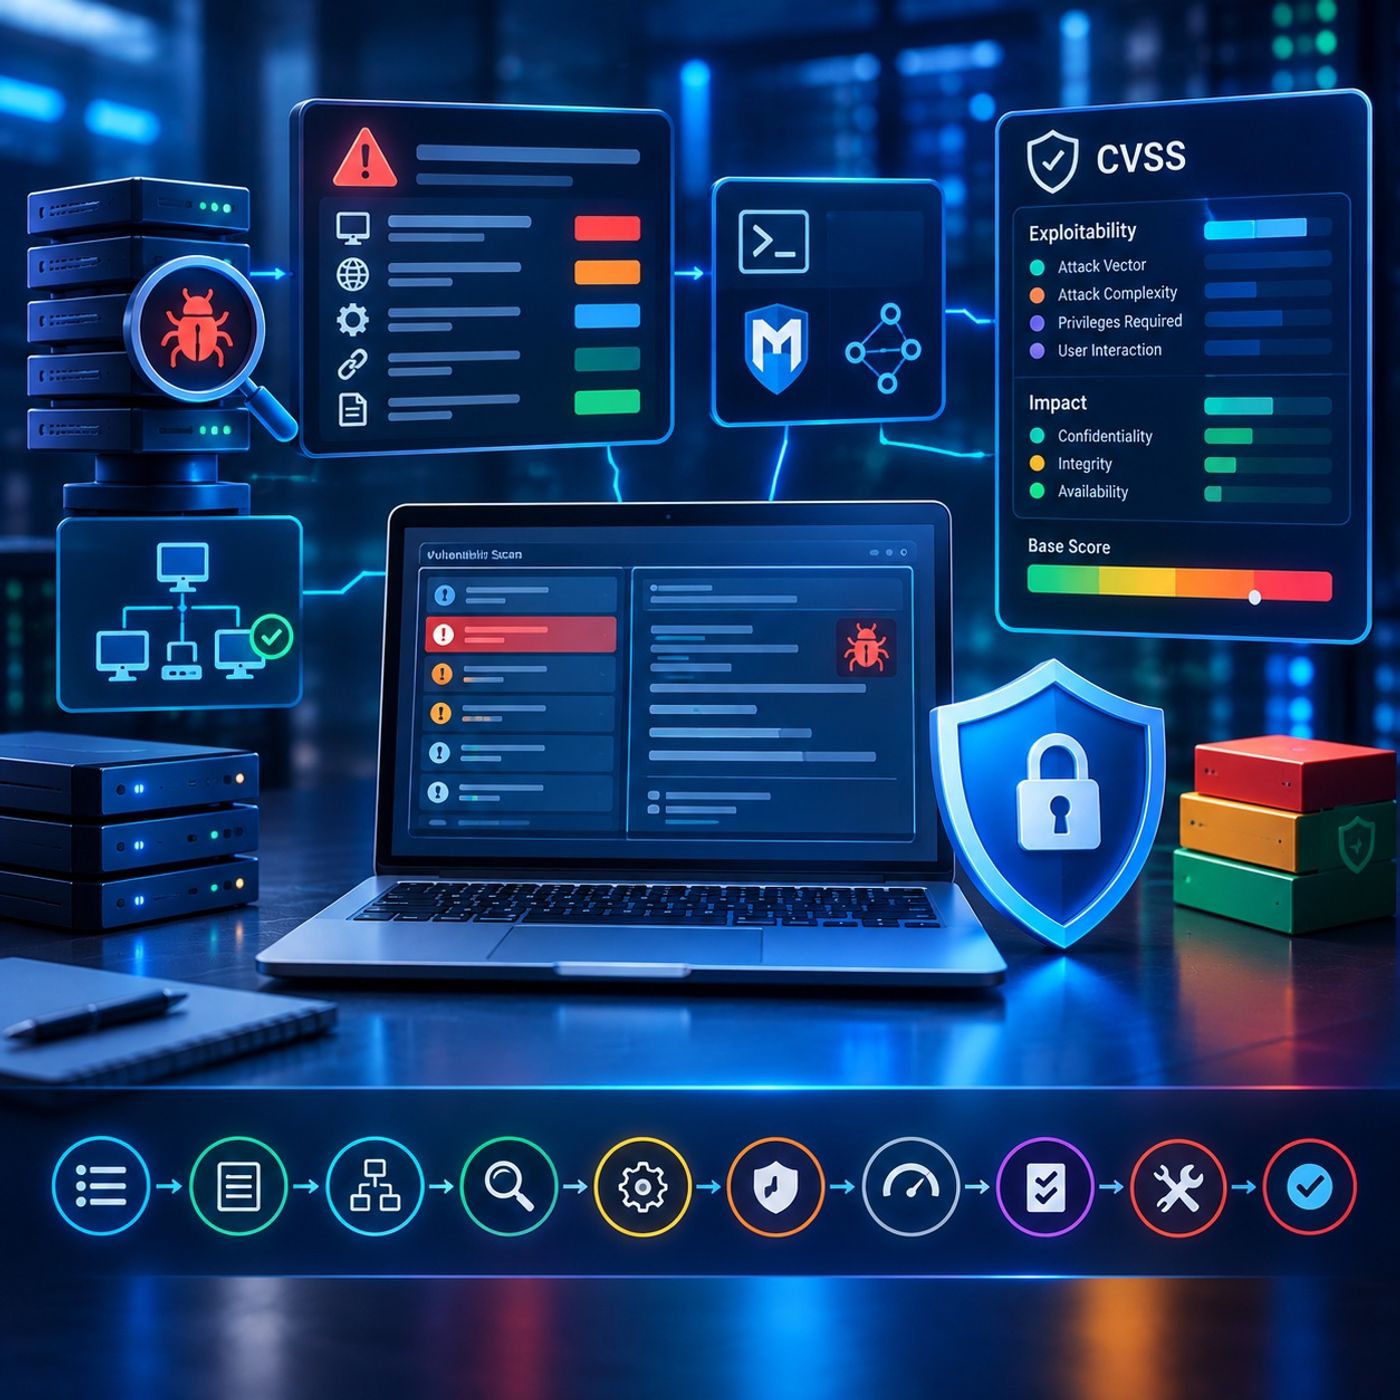
Episode OverviewThis episode provides a structured guide to vulnerability management, showing how security analysts move from raw vulnerability scanner findings to validated vulnerabilities and standardized risk ratings.The episode begins with the practical interpretation of scanner reports, using tools such as Nessus to examine vulnerability descriptions, affected hosts, exploitability information, and supporting references. It then explores how analysts investigate the underlying cause of a finding, assess whether exploitation is feasible, identify relevant exploitation frameworks such as Metasploit, and isolate affected systems for controlled remediation.The episode then introduces the Common Vulnerability Scoring System (CVSS), explaining how standardized metrics describe the characteristics and potential impact of a vulnerability. The discussion covers exploitability factors such as attack vector, attack complexity, and authentication requirements, alongside the confidentiality, integrity, and availability impacts used to evaluate consequences.Finally, the episode examines how CVSS base scores are calculated and how the resulting numerical score is mapped to standardized severity categories.Key Topics Covered1. Interpreting Vulnerability Scanner ReportsVulnerability scanners generate large volumes of technical findings, but scanner output alone does not constitute a complete risk assessment. Analysts must interpret and validate the information before determining the appropriate remediation strategy.Key report elements include:
You can listen and download our episodes for free on more than 10 different platforms:
https://linktr.ee/cybercode_academy
- Vulnerability synopsis and summary
- Detailed technical descriptions
- Affected hosts and IP addresses
- Affected services, ports, or applications
- Exploitability information
- References to known vulnerabilities and security advisories
- Available exploitation or proof-of-concept references
- Recommended remediation actions
- Vulnerable software versions
- Missing security patches
- Configuration weaknesses
- Exposed network services
- Authentication requirements
- Available exploit techniques
- Existing security controls and compensating controls
- Review the scanner finding.
- Identify affected IP addresses or hostnames.
- Determine the vulnerable service or application.
- Validate the finding where appropriate.
- Assess the host's business and security context.
- Isolate or restrict the affected system when necessary.
- Apply the appropriate remediation.
- Verify that the vulnerability has been resolved.
- Attack Vector — how the attacker reaches the vulnerable component.
- Attack Complexity — how difficult exploitation is under the required conditions.
- Privileges Required — the level of access needed before exploitation.
- User Interaction — whether interaction from another user is required.
- Confidentiality — whether sensitive information can be disclosed.
- Integrity — whether information or systems can be modified.
- Availability — whether systems or services can become unavailable or degraded.
- How the vulnerability is reached
- Whether exploitation requires special conditions
- Whether privileges or user interaction are required
- The potential confidentiality impact
- The potential integrity impact
- The potential availability impact
- Exploitability — characteristics describing how the vulnerability can be exploited.
- Impact — the potential consequences of successful exploitation.
- Scanner reports provide technical findings that require analyst interpretation.
- Vulnerability descriptions, affected hosts, services, references, and exploitability information are important components of assessment.
- Exploitability should be evaluated in the context of the actual environment and available security controls.
- CVSS provides a standardized framework for describing vulnerability severity.
- CVSS incorporates both exploitability characteristics and potential impact.
- Confidentiality, integrity, and availability form the core impact dimensions.
- CVSS vector strings provide a compact representation of the underlying scoring metrics.
- CVSS formulas and severity thresholds are version-specific, so the applicable CVSS specification should always be used.
- A numerical severity score is an important input to vulnerability prioritization, but it should be considered alongside asset criticality, exposure, business impact, threat intelligence, and compensating controls.
- Effective vulnerability management ultimately connects technical findings to validated risk, remediation, and verification.
You can listen and download our episodes for free on more than 10 different platforms:
https://linktr.ee/cybercode_academy
links1