CyberCode Academy · October 7 · 23 min
Course 45 - IE Data Center Network Design | Episode 5: Virtual Routing, Multi-Tenancy & Data Center Management Design
0:00-23:06
transcript
show notes
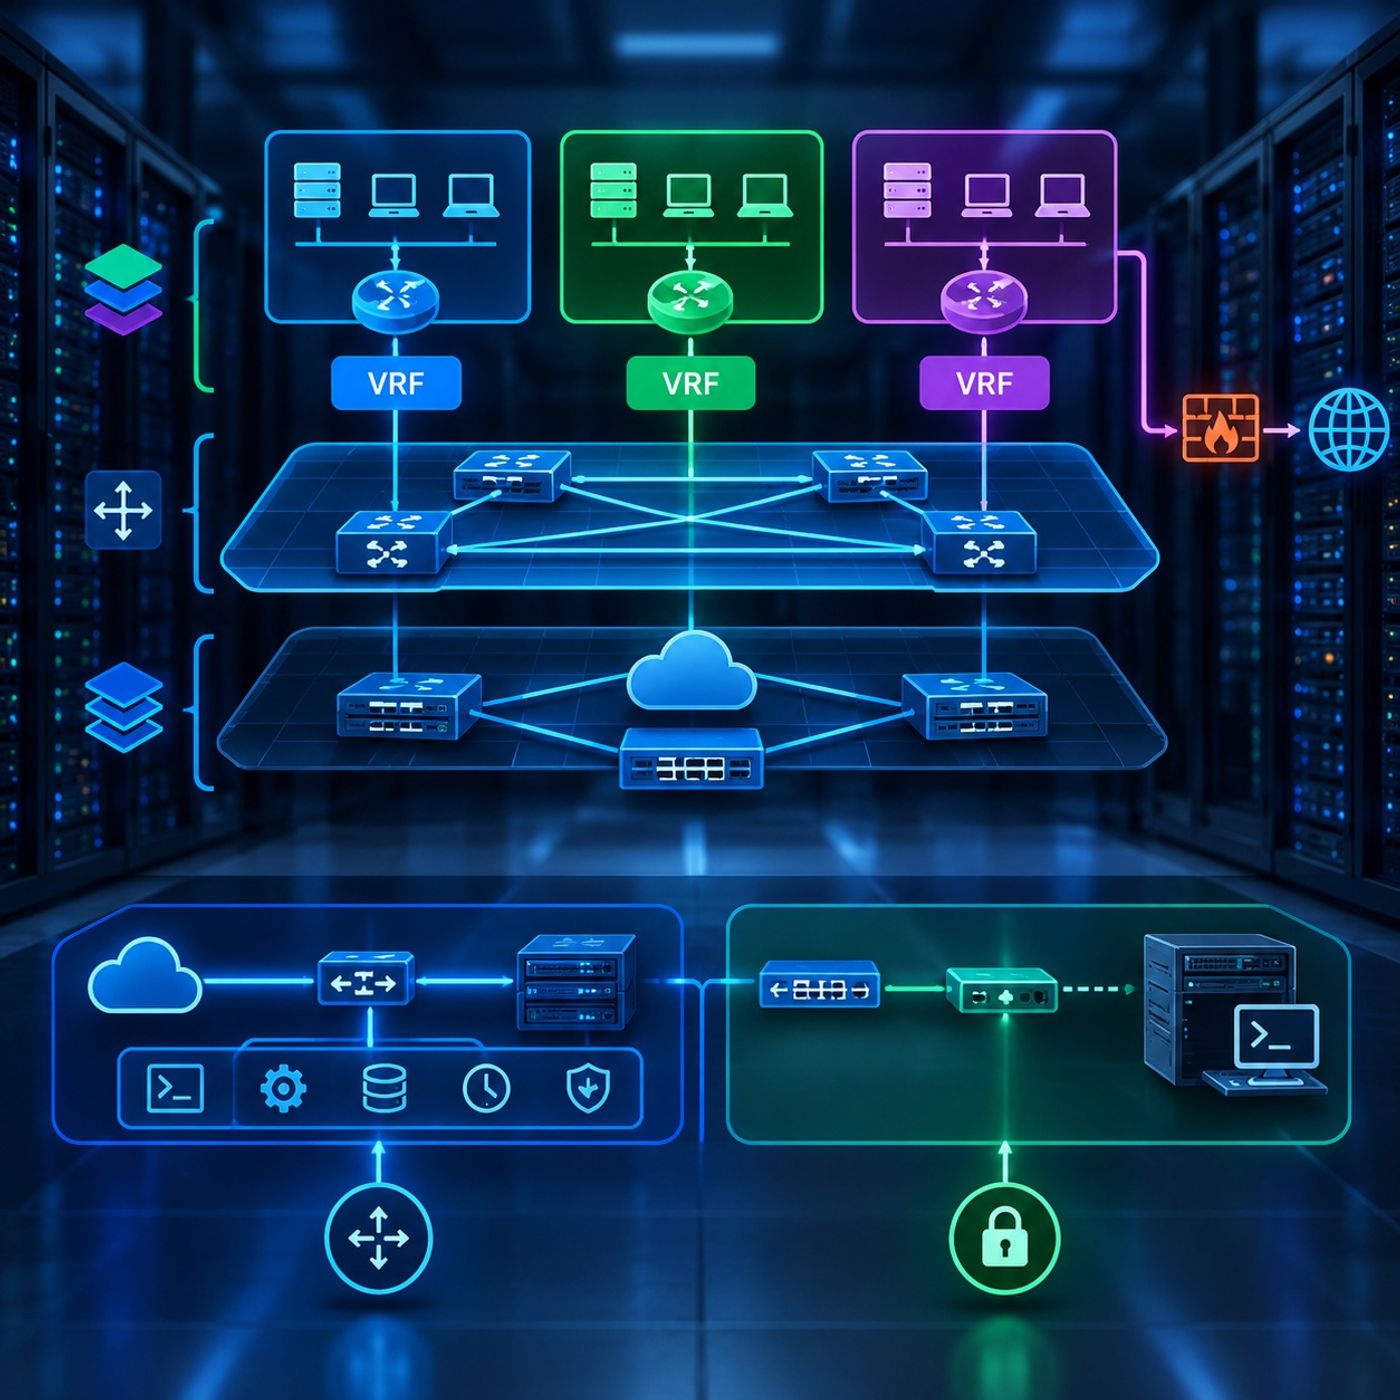
Data Center Virtualization and Secure Management ArchitectureEpisode OverviewModern data centers must provide both strong network isolation and reliable administrative access.In this episode, we explore two foundational aspects of data center architecture: Layer 3 network virtualization with Virtual Routing and Forwarding (VRF) and secure infrastructure management through inband and Out-of-Band (OOB) architectures.We begin by examining how VRFs transform a physical routing platform into multiple logically independent routing environments. We then apply these concepts to VXLAN EVPN fabrics, where VRFs provide tenant isolation while keeping overlay traffic separate from the underlying infrastructure network.The second part moves from data-plane architecture to infrastructure administration. We compare inband management with dedicated OOB management and examine how management VRFs, dedicated management interfaces, console access, and terminal servers provide resilient access to critical infrastructure—even when the production network is unavailable.Part I: Layer 3 Network Virtualization with VRF1. Understanding Virtual Routing and ForwardingVirtual Routing and Forwarding (VRF) allows a single physical router or Layer 3 switch to maintain multiple independent routing tables.Instead of every interface and route belonging to one global routing table, individual interfaces can be associated with separate VRF instances.Conceptually:One Physical Device → Multiple Logical RoutersEach VRF can maintain its own:
- Interfaces.
- Routing table.
- Default routes.
- Dynamic routing relationships.
- Layer 3 forwarding decisions.
This provides logical separation without requiring a separate physical router for every tenant or network environment.2. VRF and Multi-Tenant Network IsolationOne of the most important applications of VRF is multi-tenancy.Consider a data center hosting multiple customers or organizational environments. Each tenant may require independent IP addressing and routing policies.VRFs allow these environments to coexist on the same physical infrastructure while keeping their routing information logically separated.The architecture can be represented as:Physical Network Device→ Tenant VRF A
→ Tenant VRF B
→ Tenant VRF CEach tenant maintains an independent Layer 3 forwarding context.This prevents routes belonging to one tenant from automatically appearing in another tenant's routing table.3. VRF LightTraditional large-scale service-provider architectures may use technologies such as MPLS to provide sophisticated VPN segmentation.VRF Lite provides a simpler approach when MPLS is not required.VRF Lite allows administrators to create multiple isolated routing domains directly on supported network devices.It can be useful in:
- Enterprise networks.
- Data center environments.
- Multi-tenant deployments.
- Network virtualization projects.
- Segmented infrastructure designs.
The primary objective is straightforward:Provide independent routing tables without requiring an MPLS-based VPN architecture.4. VRF in VXLAN EVPN FabricsVRFs become particularly important in modern VXLAN EVPN data centers.A VXLAN EVPN fabric generally contains two conceptual network layers:UnderlayThe routed infrastructure that provides transport between fabric devices.It may use technologies such as:
- OSPF.
- BGP.
- PIM.
- ECMP.
OverlayThe logical tenant network built on top of the underlay.Tenant VRFs provide independent Layer 3 routing environments within this overlay.This separation means that infrastructure routing and tenant routing can operate independently.Conceptually:Underlay Routing → VXLAN Transport → Tenant VRF → Tenant Networks5. Separating Tenant and Infrastructure RoutingA major advantage of VRF-based segmentation is the ability to prevent tenant traffic from interfering with the infrastructure control plane.For example, underlay routing protocols such as OSPF or multicast-related infrastructure mechanisms such as PIM operate within the infrastructure context.Tenant routes remain within their corresponding VRFs.This creates a layered architecture:Infrastructure VRF / Global Routing Context→ Fabric Transport→ Tenant VRF 1→ Tenant VRF 2→ Tenant VRF 3This separation improves organization, scalability, and control over routing policies.6. Border Leaf HandoffsTenant networks eventually need to communicate with resources outside the VXLAN fabric.This may include:
- Internet connectivity.
- External enterprise networks.
- WAN routers.
- Firewalls.
- Load balancers.
- Other data centers.
Border leaf switches can provide these external handoff points.The important architectural principle is that the tenant's VRF remains associated with the appropriate external routing context.Traffic can therefore leave the VXLAN fabric without losing the logical segmentation established inside the overlay.The workflow becomes:Tenant VRF → Border Leaf → External Router / Security Service → External NetworkPart II: Secure Data Center Management Architecture7. Understanding Inband ManagementManagement traffic can travel through the same production network used by application and data traffic.This is known as inband management.Common management protocols include:
- SSH.
- SNMP.
- Syslog.
- NTP.
- TACACS+.
- API-based management.
The advantage is simplicity.Because management traffic uses the existing production infrastructure, organizations may require fewer physical connections and less dedicated cabling.However, this introduces an important dependency:If the production network fails, management access may fail with it.8. The Risks of Inband ManagementInband management creates a shared fate between the management plane and production network.A routing failure, switching failure, security incident, or configuration error affecting the production network may also prevent administrators from reaching the affected devices.This can become especially problematic during incidents.The very infrastructure that needs to be repaired may be the infrastructure preventing administrators from accessing it.Therefore, inband management should be evaluated not only for convenience, but also for:
- Availability.
- Security.
- Failure-domain dependency.
- Incident-response requirements.
- Operational recovery.
9. Out-of-Band ManagementOut-of-Band (OOB) management separates infrastructure administration from the production data plane.Instead of relying exclusively on production interfaces, devices can use dedicated management interfaces connected to an independent management network.On supported Cisco platforms, a dedicated interface such as:management 0can provide management connectivity.The resulting architecture creates two separate paths:Production Network → Application and Data TrafficOOB Network → Infrastructure ManagementIf the production network experiences an outage, administrators may still be able to reach the affected device through the OOB network.10. Management VRFsA dedicated management VRF can provide additional logical separation for administrative traffic.Management services such as:
- SSH.
- SNMP.
- Syslog.
- NTP.
- TACACS+.
can be associated with the management routing context rather than sharing the tenant or production routing environment.This creates another layer of isolation:Production VRFs ≠ Tenant VRFs ≠ Management VRFThe exact VRF architecture depends on the platform and deployment requirements, but the underlying principle is consistent:Management traffic should have a clearly defined security and routing boundary.11. Console Access and Terminal ServersNetwork connectivity is not always sufficient for resilient management.When a switch or router has a severe configuration, routing, or software problem, even its management interface may become unreachable.This is where console access becomes important.A terminal server can provide remote access to the physical console ports of multiple network devices.The architecture can provide:Administrator → Terminal Server → Console Port → Network DeviceThis is particularly valuable for lights-out management, allowing administrators to recover infrastructure remotely even when normal IP-based management is unavailable.12. Management Architecture for Cisco NexusCisco Nexus environments can combine multiple management mechanisms.A resilient design may include:
- Dedicated management interfaces.
- Management VRFs.
- SSH access.
- AAA and TACACS+ integration.
- SNMP monitoring.
- Centralized Syslog.
- NTP synchronization.
- Console access.
- Remote terminal-server connectivity.
The objective is to ensure that operational management remains available while maintaining strong separation from application traffic.13. Management Architecture for Cisco UCSThe same principles apply to Cisco UCS B-Series environments.Management architecture must account for both the computing infrastructure and its associated network connectivity.Dedicated management paths can provide administrative access to the UCS environment even when production application traffic is experiencing an outage.The management design should therefore consider:
- Management interfaces.
- Control-plane access.
- Authentication services.
-
You can listen and download our episodes for free on more than 10 different platforms:
https://linktr.ee/cybercode_academy
- Interfaces.
- Routing table.
- Default routes.
- Dynamic routing relationships.
- Layer 3 forwarding decisions.
This provides logical separation without requiring a separate physical router for every tenant or network environment.2. VRF and Multi-Tenant Network IsolationOne of the most important applications of VRF is multi-tenancy.Consider a data center hosting multiple customers or organizational environments. Each tenant may require independent IP addressing and routing policies.VRFs allow these environments to coexist on the same physical infrastructure while keeping their routing information logically separated.The architecture can be represented as:Physical Network Device→ Tenant VRF A
→ Tenant VRF B
→ Tenant VRF CEach tenant maintains an independent Layer 3 forwarding context.This prevents routes belonging to one tenant from automatically appearing in another tenant's routing table.3. VRF LightTraditional large-scale service-provider architectures may use technologies such as MPLS to provide sophisticated VPN segmentation.VRF Lite provides a simpler approach when MPLS is not required.VRF Lite allows administrators to create multiple isolated routing domains directly on supported network devices.It can be useful in:
- Enterprise networks.
- Data center environments.
- Multi-tenant deployments.
- Network virtualization projects.
- Segmented infrastructure designs.
The primary objective is straightforward:Provide independent routing tables without requiring an MPLS-based VPN architecture.4. VRF in VXLAN EVPN FabricsVRFs become particularly important in modern VXLAN EVPN data centers.A VXLAN EVPN fabric generally contains two conceptual network layers:UnderlayThe routed infrastructure that provides transport between fabric devices.It may use technologies such as:
- OSPF.
- BGP.
- PIM.
- ECMP.
OverlayThe logical tenant network built on top of the underlay.Tenant VRFs provide independent Layer 3 routing environments within this overlay.This separation means that infrastructure routing and tenant routing can operate independently.Conceptually:Underlay Routing → VXLAN Transport → Tenant VRF → Tenant Networks5. Separating Tenant and Infrastructure RoutingA major advantage of VRF-based segmentation is the ability to prevent tenant traffic from interfering with the infrastructure control plane.For example, underlay routing protocols such as OSPF or multicast-related infrastructure mechanisms such as PIM operate within the infrastructure context.Tenant routes remain within their corresponding VRFs.This creates a layered architecture:Infrastructure VRF / Global Routing Context→ Fabric Transport→ Tenant VRF 1→ Tenant VRF 2→ Tenant VRF 3This separation improves organization, scalability, and control over routing policies.6. Border Leaf HandoffsTenant networks eventually need to communicate with resources outside the VXLAN fabric.This may include:
- Internet connectivity.
- External enterprise networks.
- WAN routers.
- Firewalls.
- Load balancers.
- Other data centers.
Border leaf switches can provide these external handoff points.The important architectural principle is that the tenant's VRF remains associated with the appropriate external routing context.Traffic can therefore leave the VXLAN fabric without losing the logical segmentation established inside the overlay.The workflow becomes:Tenant VRF → Border Leaf → External Router / Security Service → External NetworkPart II: Secure Data Center Management Architecture7. Understanding Inband ManagementManagement traffic can travel through the same production network used by application and data traffic.This is known as inband management.Common management protocols include:
- SSH.
- SNMP.
- Syslog.
- NTP.
- TACACS+.
- API-based management.
The advantage is simplicity.Because management traffic uses the existing production infrastructure, organizations may require fewer physical connections and less dedicated cabling.However, this introduces an important dependency:If the production network fails, management access may fail with it.8. The Risks of Inband ManagementInband management creates a shared fate between the management plane and production network.A routing failure, switching failure, security incident, or configuration error affecting the production network may also prevent administrators from reaching the affected devices.This can become especially problematic during incidents.The very infrastructure that needs to be repaired may be the infrastructure preventing administrators from accessing it.Therefore, inband management should be evaluated not only for convenience, but also for:
- Availability.
- Security.
- Failure-domain dependency.
- Incident-response requirements.
- Operational recovery.
9. Out-of-Band ManagementOut-of-Band (OOB) management separates infrastructure administration from the production data plane.Instead of relying exclusively on production interfaces, devices can use dedicated management interfaces connected to an independent management network.On supported Cisco platforms, a dedicated interface such as:management 0can provide management connectivity.The resulting architecture creates two separate paths:Production Network → Application and Data TrafficOOB Network → Infrastructure ManagementIf the production network experiences an outage, administrators may still be able to reach the affected device through the OOB network.10. Management VRFsA dedicated management VRF can provide additional logical separation for administrative traffic.Management services such as:
- SSH.
- SNMP.
- Syslog.
- NTP.
- TACACS+.
can be associated with the management routing context rather than sharing the tenant or production routing environment.This creates another layer of isolation:Production VRFs ≠ Tenant VRFs ≠ Management VRFThe exact VRF architecture depends on the platform and deployment requirements, but the underlying principle is consistent:Management traffic should have a clearly defined security and routing boundary.11. Console Access and Terminal ServersNetwork connectivity is not always sufficient for resilient management.When a switch or router has a severe configuration, routing, or software problem, even its management interface may become unreachable.This is where console access becomes important.A terminal server can provide remote access to the physical console ports of multiple network devices.The architecture can provide:Administrator → Terminal Server → Console Port → Network DeviceThis is particularly valuable for lights-out management, allowing administrators to recover infrastructure remotely even when normal IP-based management is unavailable.12. Management Architecture for Cisco NexusCisco Nexus environments can combine multiple management mechanisms.A resilient design may include:
- Dedicated management interfaces.
- Management VRFs.
- SSH access.
- AAA and TACACS+ integration.
- SNMP monitoring.
- Centralized Syslog.
- NTP synchronization.
- Console access.
- Remote terminal-server connectivity.
The objective is to ensure that operational management remains available while maintaining strong separation from application traffic.13. Management Architecture for Cisco UCSThe same principles apply to Cisco UCS B-Series environments.Management architecture must account for both the computing infrastructure and its associated network connectivity.Dedicated management paths can provide administrative access to the UCS environment even when production application traffic is experiencing an outage.The management design should therefore consider:
- Management interfaces.
- Control-plane access.
- Authentication services.
-
You can listen and download our episodes for free on more than 10 different platforms:
https://linktr.ee/cybercode_academy
links1