Skip to content
Artwork for CyberCode Academy
CyberCode Academy · September 23 · 22 min

Course 44 - RH Security Specialist | Episode 3: From Standards to LUKS Encryption

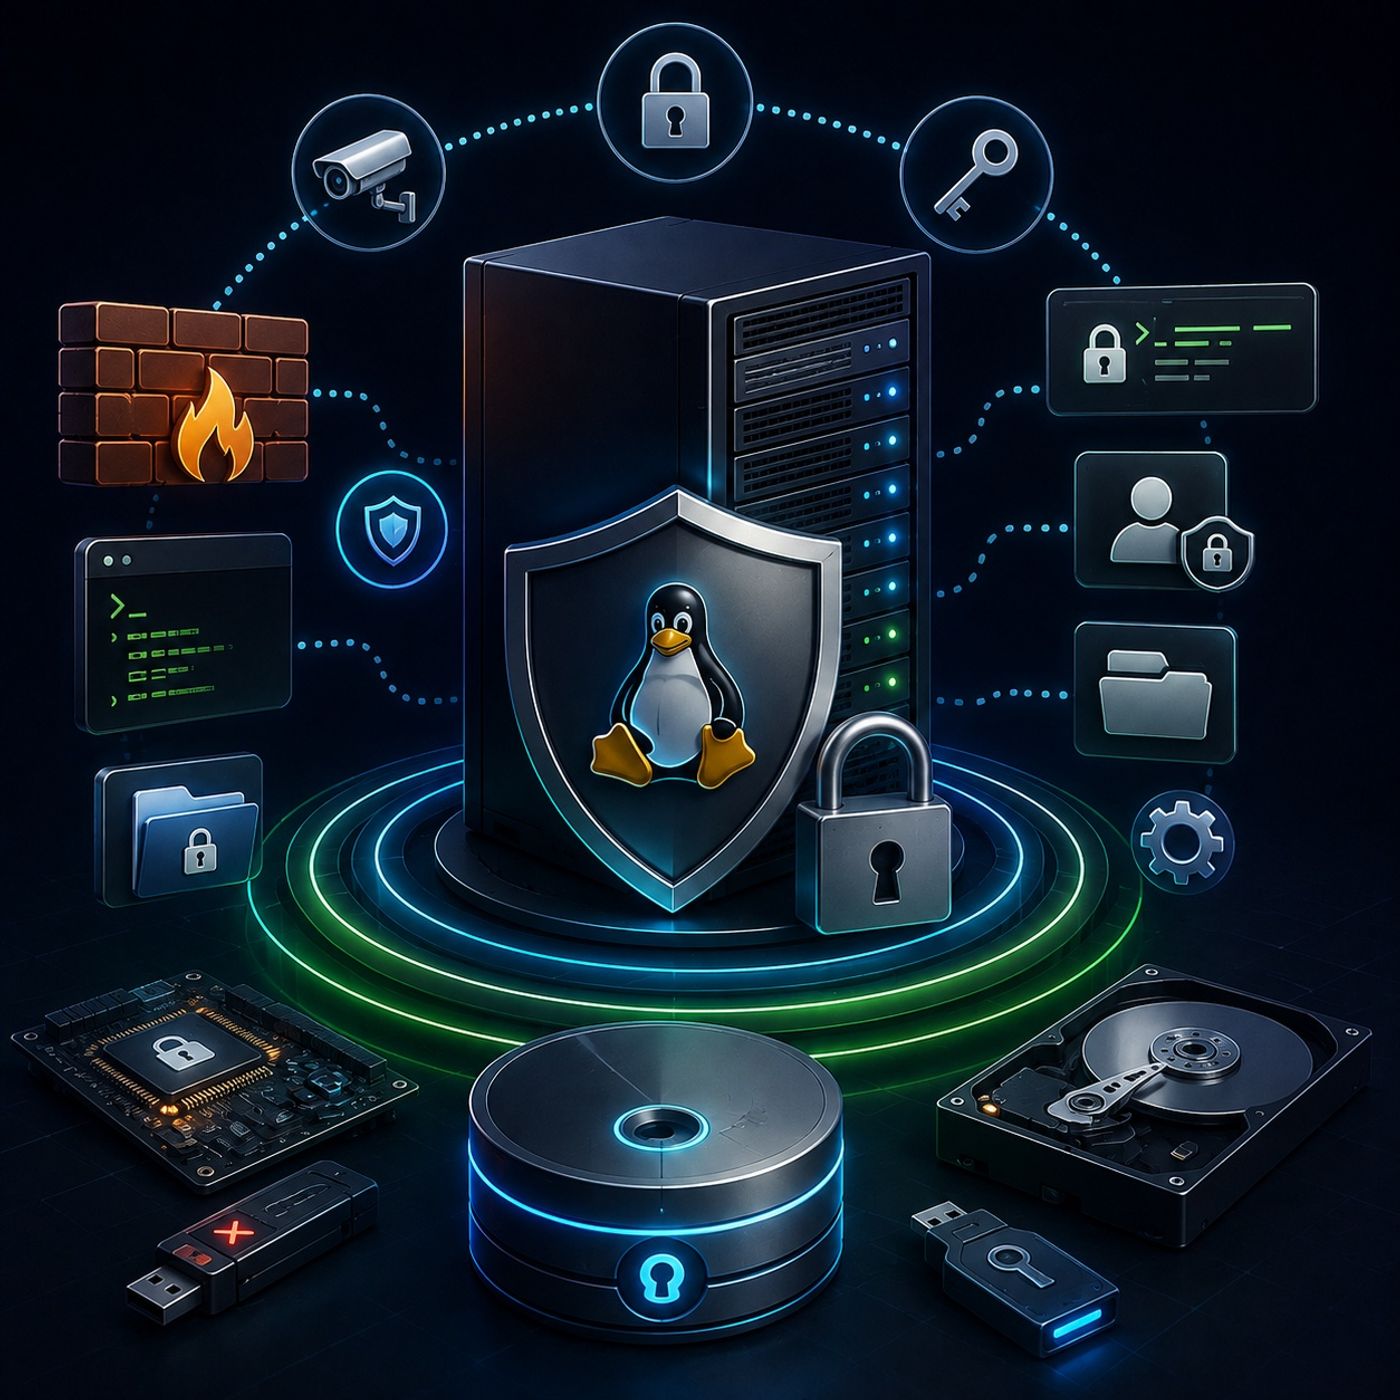
A secure Linux server begins with more than a hardened configuration file. Enterprise security requires a layered approach that protects the system from physical tampering, unauthorized remote access, insecure services, filesystem abuse, and exposure of sensitive data.In this episode, we move from fundamental operating system hardening to advanced protection for data at rest. We examine how administrators can establish a secure server baseline, strengthen remote administration, safely manage system services, and use Linux Unified Key Setup (LUKS) to protect sensitive storage.The episode emphasizes a core security principle throughout: no single security control is sufficient on its own. Effective server security comes from multiple complementary layers.1. Physical and Environmental SecuritySecurity begins at the physical layer.Even a carefully configured Linux server can be compromised if an unauthorized individual can physically access the machine. We examine practical controls designed to prevent unauthorized interaction with the underlying hardware.Key topics include: Restricting physical access to server systems. Protecting the BIOS configuration. Preventing unauthorized booting from external or removable media. Understanding why physical access can undermine otherwise strong operating system controls. Designing storage layouts that isolate critical filesystem areas. We also explore why separate disk partitions are an important administrative consideration. Isolating areas such as user data and system files can help prevent one filesystem from consuming all available storage and causing broader service disruption.2. Establishing a Linux Hardening BaselineOnce physical access is controlled, the operating system itself must be hardened.We examine several foundational controls that can significantly reduce the attack surface of an enterprise Linux server.Host-Based Firewall ProtectionA local server firewall provides an additional defensive layer by controlling which network connections are permitted to reach the system.This is particularly important in environments where threats may originate from within the same broader network rather than exclusively from the public Internet.Identifying World-Writable DirectoriesWe also examine the security implications of directories that allow broad write access.World-writable locations can introduce opportunities for unauthorized file manipulation, making it important for administrators to identify and evaluate these permissions as part of a regular security assessment.The Sticky BitThe sticky bit provides an additional filesystem-level protection mechanism for shared writable directories.It helps ensure that users cannot arbitrarily delete or rename files belonging to other users, even when the directory itself is writable by multiple accounts.Together, these controls establish a stronger baseline for filesystem and network security.3. Hardening SSH and Remote AdministrationRemote administration is one of the most important areas to secure because SSH frequently represents a primary management interface for Linux infrastructure.The episode explores several SSH hardening practices, including: Enforcing modern SSH protocol configurations. Disabling direct remote root logins. Using sudo for controlled administrative operations. Maintaining traceable administrative activity through privilege escalation logging. Configuring appropriate legal and administrative login banners. The objective is not simply to make remote access more restrictive, but to make administrative activity more accountable, auditable, and controlled.Instead of allowing administrators to connect directly as root, controlled privilege escalation provides better visibility into who performed administrative actions.4. Managing Legacy and Unnecessary ServicesEvery enabled service increases the complexity and potential attack surface of a server.We examine the process of identifying unnecessary or legacy services and discuss why removing them must be approached carefully.A key lesson involves package dependencies.Removing a seemingly unnecessary service can sometimes cause other components to be removed as dependencies. A classic example is the relationship between mail-related packages and scheduling utilities such as cron.This demonstrates why administrators should: Identify package dependencies before removal. Understand which system components rely on a package. Avoid blindly removing services based solely on their names. Verify critical system functionality after package changes. The goal is to minimize the attack surface without accidentally removing essential operating system functionality.5. Protecting Data at Rest with LUKSThe final section moves from system hardening to protecting the information stored on the server.Even if an attacker cannot remotely access a running system, physical access to storage media can expose sensitive information if the data is stored unencrypted.We therefore introduce Linux Unified Key Setup (LUKS) and the cryptsetup utility for encrypted block-device management.The workflow covers:Preparing Sensitive StorageBefore encryption is established, sensitive storage must be handled carefully to avoid leaving recoverable unencrypted remnants.The episode discusses preparing and isolating the target partition and using secure storage-clearing procedures where appropriate.Initializing the Encrypted VolumeWe then examine the process of initializing a LUKS-protected volume and establishing its encrypted container.Mapping the Encrypted DeviceUsing cryptsetup, the encrypted volume can be mapped into the operating system so that authorized users and services can interact with the decrypted filesystem through the appropriate device mapping.Persistent ConfigurationFor systems that must retain their encrypted storage configuration across reboots, we examine the relationship between: /etc/crypttab /etc/fstab Encrypted device mappings Filesystem mounting Security contexts Correct configuration ensures that encrypted storage can be integrated into the normal Linux boot and filesystem workflow.6. Maintaining SELinux CompatibilityEncryption and filesystem configuration must also coexist correctly with SELinux.We examine why security contexts matter when creating or mounting filesystems and why administrators must ensure that encrypted storage remains compatible with the system's mandatory access control policies.This reinforces an important concept: implementing one security mechanism should not unintentionally break another.A hardened Linux server must maintain consistency across:Filesystem Permissions → Encryption → Mount Configuration → SELinux Contexts → Application Access7. The Layered Enterprise Security ModelThe techniques covered throughout the episode can be viewed as multiple defensive layers:Physical Security ↓ Boot and Hardware Protection ↓ Filesystem and Permission Hardening ↓ Host-Based Firewall ↓ SSH and Privilege Management ↓ Service Reduction ↓ Encryption at Rest ↓ SELinux EnforcementIf one layer is bypassed, additional controls remain available to limit the impact.This layered approach is the foundation of effective enterprise server hardening.Key TakeawaysBy the end of this episode, you will understand: Why physical security is an essential component of Linux server security. How BIOS and bootloader protections can reduce unauthorized physical access risks. Why separating critical filesystem areas can improve system resilience. How host-based firewalls provide an additional network security layer. How to identify world-writable directories and understand their security implications. How the sticky bit protects files within shared writable directories. How to strengthen SSH-based remote administration. Why direct remote root access should generally be disabled. How sudo improves administrative accountability and traceability. Why unnecessary services should be removed carefully. How package dependencies can affect seemingly unrelated system components. How LUKS provides encryption for sensitive data at rest. The role of cryptsetup, crypttab, and fstab in encrypted storage management. Why SELinux contexts must be considered when integrating encrypted filesystems. How multiple security controls combine to create a hardened enterprise Linux environment. Final PerspectiveEnterprise Linux security is not achieved through a single configuration change. It is the result of layered protection applied consistently across the physical system, operating system, network services, user privileges, filesystems, and stored data.By combining strong access controls, careful service management, filesystem hardening, firewall protection, and LUKS-based encryption, administrators can move significantly beyond the default operating system configuration and build a more resilient enterprise server platform.The ultimate objective is simple:Reduce the attack surface, protect sensitive information, maintain accountability, and ensure that every security layer reinforces the others. You can listen and download our episodes for free on more than 10 different platforms: https://linktr.ee/cybercode_academy

0:00-22:54

transcript

No transcript — this publisher did not publish one.

show notes

A secure Linux server begins with more than a hardened configuration file. Enterprise security requires a layered approach that protects the system from physical tampering, unauthorized remote access, insecure services, filesystem abuse, and exposure of sensitive data.In this episode, we move from fundamental operating system hardening to advanced protection for data at rest. We examine how administrators can establish a secure server baseline, strengthen remote administration, safely manage system services, and use Linux Unified Key Setup (LUKS) to protect sensitive storage.The episode emphasizes a core security principle throughout: no single security control is sufficient on its own. Effective server security comes from multiple complementary layers.1. Physical and Environmental SecuritySecurity begins at the physical layer.Even a carefully configured Linux server can be compromised if an unauthorized individual can physically access the machine. We examine practical controls designed to prevent unauthorized interaction with the underlying hardware.Key topics include:
  • Restricting physical access to server systems.
  • Protecting the BIOS configuration.
  • Preventing unauthorized booting from external or removable media.
  • Understanding why physical access can undermine otherwise strong operating system controls.
  • Designing storage layouts that isolate critical filesystem areas.
We also explore why separate disk partitions are an important administrative consideration. Isolating areas such as user data and system files can help prevent one filesystem from consuming all available storage and causing broader service disruption.2. Establishing a Linux Hardening BaselineOnce physical access is controlled, the operating system itself must be hardened.We examine several foundational controls that can significantly reduce the attack surface of an enterprise Linux server.Host-Based Firewall ProtectionA local server firewall provides an additional defensive layer by controlling which network connections are permitted to reach the system.This is particularly important in environments where threats may originate from within the same broader network rather than exclusively from the public Internet.Identifying World-Writable DirectoriesWe also examine the security implications of directories that allow broad write access.World-writable locations can introduce opportunities for unauthorized file manipulation, making it important for administrators to identify and evaluate these permissions as part of a regular security assessment.The Sticky BitThe sticky bit provides an additional filesystem-level protection mechanism for shared writable directories.It helps ensure that users cannot arbitrarily delete or rename files belonging to other users, even when the directory itself is writable by multiple accounts.Together, these controls establish a stronger baseline for filesystem and network security.3. Hardening SSH and Remote AdministrationRemote administration is one of the most important areas to secure because SSH frequently represents a primary management interface for Linux infrastructure.The episode explores several SSH hardening practices, including:
  • Enforcing modern SSH protocol configurations.
  • Disabling direct remote root logins.
  • Using sudo for controlled administrative operations.
  • Maintaining traceable administrative activity through privilege escalation logging.
  • Configuring appropriate legal and administrative login banners.
The objective is not simply to make remote access more restrictive, but to make administrative activity more accountable, auditable, and controlled.Instead of allowing administrators to connect directly as root, controlled privilege escalation provides better visibility into who performed administrative actions.4. Managing Legacy and Unnecessary ServicesEvery enabled service increases the complexity and potential attack surface of a server.We examine the process of identifying unnecessary or legacy services and discuss why removing them must be approached carefully.A key lesson involves package dependencies.Removing a seemingly unnecessary service can sometimes cause other components to be removed as dependencies. A classic example is the relationship between mail-related packages and scheduling utilities such as cron.This demonstrates why administrators should:
  • Identify package dependencies before removal.
  • Understand which system components rely on a package.
  • Avoid blindly removing services based solely on their names.
  • Verify critical system functionality after package changes.
The goal is to minimize the attack surface without accidentally removing essential operating system functionality.5. Protecting Data at Rest with LUKSThe final section moves from system hardening to protecting the information stored on the server.Even if an attacker cannot remotely access a running system, physical access to storage media can expose sensitive information if the data is stored unencrypted.We therefore introduce Linux Unified Key Setup (LUKS) and the cryptsetup utility for encrypted block-device management.The workflow covers:Preparing Sensitive StorageBefore encryption is established, sensitive storage must be handled carefully to avoid leaving recoverable unencrypted remnants.The episode discusses preparing and isolating the target partition and using secure storage-clearing procedures where appropriate.Initializing the Encrypted VolumeWe then examine the process of initializing a LUKS-protected volume and establishing its encrypted container.Mapping the Encrypted DeviceUsing cryptsetup, the encrypted volume can be mapped into the operating system so that authorized users and services can interact with the decrypted filesystem through the appropriate device mapping.Persistent ConfigurationFor systems that must retain their encrypted storage configuration across reboots, we examine the relationship between:
  • /etc/crypttab
  • /etc/fstab
  • Encrypted device mappings
  • Filesystem mounting
  • Security contexts
Correct configuration ensures that encrypted storage can be integrated into the normal Linux boot and filesystem workflow.6. Maintaining SELinux CompatibilityEncryption and filesystem configuration must also coexist correctly with SELinux.We examine why security contexts matter when creating or mounting filesystems and why administrators must ensure that encrypted storage remains compatible with the system's mandatory access control policies.This reinforces an important concept: implementing one security mechanism should not unintentionally break another.A hardened Linux server must maintain consistency across:Filesystem Permissions → Encryption → Mount Configuration → SELinux Contexts → Application Access7. The Layered Enterprise Security ModelThe techniques covered throughout the episode can be viewed as multiple defensive layers:Physical Security
↓
Boot and Hardware Protection
↓
Filesystem and Permission Hardening
↓
Host-Based Firewall
↓
SSH and Privilege Management
↓
Service Reduction
↓
Encryption at Rest
↓
SELinux EnforcementIf one layer is bypassed, additional controls remain available to limit the impact.This layered approach is the foundation of effective enterprise server hardening.Key TakeawaysBy the end of this episode, you will understand:
  • Why physical security is an essential component of Linux server security.
  • How BIOS and bootloader protections can reduce unauthorized physical access risks.
  • Why separating critical filesystem areas can improve system resilience.
  • How host-based firewalls provide an additional network security layer.
  • How to identify world-writable directories and understand their security implications.
  • How the sticky bit protects files within shared writable directories.
  • How to strengthen SSH-based remote administration.
  • Why direct remote root access should generally be disabled.
  • How sudo improves administrative accountability and traceability.
  • Why unnecessary services should be removed carefully.
  • How package dependencies can affect seemingly unrelated system components.
  • How LUKS provides encryption for sensitive data at rest.
  • The role of cryptsetup, crypttab, and fstab in encrypted storage management.
  • Why SELinux contexts must be considered when integrating encrypted filesystems.
  • How multiple security controls combine to create a hardened enterprise Linux environment.
Final PerspectiveEnterprise Linux security is not achieved through a single configuration change. It is the result of layered protection applied consistently across the physical system, operating system, network services, user privileges, filesystems, and stored data.By combining strong access controls, careful service management, filesystem hardening, firewall protection, and LUKS-based encryption, administrators can move significantly beyond the default operating system configuration and build a more resilient enterprise server platform.The ultimate objective is simple:Reduce the attack surface, protect sensitive information, maintain accountability, and ensure that every security layer reinforces the others.

You can listen and download our episodes for free on more than 10 different platforms:
https://linktr.ee/cybercode_academy
links1